digital signature

Winsage
September 27, 2026
Windows 11 requires drivers to be digitally signed, a policy aimed at enhancing security by preventing unauthorized code from executing at the kernel level. This requirement, which began with Windows Vista and became mandatory with Windows 10, version 1607, has tightened over the years, especially with the introduction of UEFI Secure Boot and TPM in Windows 11. While this enforcement protects against malware and supports anti-cheat systems in gaming, it limits user autonomy and imposes significant challenges for developers, particularly those working on smaller projects. In contrast, Linux allows users more freedom to modify their systems, though this flexibility can compromise security.
Winsage
July 29, 2026
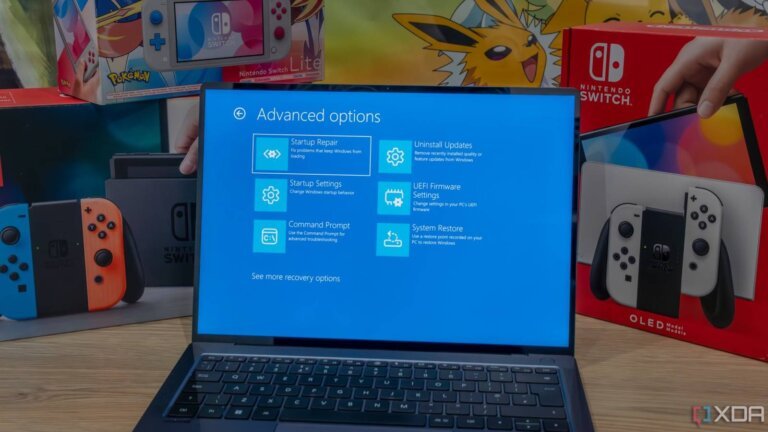
Microsoft reassured Windows 11 and Windows 10 users that their PCs will continue to boot normally and receive updates even if they have not yet received the new Secure Boot 2023 certificates. The rollout of these certificates is expected to continue over the upcoming months. The initial Secure Boot certificate expired on June 24, 2026, and Microsoft has been replacing older 2011 certificates since 2024. The latest update, KB5101650, transitioned Windows 11 to OS builds 26200.8875 and 26100.8875 for versions 25H2 and 24H2, respectively. The 2023 certificates replace older certificates with modern cryptographic standards, allowing Microsoft to deliver DBX revocation updates without interruption. Devices using the 2011 KEK can only receive DBX updates signed with that key, which is no longer valid after June 24. Microsoft has been rolling out the 2023 certificates for the past two years, and many devices remained in a yellow or red status by the June deadline. To check Secure Boot status, users can navigate to Windows Security > Device Security. A green checkmark indicates successful application of the certificates, while yellow and red alerts indicate compatibility issues or firmware incompatibility. PCs that are older or operating in Legacy BIOS mode will not receive the updates. Windows 10 also receives Secure Boot updates, but enrollment in Extended Security Updates (ESU) is required.
AppWizard
May 6, 2026
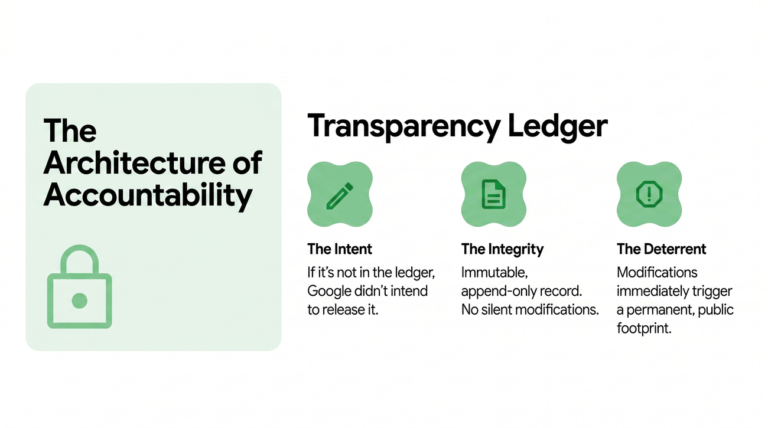
Supply chain attacks targeting mobile software have increased due to the reliance on smartphones for essential functions. In response, Google has launched an enhanced Binary Transparency program for Android, which includes a public ledger that records cryptographic entries for production applications. This program initially covers two software layers: Google Applications and Mainline Modules. For Pixel device owners, it complements the Pixel System Image Transparency feature introduced in 2023, allowing users to verify the authenticity of system images and Google applications. The program aims to address the gap in software trust by distinguishing between digital signatures, which confirm the identity of the binary's creator, and binary transparency, which indicates the intent for public release. If a Google-signed application released after May 1, 2026, is not listed in the ledger, it means Google did not authorize it as production software. Verification tools are available on GitHub for assessing software against the ledger. Google employs "defense-in-depth" protocols to mitigate insider risks, ensuring that no single individual can publish a binary without triggering cryptographic verification. The ledger acts as a public record to deter unauthorized modifications. Google is also working to extend Binary Transparency to third-party developers to enhance the security of the global software supply chain.
AppWizard
April 18, 2026
On April 16, Google released Android 17 Beta 4, concluding its beta phase and focusing on app compatibility and platform stability. Developers must finalize updates for Android 17 to avoid delays when the stable version is released. Key behavioral changes for apps targeting Android 17 include: - Large-screen resizability restrictions, preventing apps from opting out of maintaining orientation, resizability, and aspect ratio constraints. - Expanded restrictions on dynamic code loading, requiring native files loaded via System.load() to be read-only. - Certificate Transparency is enabled by default. - Local network access is restricted by default, with a new ACCESSLOCALNETWORK permission for persistent access. - Stricter rules on background audio interactions, including playback and volume change APIs. Android 17 introduces per-app memory limits based on device RAM to target memory leaks and anomalies, with minimal impact expected on app sessions. Developers can check for memory limit impacts via ApplicationExitInfo and utilize profiling tools in Android Studio Panda. An on-device anomaly detection service monitors resource-intensive behaviors and provides profiling artifacts. Additionally, the Android Keystore now supports ML-DSA for quantum-safe signatures, allowing developers to generate keys and create signatures within secure hardware.
Search