DLL sideloading

Tech Optimizer
September 22, 2026
LastPass has identified a sophisticated scheme targeting users of its Authenticator app, involving SEO poisoning and deceptive GitHub pages that distribute malicious ZIP files disguised as legitimate software. Users searching for "LastPass Authenticator download" may encounter these counterfeit pages, which redirect them to a malicious server delivering a ZIP file containing vsdbg.exe and vsdbg.dll. The executable is a legitimate Microsoft debugging tool exploited to execute the malicious DLL through DLL sideloading, allowing the malware to run undetected. Named Rapuncel by security researchers from Delphos, this malware is undetectable by antivirus engines and targets a hardcoded list of 145 antivirus and endpoint security products, disabling them upon detection. Rapuncel harvests sensitive information, including saved passwords from over 25 web browsers, cryptocurrency wallet files from more than 30 applications, and session tokens from platforms like Discord and Steam. It also captures screenshots and compiles a profile of the infected system, uploading the stolen data to an attacker-controlled server. The malware includes a kernel driver that intercepts web traffic, allowing for advertisement injection and search result manipulation. This campaign has been active for several months, with LastPass vaults remaining unaffected. Users are advised to download applications only from trusted sources. Rapuncel establishes persistence on infected machines by installing itself as a Windows service that starts with the system and terminates activated security products. Removing the kernel driver requires booting into Safe Mode or using external recovery tools, as standard Windows utilities cannot eliminate software operating at that level.
Winsage
September 9, 2026
Recent investigations have identified the BlueMoon exploit kit, used by espionage-driven threat activity clusters, particularly linked to APT31, a China-aligned state-sponsored group, since August 28, 2026. BlueMoon exploits three vulnerabilities: CVE-2026-85046 (a type confusion vulnerability in Google Chrome's V8 engine), an unassigned V8 sandbox escape, and CVE-2026-85880 (a heap-based buffer overflow in Windows ALPC). Google and Microsoft have released patches for these vulnerabilities, which were exploited as "patch-gap" zero-days. The attack vectors typically begin with phishing emails that lead victims to malicious URLs, triggering the vulnerabilities for code execution and privilege escalation. Variants of BlueMoon have been detected, featuring modifications for specific campaigns. Notable attack chains include: - APT31 targeting NGOs and mining firms in the U.S. with a malicious browser add-on called GemStone. - UNK_LateNight targeting U.S. aerospace companies, deploying BlueMoon alongside the ShadowPad backdoor. - UNK_DoubleCheck targeting a Vietnamese manufacturer, using DLL sideloading to execute a Rust binary. - UNK_QuietRacket targeting government and financial organizations in Indonesia and Singapore, modifying BlueMoon to execute a .NET assembly. CISA added the Chrome flaw to its Known Exploited Vulnerabilities catalog on September 4, 2026, requiring federal agencies to apply patches by September 18, 2026. Indicators of compromise include specific process trees, files, folders, scheduled tasks, mutexes, and registry keys. Proofpoint has released detection rules to help organizations identify and mitigate these threats.
Tech Optimizer
September 5, 2026
The cyber threat group Silver Fox is distributing the ValleyRAT backdoor disguised as a legitimate signed Chinese adware application, specifically bundled with the QN Wallpaper tool. This malware allows attackers to gain comprehensive control over infected machines, enabling them to collect sensitive information, capture screenshots, and deploy additional malicious modules. The attack utilizes DLL sideloading, where a modified version of QN Wallpaper loads a malicious DLL from the same directory, circumventing signature-based security measures. The installer disables Windows Defender, adds itself to autorun entries, and uses the "runas" command to elevate privileges if the user lacks administrator rights. ValleyRAT also marks its process as critical, potentially causing a blue screen of death if terminated. Kaspersky has identified Silver Fox as the likely perpetrator of this campaign, known for similar techniques.
Winsage
September 4, 2026
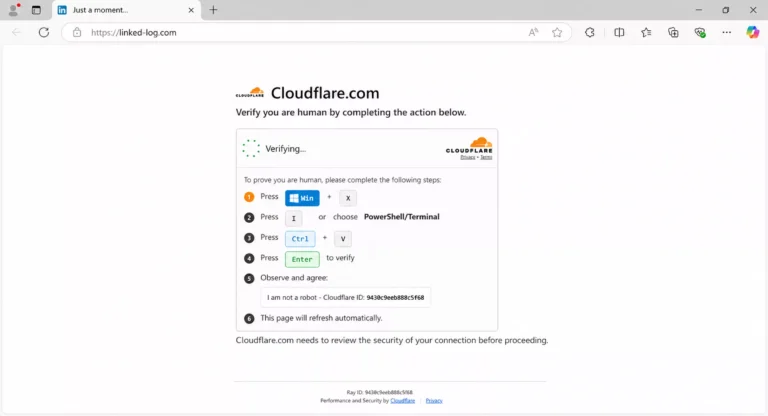
Microsoft has identified a new malware campaign called TerminalFix that uses fake CAPTCHA prompts to trick Windows users into executing malicious commands. This campaign is a variation of ClickFix attacks and employs deceptive pages that impersonate reputable services like Cloudflare. Instead of traditional CAPTCHA challenges, users are instructed to open PowerShell or Command Prompt and paste in commands, allowing attackers to execute complex scripts more easily. TerminalFix initiates a multi-stage intrusion, granting attackers persistent proxy access to the infected machine, which can lead to further exploitation of the company's network. The campaign relies on social engineering tactics, requiring user compliance with counterfeit verification instructions. Microsoft has released mitigation guidance, recommending restrictions on PowerShell access, monitoring for DLL sideloading, blocking outdated Flash plugins, and enabling cloud-delivered protection in Microsoft Defender Antivirus. The campaign poses significant risks to enterprise networks, but individual users should also be cautious about executing commands requested by websites.
Winsage
September 2, 2026
An active malware campaign is using counterfeit software-download websites to distribute malicious installers, primarily targeting users seeking popular software. This campaign has significantly affected China-based operations of multinational corporations and Chinese-speaking users. The malware, once executed, can establish persistence, undermine security measures, and communicate with attacker-controlled infrastructure. Victims span various sectors, including healthcare, manufacturing, gaming, technology, logistics, government, and education. Microsoft associates this campaign with a Chinese threat cluster called Silver Fox, known for using spoofed vendor download pages to spread Gh0st RAT and ValleyRAT. The malicious websites are hosted on .com.cn and .hl.cn domains, featuring Chinese-language content. The downloaded files are dynamically generated, and upon execution, they deploy a wrapper installer that initiates the malware payload. The malware achieves persistence through scheduled tasks and interferes with Windows Update services. The campaign establishes command-and-control communication over non-standard ports, with two identified domains linked to the activity. Microsoft Defender has detected the threat and initiated containment procedures. Kaspersky reported a related malicious installer exploiting a legitimate adware application to execute a backdoor, which captures keystrokes and clipboard contents. ValleyRAT, a sophisticated implant, can collect system information, reboot the computer, capture screenshots, and transmit logs. The attackers are motivated by cyber espionage and financial gain, targeting organizations globally. A subgroup within GoldenEyeDog, known as CuboidalCanine, has also been linked to the use of ValleyRAT, particularly in the gambling industry. In June 2026, Chinese authorities addressed cybercrime cases involving a new variant of the Silver Fox trojan.
Winsage
September 1, 2026
Microsoft Threat Intelligence has identified a new variant of the ClickFix malware campaign called "TerminalFix." This variant uses deceptive CAPTCHAs that mimic trusted services like Cloudflare and directs users to PowerShell or a command prompt, allowing for the execution of complex scripts. TerminalFix aims to orchestrate a multi-stage attack that provides attackers with persistent, network-level proxy access through the compromised host, potentially leading to significant data theft and malware propagation within unsecured enterprise networks. Recommendations for defense against TerminalFix include restricting access to PowerShell and Windows Run dialogs, monitoring for DLL sideloading indicators, blocking Flash plugins, and enabling cloud-delivered protection in Microsoft Defender Antivirus. The attacks primarily target enterprise environments rather than individual consumers.
Tech Optimizer
August 31, 2026
Silver Fox is linked to the distribution of a backdoor malware called ValleyRAT, disguised as the legitimate QN Wallpaper adware application. Once installed, ValleyRAT provides complete control over the compromised machine. The malware uses DLL sideloading to operate under the guise of a legitimate process, bypassing security measures. It disables Windows Defender and adds itself to autorun entries, and can mark its process as critical, causing system crashes if terminated. Kaspersky has identified specific indicators of compromise (IoCs) including hashes, command-and-control servers, and associated domains. In 2026, Kaspersky recorded over 100,000 detections of ValleyRAT affecting more than 1,500 unique users, mainly in China and India.
Winsage
August 14, 2026
CoolClient is a sophisticated backdoor family linked to the HoneyMyte APT group, actively used in cyber-espionage campaigns targeting organizations in Asia and Russia since its initial disclosure in 2022. It has capabilities such as keylogging, clipboard theft, credential harvesting, and system reconnaissance. Investigations in 2023 revealed enhancements, including clipboard theft and HTTP traffic interception. By late 2025 and into 2026, a variant was noted that could deploy a signed kernel-mode driver as a Windows service, improving its stealth and operational capabilities. In a recent campaign targeting Myanmar, the HoneyMyte group used PlugX to deploy CoolClient components. They configured Microsoft Defender to exclude a fake Windows Defender installation directory and a renamed executable, defender.exe, to avoid detection. Persistence was achieved through a scheduled task that executed defender.exe with SYSTEM privileges at startup, which sideloaded the malicious libngs.dll to initiate the CoolClient execution chain. The latest CoolClient variant has a multi-stage execution chain, including: - defender.exe / Sang.exe: Exploited legitimate application for DLL sideloading. - libsrapc.dll: Benign dependency for the Sangfor application. - libngs.dll: First-stage loader that decrypts and loads the next stage. - loadcert.ini: Second-stage DLL implementing core functionalities. - cert.ini: Final-stage implant for command and control communication. - time.ini: Configuration file for CoolClient. The execution begins with the legitimate Sangfor application loading libngs.dll, which uses obfuscation to conceal its operations. The second stage, loadcert.ini, is injected into synchost.exe and performs tasks including persistence and process injection. The kernel-mode driver deployment routine involves decrypting time.ini, verifying privileges, and creating a service to execute the driver, enhancing stealth. The deployed kernel-mode driver, msagent.sys, is digitally signed and helps hide processes, files, and registry objects, making detection more difficult. The latest variant continues to target organizations consistent with previous HoneyMyte activities, with confirmed victims in Myanmar, Mongolia, Pakistan, and Russia, including government entities. The deployment of CoolClient as a secondary backdoor after a PlugX infection indicates a strategic approach to maintain access to compromised systems. The malware is confirmed as a new variant of CoolClient associated with the HoneyMyte threat group, with the kernel-mode driver marking a significant advancement in its capabilities.
Tech Optimizer
July 10, 2026
Cybercriminals are exploiting the VLC media player to install ValleyRAT, a remote access trojan, by embedding malware in a seemingly harmless file linked in phishing emails. The attack starts with an email that prompts the victim to download a ZIP archive containing a fake VLC executable and a malicious DLL named libvlc.dll. This method uses DLL sideloading to execute the malware under the guise of a legitimate application. Once executed, the malware establishes persistence by creating a registry entry and connects to a remote server to retrieve the final payload. ValleyRAT employs evasion tactics to avoid detection, including assessing system characteristics before executing harmful actions and using a fileless approach to deliver the payload directly into memory. Researchers have identified indicators of compromise, including specific SHA1 hashes and URLs associated with the malicious campaign.
Search