DNS

AppWizard
September 10, 2026
The Tor Project has launched Tor VPN Beta for Android, allowing mobile applications to route traffic through the Tor network, expanding beyond web browsing. This development was driven by user demand for privacy tools to bypass internet censorship, particularly in restrictive regions. The concept originated in 2021, and after initial testing and user feedback, the beta was announced on September 9. Tor VPN creates a separate Tor circuit for each application, enhancing privacy by complicating activity correlation across apps. Users can select which applications use Tor, and the interface has been improved for easier management. The beta version 1.4.0 includes support for WebTunnel bridges to disguise Tor connections as standard encrypted traffic. Usability testing revealed issues with exit-node selection, leading to a design change that requires users to connect to Tor before choosing an exit. Tor VPN is built on the Arti implementation of the Tor protocol and the Onionmasq networking layer, ensuring stability and component sharing. The software supports reproducible builds and is available via F-Droid and APK downloads. A security review in June 2025 found no major flaws but identified some issues being addressed. Tor VPN is currently in beta and focuses on enhancing circumvention capabilities and usability rather than competing with commercial VPNs on speed. Users in censored areas are advised to configure bridges for access.
Tech Optimizer
September 10, 2026
Apple provides built-in security features for macOS, including XProtect, Gatekeeper, and automatic malware removal, which contribute to the safety of Macs. However, these protections do not effectively address threats like infostealers, phishing, and adware. For enhanced security, third-party antivirus solutions are recommended. Bitdefender is noted for its strong detection rates and minimal system impact, making it suitable for most users. Intego specializes in Mac-specific threats and is ideal for users focused solely on Apple products. ESET and Trend Micro are recommended for businesses needing centralized management. F-Secure is recognized for its privacy-focused approach, while Norton offers a comprehensive suite of security features. AVG provides free real-time protection suitable for low-risk personal use, but may not be adequate for business needs. CleanMyMac is a maintenance tool rather than a traditional antivirus, focusing on system cleanup and optimization. Users should avoid running multiple real-time scanners simultaneously and ensure they purchase appropriate licenses for business use. It's important to evaluate the necessity of additional features and consider long-term pricing when selecting antivirus software.
Tech Optimizer
September 10, 2026
Bitdefender is recognized for its strong detection capabilities, mid-range pricing, and minimal system impact. Malwarebytes offers a free scanner for cleaning infected Macs, while Intego specializes in macOS with features tailored for Apple users. Norton provides a comprehensive security package with VPN, backup, and identity monitoring features. Gen Digital owns Norton, Avast, AVG, and Avira, indicating that these brands share threat intelligence and engineering resources. The 2026 Mac Antivirus Scorecard ranks Bitdefender highest with a score of 8.8, followed by Intego (8.2), Malwarebytes (8.3), ESET (8.3), and Norton (7.4). Pricing structures often include discounted first-year rates that can double upon renewal. Free options include Avast and Avira with real-time protection, while Malwarebytes offers a free on-demand scanner. Multi-device licensing can provide better value, and business Macs should use business licenses for essential features. macOS has built-in protections like XProtect and Gatekeeper, but third-party antivirus solutions can enhance security against newer threats.
Winsage
September 9, 2026
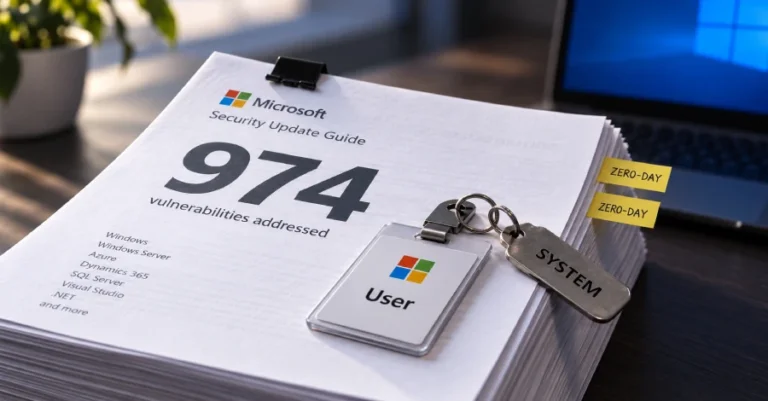
Microsoft addressed 974 vulnerabilities in its software suite during its recent Patch Tuesday, marking a record high. The breakdown includes 723 flaws in Windows, 111 in Office, 62 in SQL, and 22 in Developer Tools, with over 110 rated as critical. Two actively exploited vulnerabilities are CVE-2026-85880 and CVE-2026-81963, both allowing local privilege elevation. Other notable vulnerabilities include CVE-2026-55007 (8.1), CVE-2026-80097 (8.6), CVE-2026-69465 (8.8), and several with CVSS scores of 9.6 and above. Microsoft has patched a total of 2,760 security flaws this year, reflecting a trend of increasing vulnerability discoveries. Despite the extensive patching, no significant spike in active exploits has been observed.
Winsage
September 9, 2026
Microsoft's September 2026 security update revealed 973 vulnerabilities, with 113 classified as critical. Two actively exploited vulnerabilities are CVE-2026-81963 (Windows Update Stack, elevation of privilege, CVSS 7.8) and CVE-2026-85880 (Windows ALPC, elevation of privilege, CVSS 7.8). Among the 113 critical vulnerabilities, 82 are remote code execution (RCE) vulnerabilities. Notable vulnerabilities include: - CVE-2026-69676: RCE in Windows Kerberos, CVSS 8.8, authentication bypass. - CVE-2026-69852: RCE in Windows RRAS, CVSS 7.5, heap-based buffer overflow. - CVE-2026-72957: RCE in Windows Deployment Services, CVSS 7.8. - CVE-2026-69854: Elevation of privilege in Spring Cloud Azure, CVSS 9.0, improper authentication. - CVE-2026-83501: Information disclosure in Windows VBS, CVSS 5.5. - CVE-2026-69730: RCE in Windows DNS Server, CVSS 9.8. Less likely to be exploited vulnerabilities include: - CVE-2026-69845: RCE in Windows DHCP Server, CVSS 9.8, heap-based buffer overflow. - CVE-2026-65772: Vulnerability in Microsoft Dynamics 365 On-Premises, CVSS 8.8, deserialization of untrusted data. - CVE-2026-66302: RCE in Skype for Business, CVSS 9.8. Additional critical vulnerabilities include: - CVE-2026-62916: Elevation of privilege in Microsoft Entra ID, CVSS 9.1. - CVE-2026-83941: Elevation of privilege in Entra ID, CVSS 9.9. - CVE-2026-80098: Vulnerability in Copilot Studio, CVSS 9.3, improper verification of cryptographic signatures. Talos is releasing a new Snort ruleset to detect attempts to exploit these vulnerabilities, with specific SIDs for Snort 2 and Snort 3 rule coverage.
AppWizard
August 29, 2026
Google has introduced several network security enhancements in Android 17 to improve user privacy. One key feature is Encrypted Client Hello (ECH), which encrypts domain names to prevent external observers from monitoring user activities. ECH is integrated with private DNS and is enabled by default for apps using compatible networking libraries. Google claims to be the first major mobile operating system to implement widespread ECH support. Testing conducted by Jigsaw showed stable connection success rates and minimal interference across various networks. Additional security features in Android 17 include: - Local Network Protection, requiring apps to request permission before accessing devices on a user's home network. - Certificate Transparency, mandating public logging of certificates to detect forged ones. - A 2G Network Shutdown option for mobile operators to disable 2G services, reducing exposure to phishing messages.
Search