- Wild Tokyo, Rolling Slots, Mino Casino, and Boho Casino are the best mobile casinos in Australia based on mobile performance, gameplay experience, payment efficiency, and overall usability.
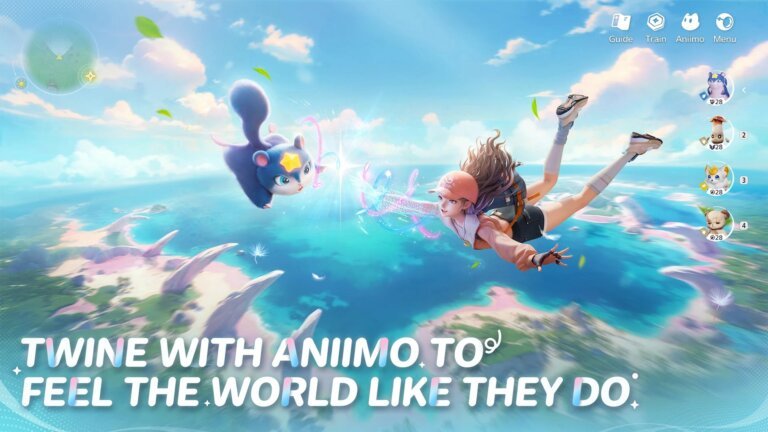
Aniimo is a game that allows players to explore the open world of Idilia, tame unique creatures, and transform into Aniimo using the Twine mechanic. The game features cross-progression support and has specific hardware requirements for Android and iOS devices.
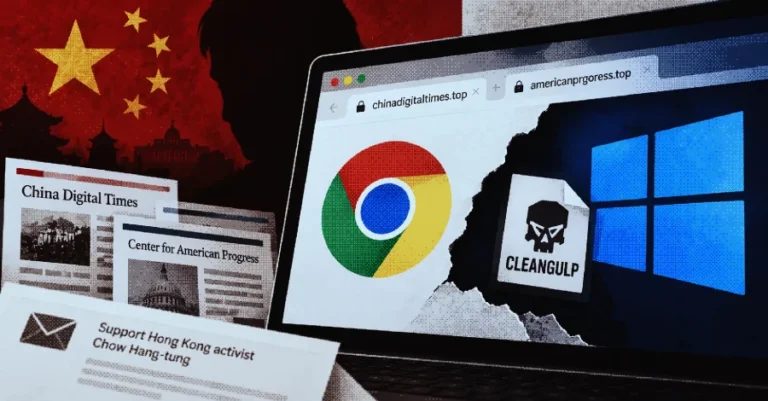
A Chinese threat actor, codenamed UTA0565, has exploited newly disclosed vulnerabilities in Google Chrome (CVE-2026-85046, CVE-2026-87491) and Windows (CVE-2026-85880) through deceptive websites, achieving remote code execution. The attacks were detected on September 3 and 4, 2026, and involved impersonating organizations to mislead victims, particularly targeting Asian government entities with phishing emails related to Hong Kong activist Chow Hang-tung. The phishing messages directed users to fraudulent sites that loaded an HTML element using the BlueMoon exploit kit, which delivered a payload named "chrome_cleanup.exe," associated with the CLEANGULP malware family. This malware allows for command execution, process listing, file uploads and downloads, and uses a hard-coded domain for command-and-control communications. The exploit's widespread use suggests a coordinated effort within the Chinese cyber espionage community, with indications that multiple groups are sharing and weaponizing the exploit.
A customer brought in a functional Dell laptop running Windows 10, which lost mainstream support from Microsoft in October 2025. Although the laptop still operates, Microsoft has stopped patching security vulnerabilities unless users take specific actions. Users have three options: upgrade to Windows 11 if their PC meets requirements, purchase a new or refurbished PC, or enroll in extended security updates available until October 2027. There is also a warning about potential scams related to Windows 10's support status. Users can check their PC's eligibility for Windows 11 using the "PC Health Check" app from Microsoft.
The Android development community has historically addressed memory optimization reactively, but new performance requirements from Google Play, effective February 2027, emphasize proactive memory management. These requirements include metrics for dynamic memory usage, bitmap memory, and DEX code optimization, with apps needing at least 25% optimization coverage. Memory usage can now hinder releases even without local crash replication, necessitating its integration into the pre-production process alongside other performance metrics.
Dynamic memory usage is defined as anonymous RSS plus swap, excluding file-backed data. Google Play will evaluate this across different application states and device performance categories. Bitmap memory is scrutinized for the retention of invisible bitmaps, and DEX optimization aims to reduce memory footprint and improve performance.
Investigating memory growth involves using Android Studio’s Memory Profiler to monitor memory changes during specific user flows and conducting heap dumps to identify retained objects. Issues often arise from retained state, where components hold onto callbacks that reference image data, necessitating a focus on lifecycle management rather than merely cache size.
Bitmap memory should be carefully managed, as the decoded size can significantly exceed the compressed file size. Downsampling images to match UI dimensions is crucial. Memory checks should occur before production, with a focus on establishing a memory budget based on actual measurements and defining representative memory scenarios for testing.
A pre-release memory checklist includes running user flows repeatedly, testing on various devices, inspecting heap dumps, examining image configurations, and reviewing optimization metrics. Monitoring Android vitals and Play Console warnings is essential to detect potential issues before they lead to user-reported crashes.
LastPass has identified a sophisticated scheme targeting users of its Authenticator app, involving SEO poisoning and deceptive GitHub pages that distribute malicious ZIP files disguised as legitimate software. Users searching for "LastPass Authenticator download" may encounter these counterfeit pages, which redirect them to a malicious server delivering a ZIP file containing vsdbg.exe and vsdbg.dll. The executable is a legitimate Microsoft debugging tool exploited to execute the malicious DLL through DLL sideloading, allowing the malware to run undetected.
Named Rapuncel by security researchers from Delphos, this malware is undetectable by antivirus engines and targets a hardcoded list of 145 antivirus and endpoint security products, disabling them upon detection. Rapuncel harvests sensitive information, including saved passwords from over 25 web browsers, cryptocurrency wallet files from more than 30 applications, and session tokens from platforms like Discord and Steam. It also captures screenshots and compiles a profile of the infected system, uploading the stolen data to an attacker-controlled server. The malware includes a kernel driver that intercepts web traffic, allowing for advertisement injection and search result manipulation.
This campaign has been active for several months, with LastPass vaults remaining unaffected. Users are advised to download applications only from trusted sources. Rapuncel establishes persistence on infected machines by installing itself as a Windows service that starts with the system and terminates activated security products. Removing the kernel driver requires booting into Safe Mode or using external recovery tools, as standard Windows utilities cannot eliminate software operating at that level.
- Game Developer Releases WWII-Themed Match-3 Combat Game
- Loyal Mussy has launched Milk Run: Tiles Over Europe, a WWII-themed match-3 combat game for Android
- Players control a B-17 bomber on missions over wartime Europe, blending puzzle-solving and aerial warfare
- Features a 25-mission campaign with various enemy aircraft types, anti-aircraft flak corridors, and historically accurate bombing targets
- Players can upgrade their bomber, recruit crew members, and customize nose art and aircraft renaming
- Immersive experience with visible battle damage, detailed sound design, and no ads or in-app purchases
- Available for download on Android devices via Google Play
Valve has released the Lepton project on GitLab, which aims to bring Android games to Linux devices, with a focus on VR Android games for the Steam Frame.
Microsoft Office Professional Plus 2019 is available for .97, down from its regular price of 9. This offer is valid until September 27 and provides a lifetime license for one Windows PC, with no recurring fees. The suite includes applications such as Word, Excel, PowerPoint, Outlook, OneNote, Publisher, and Access, and features enhanced inking capabilities, new analytical tools in Excel, upgraded PowerPoint features, and improved Outlook functionalities. Users receive an immediate email with the download link and license key, which must be redeemed within seven days. The offer supports all languages and includes updates for the 2019 version.
On September 17, researchers from LastPass and Delphos Labs discovered a counterfeit LastPass Authenticator installer on GitHub that installs a malicious Windows kernel driver designed to disable antivirus and steal passwords. The driver, named Alinubx.sys, was signed through Microsoft's hardware compatibility program and initially scored zero detections on VirusTotal. The fake installer is hosted on a fraudulent GitHub page that mimics a legitimate LastPass product page. When executed, the installer uses DLL side-loading to gain SYSTEM-level access and terminates security processes, allowing it to harvest saved passwords from various browsers and applications. The driver is a renamed variant of a known malicious driver, evading detection due to its new file hash. Delphos reported the driver to Microsoft, but it was not considered a security vulnerability. Users who executed the fake installer should treat their passwords and sensitive data as compromised and change them from a secure device. The malicious server has been linked to impersonation pages for multiple brands, and the loader was likely created using a specific crypter tool.