- Wild Tokyo, Rolling Slots, Mino Casino, and Boho Casino are the best mobile casinos in Australia based on mobile performance, gameplay experience, payment efficiency, and overall usability.
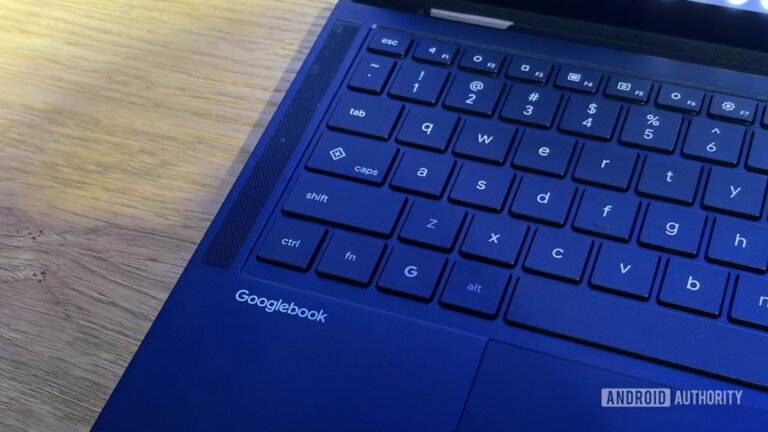
Dieter Bohn showcased the features of Googlebook OS in a video, emphasizing its app windowing and gesture controls similar to macOS. Users can navigate with gestures like a three-finger upward flick to view active applications and can also use a square-shaped key for multitasking. Googlebook OS supports Android-optimized applications and web interfaces, allowing users to drag windows for split-screen or full-screen views. It features multiple desktops with a unified taskbar across all, enhancing the user experience. All models, except the Acer 360º convertible, have haptic feedback trackpads.
Global mobile gaming revenue reached .6 billion in 2024, with projections indicating it will surpass 0 billion by the close of 2026. By 2026, the average flagship Android device will have 12GB of RAM, enhancing slot loading times and live dealer streaming. A 120Hz refresh rate can reduce perceived input lag by approximately 40% compared to 60Hz panels. As of early 2026, mobile users constitute 61% of all online gambling traffic globally. High-end devices like Samsung’s Galaxy S26 Ultra and Google’s Pixel 10 Pro feature vapor chamber cooling for sustained gaming performance. The global luxury goods market reached .5 trillion in 2024, with 9% of that total spent on digital entertainment. Flagship devices with Snapdragon 8 Gen 4 chipsets deliver live dealer feeds in 1080p and provide OLED screens for enhanced visual quality. A 5,000mAh battery supports three-hour gaming sessions and can recharge to 60% in about 20 minutes. Understanding wagering requirements and game weighting is crucial for maximizing bonuses. Progressive web apps ensure reliable performance on unstable connections, while flagship devices offer hardware-level encryption and biometric authentication for security.
A newly identified strain of Android malware, RatHat, utilizes generative AI to manipulate infected devices in real time. It is linked to threat actors believed to be operating out of China. RatHat serializes the device’s live Accessibility tree into XML format and communicates with a generative AI assistant to return screen coordinates, identify text, and issue navigation commands. The malware employs WebView-based HTML overlays to capture login credentials from banking and cryptocurrency applications and can infiltrate payment apps like WeChat and Alipay to extract PINs. It also features an SMS receiver and notification listener to intercept OTPs and 2FA codes.
RatHat is disseminated through smishing, malvertising campaigns, and misleading third-party forums. It employs anti-analysis techniques such as container tampering, manifest bombing, DEX bytecode poisoning, string encryption, and anti-debugging. Once installed, it gains Accessibility access, activates Developer Options, and enables Wireless Debugging, allowing it to connect to the device's local ADB service and launch control agents with shell-level privileges.
The malware captures raw touch coordinates to reconstruct PINs and unlock patterns, bypassing screenshot protections. It also includes persistence mechanisms that prevent uninstallation by presenting a fake Google Play failure overlay and automatically reinstalling itself if removed.
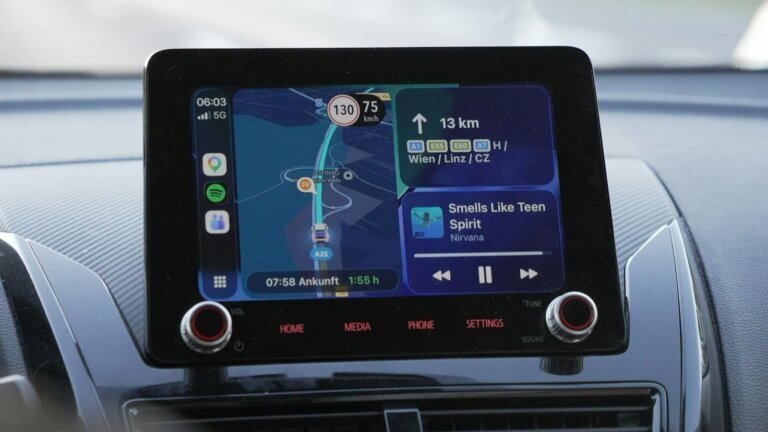
In Android Auto version 17.8.163744 and Google Maps 26.38.0, a new feature called Driving Avatar allows users to customize the vehicle icon displayed on the screen. This feature was introduced in February 2025 and became available in Android Auto by May 2026. Users can access the Google Maps app directly through Android Auto to customize their avatar, which can be done by tapping the settings icon and selecting Driving Avatar. Customization options include various vehicle types and colors, such as a blue arrow, sedan, truck, SUV, sports car, small EV, and legacy icons like a red car, green pickup, and yellow station wagon. Additionally, Google Maps offers practical features like downloading offline maps, sharing trip progress, enabling media playback controls, and tailoring route suggestions.
Cybersecurity researchers at Zimperium have identified a new strain of malware called RatHat, targeting Android devices and linked to threat actors from China. RatHat uses generative AI to maintain persistence and control over infected devices. The malware is typically spread through social engineering, tricking users into downloading counterfeit applications that appear legitimate. Once installed, RatHat requests accessibility permissions, activates Wireless Debugging, and can capture text messages, create overlays, and steal passwords and multi-factor authentication codes. Its AI capabilities allow it to navigate the device interface in real-time, making detection by security software more difficult. To protect against RatHat, users should avoid downloading apps from untrustworthy sources, and removal requires a factory reset of the device.
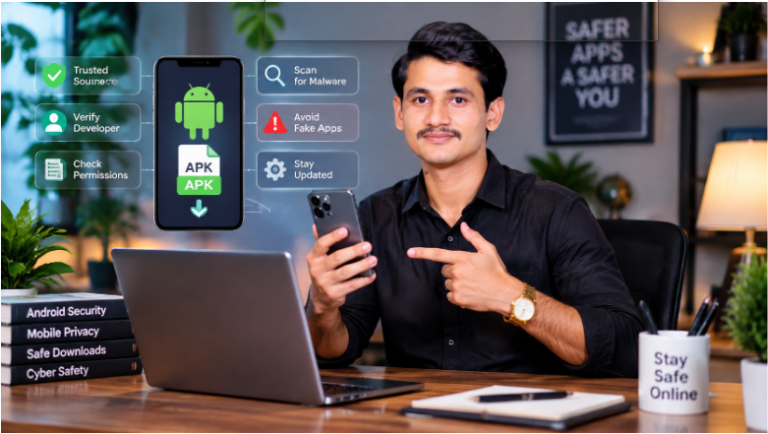
Downloading an APK file allows Android users to access various applications, including those not available in official app stores. Users should consider the source, developer credibility, and requested permissions before installation. APK files are the format used by Android for app installation, and users may download them for reasons such as regional restrictions, needing older versions, or testing beta releases. APK files are not inherently unsafe; the risks arise from unknown sources, which may contain malware, tracking software, or other harmful elements.
To ensure safety, users should verify the origin of the file, the developer's identity, and the permissions requested by the app. They should also scan APK files with security tools and be cautious of warning signs like unrealistic promises or missing developer information. A checklist before installation includes researching the app name, confirming the developer, reviewing permissions, checking security information, and monitoring the app after installation. Safe practices involve downloading from official sources, avoiding unknown websites, and keeping Android security updates current. Trusted information sources can help users make better decisions regarding APK files.
Windows operating systems include built-in tools for maintaining PCs, allowing users to monitor system health, repair corrupted files, and recover from boot failures with minimal intervention.
Task Scheduler automates maintenance tasks by triggering them based on schedules or events, accessible via the Start menu or taskschd.msc. It can activate tasks at fixed intervals, on startup, during idle periods, or in response to Event Viewer entries. Tasks should run with the highest privileges and can be configured to execute regardless of user sign-in status. The Settings tab allows missed tasks to run as soon as possible.
DISM (Deployment Image Servicing and Management) is a command-line utility that repairs the component store, essential for installing updates and restoring system files. It offers three inspection levels: CheckHealth, ScanHealth, and RestoreHealth, with the latter requiring an internet connection for downloading replacement files. DISM logs operations in C:WindowsLogsDISMdism.log.
SFC (System File Checker) verifies and repairs core operating system files using Windows Resource Protection. The command sfc /scannow checks all protected files, while /verifyonly provides a report without changes. SFC's effectiveness depends on the integrity of the component store, making it essential to run DISM first. Results are logged in C:WindowsLogsCBSCBS.log.
Quick Machine Recovery (QMR), introduced in Windows 11, addresses boot failures by connecting to the internet to find solutions when repeated boot failures are detected. QMR is enabled by default on unmanaged devices and can continuously check for fixes. It is designed to respond to widespread issues rather than unique problems and may not work effectively on older hardware or without a network connection.
Together, these tools provide a comprehensive approach to system maintenance in Windows 11, ensuring the operating system remains healthy and efficient without additional software.
Avast Free Antivirus is recognized as the best free antivirus solution for Windows in 2026, achieving a perfect score from AV-TEST. It operates on the same engine as paid versions, providing comprehensive protection. Other notable free antivirus options include Bitdefender Antivirus Free, which is efficient for older systems; Microsoft Defender, a built-in option with solid protection; AVG AntiVirus Free, suited for older hardware; Avira Free Security, which includes additional tools; and Malwarebytes Free, best for cleaning infections. Each product generates revenue through upselling or data collection. Avast scored 99.78% in detection tests, while Bitdefender achieved 97.6%, and Microsoft Defender reached 99.93%. AVG matched Avast with a 99.97% protection rate, and Avira recorded 99.96%. Malwarebytes had a detection rate of 99.57%. Kaspersky is noted as a product to avoid due to misleading trial offers.
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox.
The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception.
Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client.
The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.