emails

Winsage
September 18, 2026
The initial storage cost of the search index on a fresh installation of Windows 11 is minimal, only a few megabytes. When a sizable work folder is added, the index expands, but it does not revert to its original size after the folder is removed. The search index is stored in Windows.db for Windows 11 and Windows.edb for Windows 10. Windows 11 has two indexing modes: Classic (default) and Enhanced, with Classic indexing Documents, Pictures, Music folders, and the Desktop, while Enhanced scans the entire PC. The index includes file names and content, allowing keyword searches. Users can measure their index items through Settings without special permissions, while file size requires administrative access via PowerShell. An index under 30,000 items is acceptable for average users, while performance issues may arise beyond 400,000 items, with a technical ceiling of one million items. In an experiment, the index grew from 462 items and 6.71 MB to 3,466 items and 18.66 MB after adding 3,000 text files, but remained at 16.81 MB after deleting those files. To reclaim disk space, users can exclude specific folders from indexing and rebuild the index, which can significantly reduce its size while retaining the same number of items.
Winsage
September 15, 2026
Iranian state cyber actors are targeting individuals through popular messaging applications, using surveillance and data-stealing malware known as "Chosen Brick," which has been in use since at least 2025. This malware is designed for Windows systems and enables the theft of personal data, allowing Iranian spies to monitor perceived threats such as dissidents, activists, and journalists. The attacks typically begin with messages sent via WhatsApp or Telegram, impersonating trusted contacts. Attackers conduct extensive research on their targets to craft convincing messages that encourage victims to download malicious files disguised as legitimate applications. Once executed, Chosen Brick operates stealthily, evading detection and establishing a connection for command-and-control communications. It can enumerate processes, capture screen and audio content, extract sensitive information, and even wipe infected systems. Organizations suspecting compromise are advised to engage IT providers for investigations and to inform staff about potential risks. Recent alerts follow cyberattacks on water and energy sectors linked to Iran, with ongoing concerns about the implications for cybersecurity amid escalating military tensions. Additionally, five US agencies have reported that attackers are using AI-generated scripts to exploit vulnerabilities in critical infrastructure systems.
Tech Optimizer
September 15, 2026
In 2026, McAfee introduced its AI-powered Scam Detector as part of the McAfee+ suite, which includes antivirus protection, identity monitoring, privacy tools, VPN services, and financial safeguards. The McAfee+ Advanced tier is available for .99 for the first year, reduced from 9.99, and a family plan for up to six members is priced at 9.99, down from 9.99. Each plan includes a 30-day money-back guarantee. Research shows Americans receive an average of 14 scam messages daily, with one in three falling victim to online scams, losing an average of ,160. The Scam Detector identifies threats such as suspicious texts, emails, deepfake videos, and risky websites, and includes a QR code safety check. It is included in all McAfee core plans at no additional cost.
Winsage
September 15, 2026
A spear-phishing campaign linked to the Chinese threat actor UTA0560 targeted various NGOs on September 1, 2026, exploiting recently patched vulnerabilities in Google Chrome and Microsoft Windows. The campaign utilized a malicious JavaScript backdoor called GRIMWEDGE, which was deployed through a multi-stage exploit chain that involved three vulnerabilities: CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880. The attack began with spear-phishing emails that led recipients to a vulnerable U.S.-based university website, allowing attackers to redirect users to their infrastructure. The exploit chain enabled arbitrary code execution and facilitated the deployment of GRIMWEDGE, which is capable of host reconnaissance, file and process management, command execution, and payload delivery. The initial payload was an executable named "msgbox.exe," which extracted a legitimate Windows binary and a malicious DLL called "wsc.dll." This DLL initiated a sideloading chain and contacted a command-and-control server for further instructions. GRIMWEDGE allows for several commands, including system reconnaissance, directory listing, file deletion, and command execution in a hidden window. It lacks built-in persistence or lateral movement mechanisms but provides a foothold for further exploitation. Concurrently, another Chinese threat actor, JungleBamboo (APT31), used the same exploit chain to deploy a loader named SUPERSTOMP, which installs a credential-stealing Chrome extension called LONGTALE. The simultaneous use of the exploit chain by multiple actors suggests potential sharing or sale of the exploit, raising concerns about patch-gap vulnerabilities that pose risks for exploitation campaigns.
AppWizard
September 14, 2026
The “Continue Activity” feature will officially debut around mid-September 2026 within the “Cross-Device Services” settings on Android. It includes the “Task Handoff” feature, allowing users to transition tasks between devices. Users can also toggle access to apps, media, and notifications across Android devices, Chromebooks, or Googlebooks. The rollout is currently focused on the “Pixel 11” series, including the “Pixel 11 Pro XL” and “Pixel 11 Pro Fold,” with plans to expand to other devices running “Android 17.”
Winsage
September 9, 2026
Recent investigations have identified the BlueMoon exploit kit, used by espionage-driven threat activity clusters, particularly linked to APT31, a China-aligned state-sponsored group, since August 28, 2026. BlueMoon exploits three vulnerabilities: CVE-2026-85046 (a type confusion vulnerability in Google Chrome's V8 engine), an unassigned V8 sandbox escape, and CVE-2026-85880 (a heap-based buffer overflow in Windows ALPC). Google and Microsoft have released patches for these vulnerabilities, which were exploited as "patch-gap" zero-days. The attack vectors typically begin with phishing emails that lead victims to malicious URLs, triggering the vulnerabilities for code execution and privilege escalation. Variants of BlueMoon have been detected, featuring modifications for specific campaigns. Notable attack chains include: - APT31 targeting NGOs and mining firms in the U.S. with a malicious browser add-on called GemStone. - UNK_LateNight targeting U.S. aerospace companies, deploying BlueMoon alongside the ShadowPad backdoor. - UNK_DoubleCheck targeting a Vietnamese manufacturer, using DLL sideloading to execute a Rust binary. - UNK_QuietRacket targeting government and financial organizations in Indonesia and Singapore, modifying BlueMoon to execute a .NET assembly. CISA added the Chrome flaw to its Known Exploited Vulnerabilities catalog on September 4, 2026, requiring federal agencies to apply patches by September 18, 2026. Indicators of compromise include specific process trees, files, folders, scheduled tasks, mutexes, and registry keys. Proofpoint has released detection rules to help organizations identify and mitigate these threats.
AppWizard
September 9, 2026
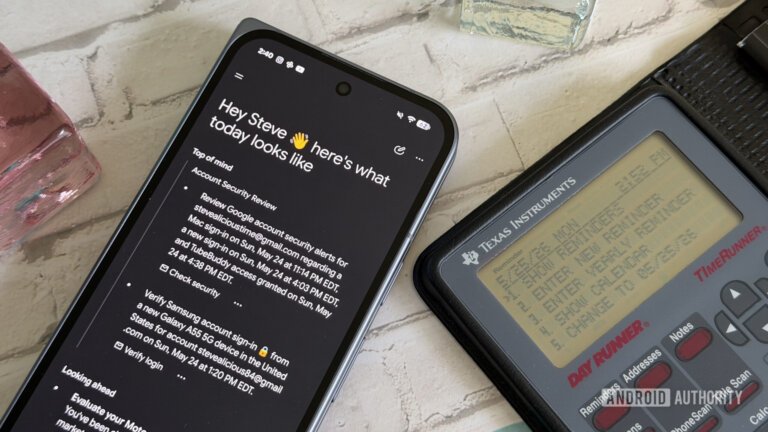
Google has extended access to its Gemini Daily Brief feature to users in the United States without requiring a paid Google AI subscription. This change allows users without Plus, Pro, or Ultra tiers to receive daily briefings summarizing essential tasks and emails. The announcement confirmed the removal of subscription prerequisites, aiming for a more inclusive user experience. The feature delivers concise information once a day and is accessible through Gemini mobile applications and the web platform, provided users link their Workspace apps and enable memory features. The rollout may be gradual, leading to potential delays for some users.
Search