enrollment

Tech Optimizer
September 14, 2026
The encryption landscape has shifted significantly, with Microsoft’s BitLocker and Apple’s FileVault becoming the primary free and integrated solutions for disk encryption. Organizations are encouraged to focus on comprehensive management capabilities rather than just acquiring encryption technology. Key management, compliance proof for auditors, and consistent policy enforcement across devices are critical. Native encryption solutions do not provide fleet-wide compliance, centralized key escrow, or advanced pre-boot authentication options. Various management models exist for different organizational needs, including options from Microsoft, Sophos, ESET, Trend Micro, Check Point, Trellix, WinMagic, Broadcom (Symantec), Dell, and Kaspersky. It is essential to ensure proper key management and recovery procedures before enforcing encryption to avoid data loss. Organizations should verify claims of compatibility and effectiveness of encryption solutions, especially regarding pre-boot authentication and cryptographic standards. Native encryption solutions are free, but management layers typically incur costs. Open-source solutions like VeraCrypt lack necessary management features, making them impractical for businesses.
Tech Optimizer
September 13, 2026
The landscape of encryption engines has stabilized, with Microsoft BitLocker and Apple FileVault being the primary solutions. As of 2026, the emphasis is on management rather than just acquiring encryption technology. Key management elements include audit proofing, key escrow and recovery, policy enforcement, and pre-boot options. Native encryption solutions lack features such as fleet-wide compliance proof, centralized key escrow, consistent policy enforcement, advanced pre-boot authentication, and removable-media encryption. Various management models are available for different environments, including: 1. Microsoft BitLocker with Intune: Free for Windows Pro/Enterprise, integrates with Entra ID for key management. 2. Sophos: Manages both BitLocker and FileVault from a single console. 3. ESET: Offers lightweight management and removable-media protection. 4. Trend Micro: Integrates encryption with DLP capabilities. 5. Check Point: Provides advanced pre-boot options and policy management. 6. Trellix: Comprehensive enterprise encryption suite with a complex management interface. 7. WinMagic: Focuses on cross-platform encryption and strong pre-boot options. 8. Broadcom (Symantec): Manages native engines within its broader security framework. 9. Dell: OEM-integrated encryption management for Dell hardware. 10. Kaspersky: Provides encryption management but is restricted in the U.S. Key considerations before deploying encryption include ensuring key escrow is in place, conducting recovery tests, and being mindful of removable media and server encryption. Common mistakes include using outdated freeware and not verifying key escrow. Organizations should request auditor reports for compliance verification and confirm claims of compatibility and pre-boot functionality. Native encryption engines are free, while management layers typically charge on a per-endpoint basis.
Tech Optimizer
September 11, 2026
Microsoft BitLocker and Apple FileVault are free, integrated encryption solutions within their respective operating systems. As of 2026, the focus is on investing in management solutions that provide compliance proof, key escrow, recovery options, and policy enforcement across devices. Native encryption solutions lack certain management features, prompting the need for additional management layers from various vendors. Legacy freeware like TrueCrypt is no longer maintained, posing risks for business use, while VeraCrypt is a credible open-source alternative but lacks centralized management. Management options include Microsoft Intune for Windows, Sophos for mixed fleets, and specialized providers like Check Point and WinMagic for advanced needs. Organizations should ensure proper key management before enforcing encryption to avoid data loss and regularly test recovery processes. It is crucial to verify claims regarding compatibility and pre-boot options when selecting encryption solutions. Native engines are free, but management layers typically charge per endpoint annually.
Winsage
August 29, 2026
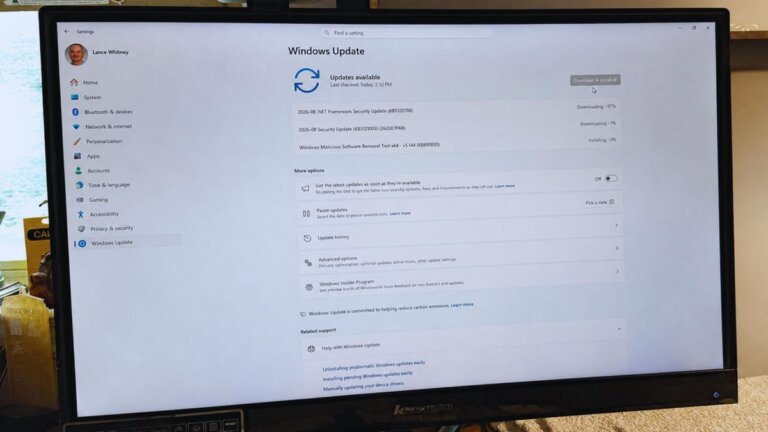
Windows updates are released frequently to enhance performance, improve compatibility, fix bugs, and distribute critical security patches. Microsoft issues security updates every second Tuesday of the month, known as Patch Tuesday, which are cumulative, meaning the latest updates include all previous fixes. The Cybersecurity and Infrastructure Security Agency (CISA) issues warnings about vulnerabilities, and Microsoft maintains a security portal for documentation of these issues. Users on unsupported versions, like Windows 10 without Extended Security Updates (ESU), are at increased risk. In addition to security updates, Windows receives an annual feature update and occasional optional non-security updates that introduce new features and enhancements. An example is the Windows 11 February 2026 preview update, which added new features and improvements.
Winsage
August 27, 2026
Windows 10 Enterprise LTSB 2016 and Windows 10 IoT Enterprise 2016 LTSB will reach their end of support on October 13, 2026, after which they will no longer receive security updates. These operating systems are designed for fixed-function devices like kiosks and point-of-sale terminals, which are often not actively managed, posing risks if the end-of-support date is overlooked. Microsoft offers an Extended Security Updates (ESU) program as a temporary solution, with escalating costs over three years, but it is not intended as a long-term fix. Customers must decide whether to continue paying for ESU, upgrade to newer hardware, or transition away from Windows.
Winsage
August 15, 2026
Windows 11 requires a compatible 64-bit processor with a minimum speed of 1 GHz and at least two cores, 4GB of RAM, and 64GB of available storage. The system must use UEFI firmware with Secure Boot capability, support Trusted Platform Module (TPM) 2.0, and have graphics hardware compatible with DirectX 12 or later with a WDDM 2.0 driver. A high-definition display with a resolution of at least 720p, measuring more than 9 inches diagonally, and supporting 8 bits per color channel is also necessary. Microsoft provides the PC Health Check app to assess compatibility with Windows 11. If a PC cannot upgrade, users can enroll in the Consumer Extended Security Updates (ESU) program for Windows 10 version 22H2, which extends security updates until October 12, 2027, without introducing new features. Enrollment options include syncing settings for free, redeeming 1,000 Microsoft Rewards points, or paying a fee, with a license applicable to up to 10 devices.
Winsage
August 15, 2026
In 2026, Microsoft Windows 11 requires specific hardware criteria for installation, including a 64-bit processor (1 GHz or faster with at least two cores), a minimum of 4GB of RAM, at least 64GB of available storage, UEFI firmware with Secure Boot, TPM version 2.0 support, and graphics hardware that supports DirectX 12 or later with a WDDM 2.0 driver. A high-definition display with a resolution of at least 720p and a diagonal measurement exceeding 9 inches is also necessary. Compatibility can be checked using the PC Health Check app, which may take up to 24 hours to reflect recent hardware upgrades. For Windows 10 users unable to upgrade, the Consumer Extended Security Updates (ESU) program provides security updates until October 12, 2027, without new features. Enrollment options include syncing settings for free, using Microsoft Rewards points, or paying a fee, with each license applicable to up to 10 devices.
Winsage
August 13, 2026
A recent update has been released, addressing security vulnerabilities and improving system functionality. Key improvements include a fix for the Backup feature, resolving an "invalid credentials" error that caused automatic backups to fail when using Server Message Block (SMB). The update also enhances the Secure Boot feature by introducing high-confidence device targeting data, allowing more devices to receive new Secure Boot certificates. This update addresses outdated Secure Boot certificates for Windows 11 and Windows 10 users. The update, identified as KB5120249, is under 1 GB and is available only to PCs enrolled in the Extended Security Updates (ESU) program, which ensures Windows 10 PCs receive security updates until at least October 2027. Non-enrolled PCs lost security update support in October 2025.
Winsage
August 12, 2026
Microsoft's August Patch Tuesday update addressed 421 vulnerabilities across various products, including multiple versions of Windows (11 25H2/24H2, 11 23H2, and 10). A critical zero-day flaw, the "Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability," allows attackers with lower-level access to gain system privileges without user interaction. Additionally, the update addresses two other zero-day flaws, including the "Windows User Profile Service Elevation of Privilege Vulnerability," which has not yet been exploited but was publicly disclosed. The update is mandatory and should automatically install on supported PCs, with users encouraged to verify its application. The update also includes minor improvements to Windows features, such as enhancements to File Explorer, Windows Hello, Voice Access, and touchpad controls.
Search