Exchange Server

Winsage
October 19, 2026
Organizations using on-premises Microsoft Exchange Server are experiencing stability issues after the October 2026 Windows Server updates, which Microsoft has confirmed can lead to unreliable Exchange services, especially in environments with heavier workloads. Administrators have reported problems such as connectivity failures with Outlook on the web, disruptions in mail flow, and complications with database availability groups (DAG), all emerging post-update. This bug affects Exchange Servers on Windows Server versions 2016, 2019, 2022, and 2025. Microsoft has identified that the issue is related to limitations in Endpoint Mapper requests and has recommended a registry-based mitigation to improve capacity and reduce service degradation. The default limit of 512 simultaneous Endpoint Lookup calls may be insufficient under heavy load. Microsoft is investigating the issue and will provide further information. Organizations are advised to maintain critical security updates while implementing additional mitigation measures and closely monitoring affected systems until a long-term solution is found.
Winsage
October 17, 2026
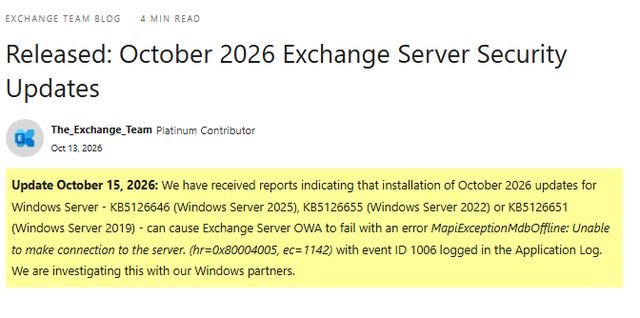
On October 13, 2026, Microsoft released security updates for Windows Server that unintentionally affected Microsoft Exchange Server, causing significant disruptions approximately 24 hours after installation. Users reported issues such as database services failing, resulting in unresponsive email and Outlook Web Access access. Microsoft acknowledged the problem and is investigating it. The updates targeted supported Windows Server and Microsoft Exchange versions 2016, 2019, and SE. By October 15, reports of severe issues, including the inability to connect to the server and halted email delivery, emerged. The error message associated with the disruption is "MapiExceptionMdbOffline: Unable to make connection to the server. (hr=0x80004005, ec=1142)." Despite these issues, the Exchange Admin Center still showed databases as connected and mounted. Unofficial workarounds, including a registry edit and a PowerShell script, have been suggested to mitigate the problems.
Winsage
October 14, 2026
Microsoft's October 2026 Patch Tuesday updates addressed 1,413 vulnerabilities, including 1,102 in Windows, 134 in Office applications, 61 in developer tools, and 36 related to SharePoint Server. This total surpasses the vulnerabilities fixed by Microsoft in all of 2025, with over 4,000 vulnerabilities resolved in 2026. A critical zero-day vulnerability, CVE-2026-96951, with a CVSS score of 8.8, was also patched; it allows attackers to bypass Windows shell security features. The Cybersecurity and Infrastructure Security Agency (CISA) has included this vulnerability in its Known Exploited Vulnerabilities catalog. Additionally, two publicly disclosed vulnerabilities were patched, and Microsoft introduced 'risk cohorts' to help manage security updates.
Winsage
September 9, 2026
Microsoft addressed 974 vulnerabilities in its software suite during its recent Patch Tuesday, marking a record high. The breakdown includes 723 flaws in Windows, 111 in Office, 62 in SQL, and 22 in Developer Tools, with over 110 rated as critical. Two actively exploited vulnerabilities are CVE-2026-85880 and CVE-2026-81963, both allowing local privilege elevation. Other notable vulnerabilities include CVE-2026-55007 (8.1), CVE-2026-80097 (8.6), CVE-2026-69465 (8.8), and several with CVSS scores of 9.6 and above. Microsoft has patched a total of 2,760 security flaws this year, reflecting a trend of increasing vulnerability discoveries. Despite the extensive patching, no significant spike in active exploits has been observed.
Winsage
September 8, 2026
Microsoft released its September 2026 security updates, addressing two critical Windows elevation-of-privilege vulnerabilities: CVE-2026-85880 and CVE-2026-81963. Both vulnerabilities were exploited before their public disclosure on September 8. CVE-2026-85880 involves a heap-based buffer overflow in the Windows Advanced Local Procedure Call (ALPC), allowing low-privileged attackers to gain SYSTEM privileges. CVE-2026-81963 affects the Windows Update Stack due to improper link resolution and access controls, enabling similar privilege escalation. The September release also includes 974 Common Vulnerabilities and Exposures (CVEs) across various Microsoft products, with 723 affecting Windows. Users of Windows 11 24H2 and 25H2 receive updates via KB5124008, while Windows 11 26H1 receives KB5124012. Windows 11 24H2 Home or Pro editions will reach end of servicing on October 13, 2026. Users are advised to install the updates promptly and back up important data.
Winsage
July 16, 2026
Microsoft has released its July 2026 Patch Tuesday updates, addressing 570 new security vulnerabilities, bringing the total for the month to over 620. The cumulative count of vulnerabilities patched this year has reached 1,380, exceeding the total of 1,250 for the entire year of 2020. Over 400 vulnerabilities are related to various versions of Windows, and the Windows 10 Extended Security Update program has been extended until October 12, 2027. Notable vulnerabilities include CVE-2026-56155 in Active Directory Federation Services, which allows attackers to gain administrator rights, and several critical Remote Code Execution vulnerabilities, including CVE-2026-57092 in Hyper-V and CVE-2026-56190 in Remote Desktop Protocol. Microsoft has also patched 97 vulnerabilities in Office products, with 17 classified as critical RCE vulnerabilities, and four vulnerabilities in Exchange Server, including CVE-2026-55008. The latest Microsoft Edge update addresses 27 vulnerabilities related to Chromium, and a vulnerability in Minecraft Bedrock servers has been patched.
Winsage
July 14, 2026
Microsoft released its July 2026 Patch Tuesday cumulative updates for Windows 11, addressing numerous security vulnerabilities and enhancing Secure Boot functionalities. The updates include: - KB5101650 for Windows 11 25H2 and 24H2, updating systems to builds 26200.8875 and 26100.8875. - KB5101649 for Windows 11 26H1, updating devices to build 28000.2525. The release addresses a total of 622 Microsoft Common Vulnerabilities and Exposures (CVEs), including: - 416 vulnerabilities in Windows. - Fixes for Microsoft Office, Edge, Exchange Server, SharePoint Server, SQL Server, Defender, and Azure services. Key vulnerabilities fixed include: - CVE-2026-50661: A BitLocker Security Feature Bypass vulnerability. - CVE-2026-56155: An AD FS Elevation of Privilege vulnerability that has been exploited. - CVE-2026-56164: A SharePoint Server Elevation of Privilege vulnerability. The updates also introduce new Secure Boot certificates, rectify issues from previous patches affecting third-party applications, and incorporate curl 8.21.0 for security improvements. Users are advised to back up data before installation, which requires a system reboot.
Winsage
July 12, 2026
Microsoft will discontinue support for several products in 2026, including: 1. Windows 11 24H2 (Home and Pro) - End of servicing on October 13, 2026. 2. Office 2021 and Office LTSC 2021 - End of support on October 13, 2026. 3. Windows Server 2012 and 2012 R2 - Final ESU year ending on October 13, 2026. 4. SQL Server 2016 - Extended end of support on July 14, 2026. 5. SharePoint Server 2016 and 2019, Project Server 2016 and 2019 - Support ends on July 14, 2026. 6. Microsoft Publisher - Retired after October 2026. 7. Exchange Server 2016 and 2019, Skype for Business Server - Final ESU cutoff on October 31, 2026. 8. Windows 11 Enterprise and Education 23H2, .NET 8, .NET 9, PowerShell 7.4 - End of servicing on November 10, 2026. 9. Windows 10 2016 LTSB and IoT Enterprise LTSB 2016 - Extended support ends on October 13, 2026. 10. Windows 11 SE - Support ends on October 1, 2026. 11. Dynamics CRM 2016 and older versions - Lost support earlier in January 2026. 12. Microsoft Configuration Manager, version 2409 - End of support on June 6, 2026. 13. Visual Studio 2022 LTSC channels, versions 17.10 and 17.12 - End of support in January and July 2026, respectively. 14. InfoPath 2013, SharePoint Designer 2013 - End of support on July 14, 2026. 15. Azure service retirements - Occurring in late 2026. Organizations are advised to review their software landscape and plan for transitions to avoid disruptions.
Winsage
June 16, 2026
Cybersecurity researchers have identified two new Windows variants of the SprySOCKS backdoor, named WINDRV and WINPLUS, which were previously thought to be exclusive to Linux systems. Both variants feature hard-coded command-and-control configurations and can communicate via TCP, UDP, and WebSocket protocols. They support over 30 commands for operations such as system information collection and file management. WINDRV employs kernel drivers for stealth, obscuring network connections and allowing TCP traffic diversion. SprySOCKS was first documented by Trend Micro in September 2023, linked to the Chinese state-sponsored threat actor Earth Lusca, also known as FishMonger. The Windows variants belong to version 1.8 of SprySOCKS and utilize a kernel driver named RawWNPF for enhanced stealth. The attack chain begins with an initial access method that drops a batch script, leading to the installation of the backdoor. Evidence suggests these variants may have been used in attacks against government organizations in Honduras, Taiwan, Thailand, and Pakistan between 2023 and 2024. The WINPLUS variant was first detected in July 2024 in Pakistan. There are indications of a potential UEFI bootkit involvement exploiting CVE-2023-24932, a vulnerability in the Windows Boot Manager.
Search