expertise

AppWizard
September 21, 2026
Modder Doneda has created a modification for Elden Ring Nightreign, featuring a standalone map inspired by Frozen Eleum Loyce and Frigid Outskirts from Dark Souls 2. A trailer for this project is available on YouTube. Doneda has a history of modding, having restored a cut sewers map from Dark Souls 2. The new map can be downloaded from the Nightreign Nexus, requiring Mod Engine 3 for installation. Doneda plans to create more maps and invites fans to follow their progress on YouTube or support them on Ko-fi. The recent Deep of Night update in Nightreign has introduced new boss fights, while the community has developed various mods, including Yui's Seamless Co-op and TerraMag's weapon integration from other titles.
Winsage
September 19, 2026
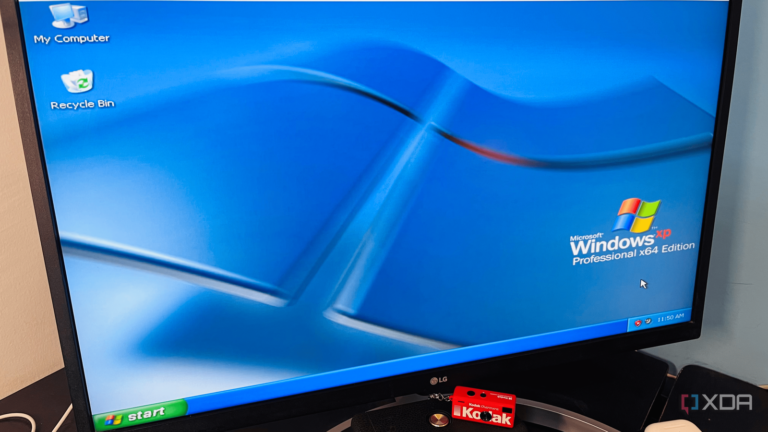
Windows XP was released in two versions: Retail for individual consumers and Volume for Microsoft's partners and OEMs. The product key FCKGW-RHQQ2-YXRKT-8TG6W-2B7Q8 became widely recognized due to a potential leak by an insider at a major OEM, which was then spread by the pirate group Devils0wn. The Volume version's activation system required a unique key, but the FCKGW key was incompatible with the standard installation CD. To verify the legitimacy of Volume discs, the activation system searched for a secret 10MB binary blob exclusive to the Volume media. Microsoft blacklisted the FCKGW key with Service Pack 1 and implemented further security measures with Service Pack 2, restricting access to certain updates. Contrary to prior beliefs, the key's functionality was not due to a simple key generation algorithm but was designed by skilled engineers.
AppWizard
September 16, 2026
9to5Toys is a platform that provides insights and deals for technology and lifestyle enthusiasts. It offers a homepage for news and updates, and engages with followers on social media platforms like Twitter, Facebook, and LinkedIn. Key resources include a section for the best Apple deals, a daily podcast discussing tech news and product reviews, and a YouTube channel for product unboxings and reviews.
Tech Optimizer
September 12, 2026
If you hold Microsoft 365 E5, you already have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended. CrowdStrike is suitable for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses without IT staff, VIPRE for budget-conscious organizations, and Expel for tool-agnostic managed detection and response. It is essential to assess your organization's current situation honestly when evaluating endpoint protection options. Antivirus and EDR are now essentially the same agent, and organizations should inquire about update staging processes and review independent tests for protection rates. Coverage for servers and Linux environments is often overlooked but crucial, as Linux servers are prime targets for ransomware. Key recommendations include: - Microsoft Defender for Endpoint for organizations already on Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a well-funded security operations function. - SentinelOne for mid-sized organizations needing autonomous operation. - ESET for organizations with older hardware or virtual desktop infrastructure. - Avast Business for micro and small businesses. - VIPRE for budget-conscious organizations. - Expel for those seeking managed detection across various environments. During deployment, avoid running two real-time agents simultaneously, ensure prevention features are activated, and test on line-of-business applications first. Verify update staging and rollback procedures with vendors, and confirm whether Microsoft licensing covers your needs to avoid unnecessary purchases.
Tech Optimizer
September 10, 2026
If an organization holds Microsoft 365 E5, it already has access to Microsoft Defender for Endpoint. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly management. CrowdStrike is preferred for those with a mature Security Operations Center (SOC) and sufficient budget. The choice of endpoint protection depends on specific organizational needs. Business endpoint protection integrates various technologies to defend against malware and attacks on devices. Organizations should assess their current situation before selecting a solution. Key recommendations include: - Microsoft Defender for Endpoint for organizations already using Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a funded SOC. - SentinelOne for mid-sized organizations needing automation. - ESET for those with older hardware or virtual desktops. - Avast Business for very small businesses lacking IT staff. - VIPRE for budget-conscious organizations needing straightforward coverage. - Expel for organizations wanting managed detection across diverse environments. Organizations should avoid running multiple real-time agents simultaneously and ensure prevention features are activated. Testing should prioritize line-of-business applications, and rollout procedures should be defined before going live. It’s essential to verify update staging and rollback procedures with vendors and confirm existing licenses to avoid unnecessary purchases.
Tech Optimizer
September 10, 2026
If you hold Microsoft 365 E5, you have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly platform. CrowdStrike is suggested for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses, VIPRE for budget-conscious mixed estates, and Expel for tool-agnostic managed detection and response. Antivirus and EDR are now unified under a single agent, and organizations should inquire about update staging processes to avoid issues like those experienced in July 2024 with a major vendor's faulty content update. Independent tests from organizations like AV-Comparatives and AV-TEST are crucial for evaluating protection rates and false positives. Linux servers require attention as they are often targeted by ransomware. When deploying endpoint protection, avoid running two real-time agents simultaneously, activate prevention features promptly, and test deployments on critical applications first. Organizations should confirm their Microsoft licensing covers necessary features and ensure there is a plan for responding to alerts. Common pitfalls include neglecting identity management and failing to test response workflows before incidents occur.
Winsage
September 8, 2026
Several pathways exist to expedite the official rollout of Windows updates. Users can navigate to Windows Update settings to enable the latest updates, install optional preview updates manually, join the Windows Insider Program for pre-release versions, or use ViveTool to unlock hidden features. 1. Enable the latest updates: A toggle in Windows Update settings allows users to receive new features and updates as soon as they are available. 2. Install optional updates: Preview updates are released towards the end of each month and can be installed manually through Windows Update. 3. Use Windows Insider: The Insider Program offers pre-release versions of Windows, with the Beta Channel for innovation and the Release Preview Channel for stability. 4. Enable hidden features with ViveTool: This tool unlocks features already present in Windows but not activated, requiring technical expertise. Activating the toggle in Windows Update prioritizes the device for new features while ensuring essential security updates continue.
Search