exploits

Tech Optimizer
October 10, 2026
In gaming, tools such as utilities, beta applications, and modding tools are often distributed as APK, IPA, or desktop files, and it is essential to investigate their origin, version, and any security warnings before installation. Antivirus software flags potential threats based on known malicious signatures, behavior patterns, and reputation data. Tools that modify game clients may receive heightened scrutiny, and classifications like “HackTool” or “Riskware” do not definitively indicate a file's functionality. Identical game utilities can exist on various platforms, and a familiar website does not guarantee authenticity. It is crucial to verify the publisher, update date, version, and installation method of a file. The SHA-256 hash verifies file integrity but does not ensure safety from malware. Calculating a file hash can be done using specific commands in Windows, macOS, or Linux. Multi-engine scanning platforms like VirusTotal provide insights, but a lack of detections does not guarantee safety. Even if a file matches its reference hash and raises no alerts, it may still violate online game terms. A pre-installation checklist includes confirming the publisher, checking file types, comparing SHA-256 hashes, reviewing security findings, keeping antivirus protection enabled, and consulting platform rules. A cautious approach integrates source verification, file integrity checks, security assessments, and compliance with platform regulations.
Tech Optimizer
September 23, 2026
A new tool named BigDiskBuster has been released on GitHub, which disrupts Microsoft Defender Antivirus by preventing it from installing updates. It does this by consuming available disk space during the update process, causing Defender to remain on its current version and unable to receive new platform or signature updates. BigDiskBuster operates as a local denial-of-service technique and requires prior access to the target machine to execute. The tool was created by researcher Abdelhamid Naceri, known as Nightmare Eclipse, who has previously worked on similar projects. As of now, there is no CVE identifier, patch, or advisory from Microsoft regarding this issue.
Winsage
September 23, 2026
Security researcher Abdelhamid Naceri, known as Nightmare Eclipse, released a zero-day exploit called BigDiskBuster that targets Microsoft Defender, preventing antivirus updates and leaving systems vulnerable. BigDiskBuster operates across all supported Windows versions and must run in the background to block updates. Naceri has previously released a similar exploit called UnDefend and has a history of releasing multiple zero-day exploits since April 2026 amid a dispute with Microsoft. Two weeks before BigDiskBuster, he introduced another exploit named ShieldCrash, which grants SYSTEM access and circumvents a patched flaw. Naceri's recent exploits include tools like LegacyHive, BlueHammer, RedSun, YellowKey, GreenPlasma, and MiniPlasma, all targeting Microsoft Defender and other Windows components. Microsoft has warned of potential legal action against malicious activities but has not commented on BigDiskBuster.
Tech Optimizer
September 21, 2026
More than 5,400 websites across over 2,200 organizations have been compromised to propagate malware, primarily affecting small businesses like clinics and online retailers. The attack mechanism involves malicious code that triggers a deceptive CAPTCHA, instructing users to execute commands that can download malware. Attackers are using the BNB Smart Chain test network to store instructions, making it harder for investigators to shut down operations. A newer variant of the attack uses WebRTC technology to establish encrypted connections for delivering additional malicious code. To protect against these threats, users should avoid pasting commands from websites, be suspicious of unusual CAPTCHA instructions, use strong antivirus protection, keep systems updated, take action if commands are executed, and small business owners should regularly verify their website's integrity.
AppWizard
September 19, 2026
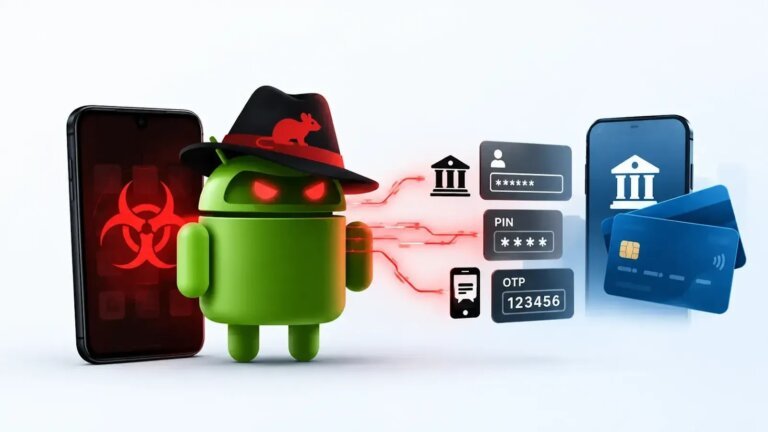
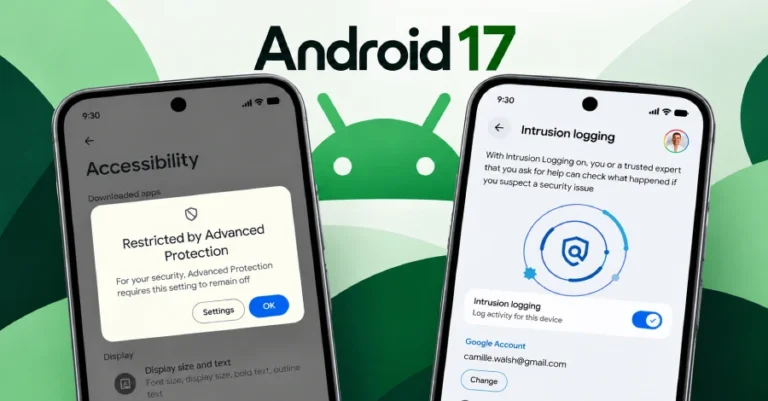
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
Winsage
September 15, 2026
A spear-phishing campaign linked to the Chinese threat actor UTA0560 targeted various NGOs on September 1, 2026, exploiting recently patched vulnerabilities in Google Chrome and Microsoft Windows. The campaign utilized a malicious JavaScript backdoor called GRIMWEDGE, which was deployed through a multi-stage exploit chain that involved three vulnerabilities: CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880. The attack began with spear-phishing emails that led recipients to a vulnerable U.S.-based university website, allowing attackers to redirect users to their infrastructure. The exploit chain enabled arbitrary code execution and facilitated the deployment of GRIMWEDGE, which is capable of host reconnaissance, file and process management, command execution, and payload delivery. The initial payload was an executable named "msgbox.exe," which extracted a legitimate Windows binary and a malicious DLL called "wsc.dll." This DLL initiated a sideloading chain and contacted a command-and-control server for further instructions. GRIMWEDGE allows for several commands, including system reconnaissance, directory listing, file deletion, and command execution in a hidden window. It lacks built-in persistence or lateral movement mechanisms but provides a foothold for further exploitation. Concurrently, another Chinese threat actor, JungleBamboo (APT31), used the same exploit chain to deploy a loader named SUPERSTOMP, which installs a credential-stealing Chrome extension called LONGTALE. The simultaneous use of the exploit chain by multiple actors suggests potential sharing or sale of the exploit, raising concerns about patch-gap vulnerabilities that pose risks for exploitation campaigns.
Search