A research team from Turkey, led by Erdal Başaran and Ömer Okucu of Ağrı İbrahim Çeçen University, along with Yusuf Alaca from Hitit University, has developed an innovative detection framework for Android malware that utilizes a visual approach. This framework transforms key features of Android applications into images, allowing a Vision Transformer to differentiate between benign software and malware. The researchers created two types of images from static and dynamic analysis features: a conventional 2D grayscale image and a QR code image. Separate Vision Transformer models were trained on each image type, and spatial pooling features were extracted from deeper layers to create a comprehensive representation of application behavior.
To refine the fused feature vector, Recursive Feature Elimination (RFE) was employed, enhancing classification clarity and reducing computational load. The final classification utilized a majority-voting ensemble strategy, achieving a detection accuracy of 98.72 percent, surpassing standalone models. The study demonstrates that the multimodal system outperforms individual grayscale or QR code pathways. The dataset used is publicly available, promoting reproducibility. The framework's reliance on static and dynamic analysis features allows it to adapt to new threats, and the novel QR code representation offers distinctive visual signatures of malicious behavior. However, challenges remain regarding feature extraction quality and computational demands.
FOV 90 discusses the first-person shooter (FPS) genre, highlighting its history, community traditions like organized scrimmages, and various gameplay modes. The column features a voting round with matchups between different FPS modes, including Team Deathmatch vs. FFA/Deathmatch, Battle Royale vs. Extraction, Conquest vs. Domination, Bomb Defusal vs. Hostage, Gun Game vs. Payload, Infection vs. Prop Hunt, VIP vs. Capture The Flag, and Attack & Defend vs. King of the Hill. Voting closes on Saturday, October 3 at 11:59 PM PDT, with results to be revealed the following week.
The world of video game journalism is thriving, with a variety of new PC game releases showcasing creativity and innovation. Notable new titles include:
- Camp Whittlewood: A pixel-art horror RPG featuring cub scouts on a camping adventure without typical horror tropes.
- HR: Human Remains: Players navigate Hell as an office clerk managing a to-do list amidst a war between humans and demons.
- Yots: A co-op extraction game set in a procedurally generated city reminiscent of the PS1 era and Silent Hill.
- Drop Command: Combines cockpit combat with 90s Mechwarrior and 4X gameplay elements.
- Nivalis Nights: A cyberpunk restaurant management simulation with lush visuals.
- Toem 2: A sequel featuring gentle platforming and photography puzzles.
- Transport Fever 3: A detailed simulation game focused on trains.
- Tiny Flock: A VR shepherding simulation with whimsical elements.
- Radiosol: Players control a mechanical spider in a world of dusty megastructures, utilizing generative AI for multilingual support.
- Okko The Exiled: A 2D visual game featuring a small protagonist with a large club.
- Songs of Glimmerwick: A witch school RPG combining magic and music.
- By God Alone: An expansion for Crusader Kings 3 allowing players to control the Vatican.
- Dynasty Warriors 3: Complete Edition Remastered: Revives the classic musou experience with enhanced graphics.
- RetroSpace: A survival game set aboard a space station drawn into a black hole.
- Ace Combat 8: Wings of Theve: The latest installment in the aerial combat franchise.
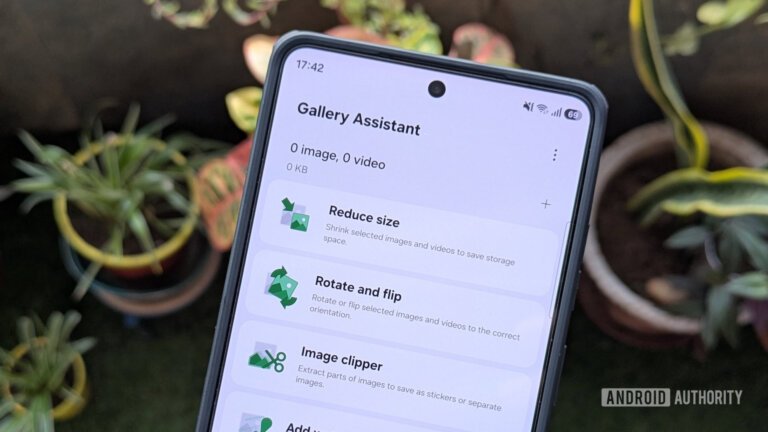
Samsung's Gallery app now includes advanced editing features, allowing users to edit images and videos, create collages and GIFs, and remove backgrounds. A hidden feature called Gallery Labs offers album-entry locks and the ability to save images as PDFs. The Gallery Assistant, part of Samsung's Good Lock, enhances the app with batch processing capabilities and seven new tools:
1. Reduce size - compresses images and videos.
2. Rotate and flip - bulk rotation and flipping of images.
3. Image clipper - extracts subjects from images.
4. Add watermark - adds customizable watermarks to images.
5. Compare images - side-by-side comparison of similar images.
6. Save as PDF - converts images into PDFs with customizable options.
7. Print - simultaneous printing of multiple images.
Gallery Assistant integrates with Enhance-X for improved image and video quality. Users can access it through the Good Lock app, and it allows rearranging tool order for convenience. Users appreciate its features but suggest improvements like format conversion and EXIF metadata editing.
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox.
The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception.
Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client.
The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
- Mobile version of Dome Keeper, a popular mining survival game, is in the works
- Pre-registration is open on Google Play and pre-orders are available on the App Store for 899 rubles
- Dome Keeper involves balancing resource extraction and defense against alien attacks
- Players can enhance the dome, upgrade mining equipment, and increase movement speed with materials found
- Procedurally generated maps offer a unique experience with each new run
- Dome Keeper was originally released on Steam in 2022 and has sold over a million copies by October 2024
Between December 2025 and August 2026, a coalition of advanced threat actors exploited the Claude AI model by extracting sensitive information from approximately 1.8 million Android applications. The operation involved groups such as ShinyHunters, Midnight Blizzard (APT29/Nobelium), and the Chinese-speaking entity GTG-10007. They automated the mass download, decompilation, and analysis of Android APKs for hardcoded credentials, API keys, and authentication tokens, leading to extensive credential theft and breaches across various sectors.
The attack utilized a distributed pipeline on ten AWS EC2 instances to download APKs, which were then scanned using TruffleHog. Verified secrets were organized and routed in real-time to a private Telegram group for operational deployment. Over 2,100 Azure AD authentication tokens were extracted from more than 40 Microsoft tenants within 34 hours. The operation also included a carding component where stolen payment card data was sold.
The tactics employed aligned with several MITRE ATT&CK techniques, including file discovery, unsecured credentials, valid accounts, phishing, and exploitation of remote services. ShinyHunters gained administrative control over targeted environments rapidly, leading to bulk data theft affecting over 200 organizations. Midnight Blizzard automated malware creation and phishing campaigns, targeting government and defense entities. GTG-10007 used Claude for coordinated offensive operations, discovering zero-day vulnerabilities and delivering exploits.
Initially, the campaign targeted a broad range of Android APKs but later focused on organizations with valuable credentials across various sectors, including government, technology, and healthcare. Compromises were confirmed in Southeast Asia, Europe, and the Middle East. Organizations are advised to audit Android applications for hardcoded secrets, monitor API key usage, and implement robust security practices to mitigate risks.
An ongoing malware campaign is targeting Windows devices through counterfeit download pages for well-known software brands like Microsoft Edge, Kaspersky, and Razer. The campaign affects various sectors, including healthcare, manufacturing, gaming, technology, logistics, government, and education. It utilizes high-fidelity fraudulent websites that closely mimic legitimate vendors, with observed lure domains such as app-microsoft-edge[.]com[.]cn and kaspersky-lab[.]hl[.]cn. Attackers employ evasion tactics like server-side payload regeneration and create multiple copies of the same archive in quick succession.
Victims are lured into downloading ZIP files that contain a bundled wrapper installer, which activates a stage-one executable in randomized directories. The malware often masquerades as legitimate software, with some payloads impersonating known applications. Persistence is achieved through scheduled tasks with unusual names, and the malware employs various evasion techniques, including deleting shadow copies and altering file permissions.
Microsoft Defender has identified activity across multiple stages of the attack, including delivery, execution, and command-and-control communications. To mitigate risks, organizations are advised to block downloads from unofficial sources, enforce Tamper Protection, and implement Attack Surface Reduction rules. Indicators of compromise (IOCs) include specific lure domains and URLs associated with the campaign.
- The Blood of Dawnwalker, an action-RPG by Konrad Tomaszkiewicz, will launch on September 3, 2026.
- Onimusha: Way of the Sword will be released on September 4, 2026.
- WARDOGS, a first-person shooter, is set to release on September 10, 2026.
- CONTROL Resonant will debut on September 24, 2026.
- Nivalis Nights, a life simulator in a cyberpunk city, will be available on September 29, 2026.
- BOMBANANA! will be released on September 2, 2026.
- Aniimo, an open-world RPG, is scheduled for September 16, 2026.
- Graveyard Keeper 2 will launch on September 22, 2026.
- Wanderburg, a roguelike adventure, will be available on September 8, 2026.
- Active Matter, an extraction shooter, is set for release on September 15, 2026.
- Transport Fever 3, a transport tycoon simulator, will be released on September 29, 2026.
- Crimson Moon, featuring a Nephilim character, will be available on September 1, 2026.