factory

AppWizard
September 22, 2026
Cybersecurity researchers at Zimperium have identified a new strain of malware called RatHat, targeting Android devices and linked to threat actors from China. RatHat uses generative AI to maintain persistence and control over infected devices. The malware is typically spread through social engineering, tricking users into downloading counterfeit applications that appear legitimate. Once installed, RatHat requests accessibility permissions, activates Wireless Debugging, and can capture text messages, create overlays, and steal passwords and multi-factor authentication codes. Its AI capabilities allow it to navigate the device interface in real-time, making detection by security software more difficult. To protect against RatHat, users should avoid downloading apps from untrustworthy sources, and removal requires a factory reset of the device.
AppWizard
September 19, 2026
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
AppWizard
September 19, 2026
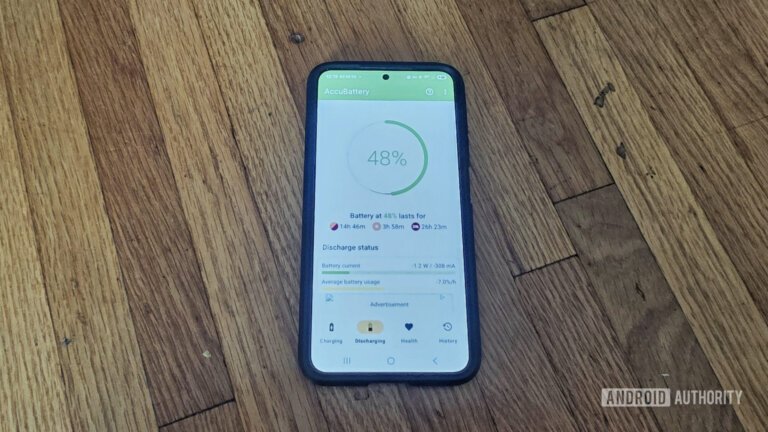
AccuBattery is a battery management app that helps users identify and diagnose software and hardware issues draining their device's battery. It offers a distinct approach by using pattern recognition over time for data gathering, which can yield more accurate insights compared to built-in tools. AccuBattery provides detailed statistics, including mAh consumption of each app, current, temperature, and voltage, facilitating easier diagnosis of potential hardware issues. Users can benefit from using AccuBattery alongside built-in tools, as each may catch what the other overlooks. The app includes a charge alarm feature that notifies users when their battery reaches 80%, promoting better battery longevity. However, AccuBattery relies on observational data, which may not always be perfectly accurate. It is not categorically superior or inferior to built-in tools but offers depth of detail that can be beneficial for users facing persistent battery issues.
Tech Optimizer
September 15, 2026
Iranian state-sponsored hackers are targeting dissidents, activists, and journalists using deceptive tactics, including malicious applications that impersonate reputable cybersecurity products like Norton Antivirus and KeePass. The FBI and UK authorities issued a warning about these hackers, who establish rapport with targets via social messaging platforms, posing as IT support or known contacts. They convince victims to download files that appear authentic, including AI video creation applications and other software. The spyware, named “Chosen Brick,” infects Windows PCs and has capabilities such as capturing screen content, recording audio, collecting message data, and downloading additional malware. The hackers have exploited this spyware to publish personal details of victims, increasing their harassment. The FBI advises potential victims on detecting the spyware and recommends enabling antivirus software, running regular scans, and avoiding unofficial downloads.
AppWizard
September 2, 2026
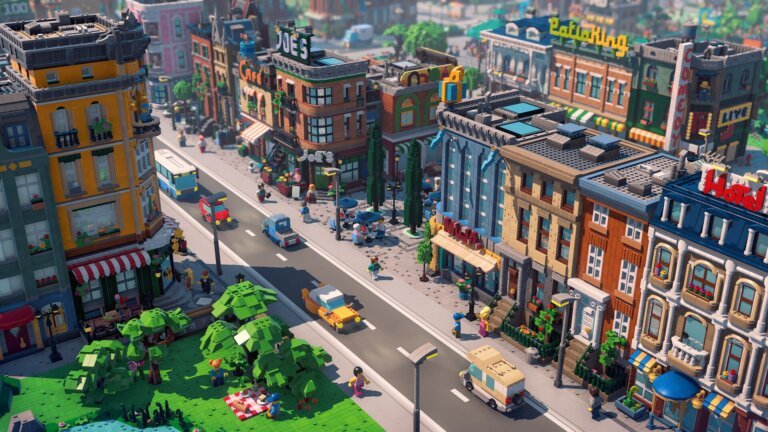
Lego unveiled a new city builder game titled Lego Skylines at Gamescom. The early gameplay preview lasted about 35 minutes, allowing players to construct a small neighborhood with a maximum population of around 50 residents. The game features whimsical animations for building and demolishing structures, vibrant visuals, and customization options for enhancing resident happiness through decorations. Players can complete quests to engage with the community and unlock new building types. Resource management involves constructing farms and factories to create supply chains, with a playful aesthetic evident in the design of buildings like a bread factory resembling a giant toaster. The game allows for a larger city scale of around 2,400 residents across several islands but focuses on a relaxed gameplay experience without catastrophic events.
AppWizard
September 2, 2026
During a summer internship at a fireworks factory, the author noted that celebrations are enhanced by vibrant colors. The Rainbow Eclipse PvP Pack by CubeCraft Games includes animated swords and armor with various colors, low fire, and short swords. The Steampunk - Original Textures pack by The Craft Stars features a retrofuturistic steampunk aesthetic. Pastel Adventures by Pathway Studios offers a pastel color palette, a custom user interface, adorable mobs, and 12 unique pastel skins. The Cube Chaos texture pack by Pathway Studios captures the essence of classic comic books. The Cherry Bonsai Treehouse by CrackedCubes provides a treetop base with cherry blossoms and unique textures. The Cute Cozy House by Heropixel Games features a dreamy design and adorable furniture. The Cityscapes Las Vegas pack by Octovon allows exploration of iconic landmarks and opulent resorts. The City Life pack by Kora Studios showcases sprawling apartment complexes and bustling city streets. The Cursed Woodland Mansion by Pathway Studios is a cleverly designed escape room set in a haunting woodland mansion. Space Mini-Golf by Waypoint Studios includes 100 distinct holes for intergalactic golfing. Mega Prehistoric Parkour by Jigarbov Productions combines parkour with baby dinosaurs. The Cute in Pink! pack by Pixel Squared offers 10 fashionable pink skins. Sakura Bliss by Yeggs features 12 cherry blossom-themed skins. The Angels vs Devils pack by Pixel Squared includes 12 skins embodying heavenly or hellish aesthetics. The Spooky Season pack by StudioU provides 13 eerie skins for Halloween. Additionally, there is a selection of Character Creator items crafted from gold.
AppWizard
September 1, 2026
Cybercriminals are targeting Android users with deceptive advertisements for malicious applications disguised as pornographic content on platforms like Facebook and Instagram. The National Cybercrime Threat Analytics Unit (NCTAU) has reported that these ads lead users to phishing traps or malware downloads that can compromise banking credentials. Malicious applications linked to this threat include “Night Play,” “Reloop,” “Kyss,” “Vimo,” “Rivo,” “Nexo,” and “Vixa.” The scam involves promoting these apps through enticing ads, redirecting users to websites offering pornographic content, and prompting them to download APK files directly from these sites, often using “.live” domains. The initial app may request users to download a second package disguised as an update, which can exploit permissions granted to the first app. This malware can gain extensive control over the device, potentially installing a VPN that routes internet traffic through attackers' servers. To protect against this threat, users should download apps only from trusted sources, avoid installing APK files from ads or suspicious links, refrain from granting Accessibility access to unknown apps, regularly review installed apps, keep Google Play Protect enabled, and monitor bank accounts for unusual activity. If a suspicious app cannot be uninstalled, users can try Safe Mode, remove special permissions, or perform a factory reset as a last resort.
AppWizard
August 31, 2026
India's cybercrime authorities have warned about the misuse of dating and adult-themed advertisements on social media platforms like Instagram and Facebook, which are being exploited by criminals to distribute malicious Android applications. These ads redirect users to external websites where they are prompted to download APK files, bypassing security measures of trusted app stores. The Indian Cybercrime Coordination Centre (I4C) has identified several malicious applications, including Night Play, Reloop, Kyss, Vimo, Rivo, Nexo, and Vixa, and cautions against installing unfamiliar applications promoted through unsolicited ads. These apps may request sensitive permissions, such as access to SMS messages, contacts, photos, device storage, and Accessibility Services, which can allow fraudsters to access valuable information. Compromised devices can lead to financial fraud by intercepting OTPs and other verification details. The I4C recommends using trusted app stores, keeping Google Play Protect active, reviewing app permissions, and being cautious with social media ads. If a suspicious app is installed, users should restart their phone in Safe Mode to uninstall it, disable its permissions if necessary, and consider a factory reset if removal fails. Users who suspect fraud are encouraged to report incidents promptly.
Search