fake websites

Winsage
September 24, 2026
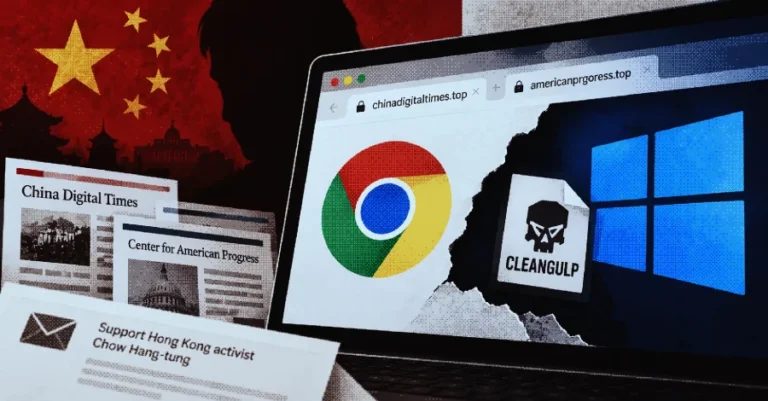
A Chinese threat actor, codenamed UTA0565, has exploited newly disclosed vulnerabilities in Google Chrome (CVE-2026-85046, CVE-2026-87491) and Windows (CVE-2026-85880) through deceptive websites, achieving remote code execution. The attacks were detected on September 3 and 4, 2026, and involved impersonating organizations to mislead victims, particularly targeting Asian government entities with phishing emails related to Hong Kong activist Chow Hang-tung. The phishing messages directed users to fraudulent sites that loaded an HTML element using the BlueMoon exploit kit, which delivered a payload named "chrome_cleanup.exe," associated with the CLEANGULP malware family. This malware allows for command execution, process listing, file uploads and downloads, and uses a hard-coded domain for command-and-control communications. The exploit's widespread use suggests a coordinated effort within the Chinese cyber espionage community, with indications that multiple groups are sharing and weaponizing the exploit.
AppWizard
June 9, 2026
Old-school gaming consoles are seeing a resurgence, but hackers are exploiting this trend with a malware campaign called "WeedHack," which emerged in January. This malware operates on a "Malware-as-a-Service" model, allowing users to purchase it to infect victims. WeedHack functions as a remote access infostealer, compromising computers to manipulate screens, access webcams, and steal sensitive data. It propagates by enticing users with unofficial "Minecraft" mods and clients, often using videos and download links as bait. Additionally, it employs "SEO poisoning" to promote fake websites as legitimate sources for these mods on platforms like Discord and Reddit. WeedHack disguises itself as a JAR file, similar to the official "Minecraft" client, and once executed, it installs its payload from Ethereum server domains. It can insert itself into antivirus exclusion lists, evading detection, and McAfee's tests show that Windows Defender is ineffective against it. The malware collects extensive information, including Wi-Fi networks and browser cookies, and grants hackers complete control over infected computers. The WeedHack virus serves as both malware and a training ground for aspiring hackers, structured into two tiers: a free version with core capabilities and a paid subscription for advanced features. A community has formed around WeedHack, offering tutorials, a Discord server, and a website for feature requests and custom payload creation. This community aspect lowers the barrier for newcomers, particularly targeting a younger audience that may not understand online safety.
AppWizard
June 4, 2026
A recent cybersecurity analysis from McAfee Labs has revealed a malware campaign involving WeedHack, which has garnered over 116,000 hits and is accumulating 2,000 to 3,000 malicious hits daily. WeedHack is marketed as malware-as-a-service (MaaS) and is accessible on the internet, allowing individuals with minimal technical skills to use it for harmful activities. A dedicated Telegram channel for WeedHack has over 850 members, many of whom are teenagers and young adults using the malware for cyberbullying. The malware spreads primarily through YouTube videos promoting Minecraft mods, which often conceal the WeedHack malware. Additionally, bad actors use SEO poisoning tactics to elevate fake websites posing as legitimate Minecraft clients. McAfee lists several legitimate clients targeted by WeedHack, including Meteor Client, Radium Client, and Wurst Client. For an additional fee, attackers can access premium features like webcam access, keylogging, and file management. McAfee advises players to be cautious when downloading mods and to seek help from trusted adults if approached by individuals claiming to have compromised their systems.
Search