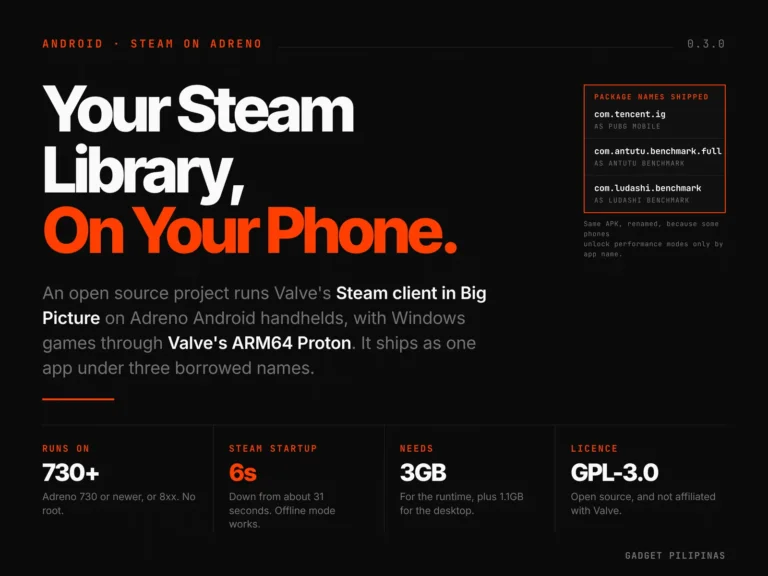
DroidDeck is an open-source project that allows users to run Valve's Steam client in Big Picture mode on Adreno Android devices and play Windows games through Valve's ARM64 Proton.
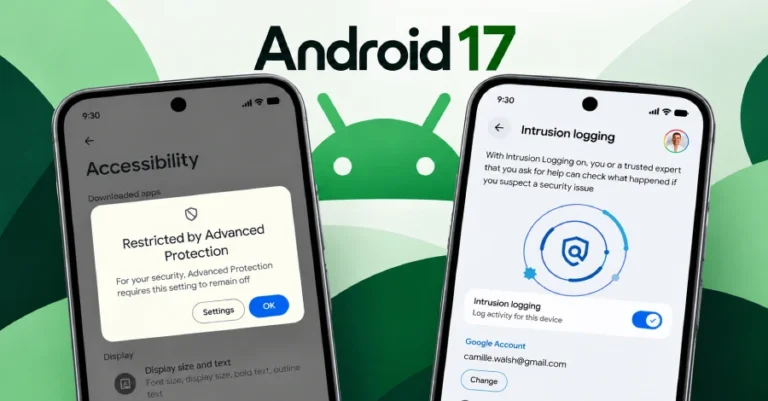
Google has enhanced its Android security framework by restricting access to the AccessibilityService API, allowing only verified applications classified as Accessibility Tools to use these features when Advanced Protection is activated. This decision addresses the misuse of the AccessibilityService API by malicious applications that facilitate malware distribution and financial fraud. The new measures include Intrusion Logging, USB Protection, disabling WebGPU, and a Failed Authentication Lock. Developers will be notified when Advanced Protection is enabled, and users can manually enable Intrusion Logging through the Advanced Protection settings page.
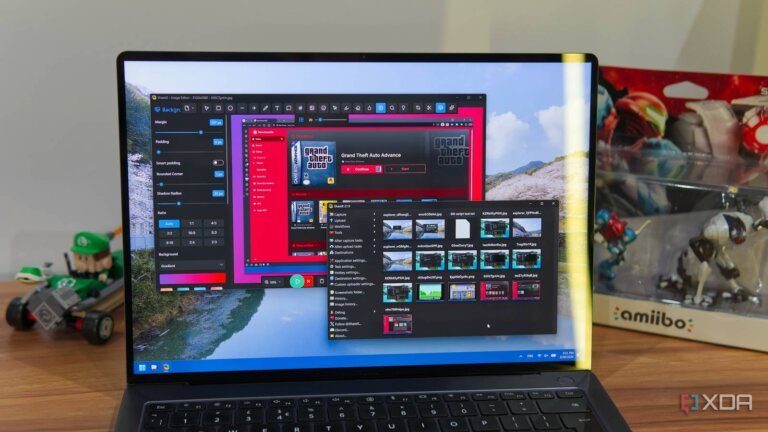
The Snipping Tool in Windows has been modernized in Windows 11 but still has bugs that can disrupt user workflow. ShareX is a free and open-source alternative that excels in screenshot capabilities and offers advanced features, including precise selection tools, real-time editing, video recording, and GIF creation. ShareX supports multiple upload targets, including Imgur and cloud services like OneDrive and Google Drive, and allows users to upload various file types, including text documents to Pastebin. It includes bonus features such as a video converter, image comparison tools, and customization options for hotkeys. However, ShareX may be overwhelming for newcomers seeking basic screenshot functions, for whom the Snipping Tool remains a valid choice.
A young gamer known as Mighty Mike Plays has claimed to have accumulated over ,000 in credit card debt on his father's company card due to expenditures related to promoting his Minecraft gaming account. His father, Dave, has stated that he was unaware of these charges and that the family is facing financial repercussions, including Dave's reported job termination. They have since launched a merchandise store to help recover the losses. However, skepticism regarding the authenticity of their claims has emerged, with critics suggesting inconsistencies in their narrative. Additionally, Dave has threatened legal action against those questioning their story.
Norton, Bitdefender, and Malwarebytes have adjusted their antivirus products to mitigate the negative effects on gaming performance. In June 2026, Norton 360 and Bitdefender Total Security both received a perfect AV-TEST score of 18 out of 18, while Malwarebytes achieved a 100% real-world protection rate in AV-Comparatives testing, though it had more false positives. Bitdefender Total Security is recommended for gamers due to its low frame-rate impact of 0-2%, while Norton 360 offers features for streamers and competitive players, and Malwarebytes serves as a lightweight secondary scanner.
The value of gaming accounts has increased, making them targets for cybercriminals, with malware campaigns like Vidar 2.0 accounting for 41% of gaming-related malware detections. New malware families such as Katz and Bee specifically target Discord and gaming platforms.
In terms of performance, Norton showed a 2-3% FPS decrease in Cyberpunk 2077, while Bitdefender's impact was only 0-2%, and Malwarebytes had less than 1% impact. Norton and Bitdefender are tied in detection capabilities, both scoring 18/18 in AV-TEST, while Malwarebytes had a 92.4% offline detection rate and 98.3% online.
Norton includes a no-log VPN and gamer-tag monitoring, while Bitdefender offers identity protection without specific gamer-tag monitoring. Malwarebytes lacks a VPN and password manager. Pricing varies, with Norton starting at .99 for three devices, Bitdefender at .99 for one device, and Malwarebytes at .99 for one device.
To switch antivirus solutions, users should back up their license keys, use removal tools, and ensure game-aware modes are active. Each product has unique strengths: Norton excels in gamer-tag monitoring, Bitdefender minimizes CPU usage, and Malwarebytes is lightweight but lacks additional features.
Cybercriminals have developed an infostealer called MacSync, targeting Mac devices by using iCloud calendar events and cloud storage. This malware disguises itself as fake cryptocurrency wallets and pirated software. It begins with a loader that retrieves instructions from calendar entries and deploys malware to exfiltrate sensitive information, including credentials and cryptocurrency wallets. Recent versions have introduced an Objective-C backdoor that mimics Finder. Victims are often tricked into downloading these malicious applications, and effective antivirus solutions can prevent damage. Cybercriminals use tactics like SEO poisoning and phishing to direct victims to fraudulent websites or social media promoting pirated software. In one case, the loader was marketed as a cryptocurrency wallet, and victims encountered a misleading ClickFix error message that prompted them to execute a command in the Terminal.
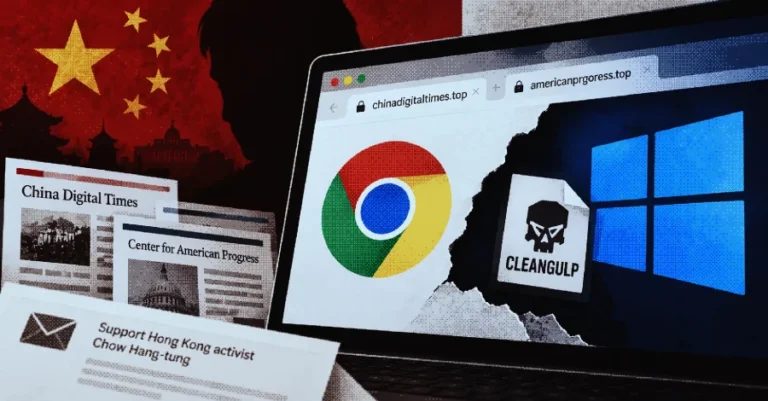
A Chinese threat actor, codenamed UTA0565, has exploited newly disclosed vulnerabilities in Google Chrome (CVE-2026-85046, CVE-2026-87491) and Windows (CVE-2026-85880) through deceptive websites, achieving remote code execution. The attacks were detected on September 3 and 4, 2026, and involved impersonating organizations to mislead victims, particularly targeting Asian government entities with phishing emails related to Hong Kong activist Chow Hang-tung. The phishing messages directed users to fraudulent sites that loaded an HTML element using the BlueMoon exploit kit, which delivered a payload named "chrome_cleanup.exe," associated with the CLEANGULP malware family. This malware allows for command execution, process listing, file uploads and downloads, and uses a hard-coded domain for command-and-control communications. The exploit's widespread use suggests a coordinated effort within the Chinese cyber espionage community, with indications that multiple groups are sharing and weaponizing the exploit.
A newly identified strain of Android malware, RatHat, utilizes generative AI to manipulate infected devices in real time. It is linked to threat actors believed to be operating out of China. RatHat serializes the device’s live Accessibility tree into XML format and communicates with a generative AI assistant to return screen coordinates, identify text, and issue navigation commands. The malware employs WebView-based HTML overlays to capture login credentials from banking and cryptocurrency applications and can infiltrate payment apps like WeChat and Alipay to extract PINs. It also features an SMS receiver and notification listener to intercept OTPs and 2FA codes.
RatHat is disseminated through smishing, malvertising campaigns, and misleading third-party forums. It employs anti-analysis techniques such as container tampering, manifest bombing, DEX bytecode poisoning, string encryption, and anti-debugging. Once installed, it gains Accessibility access, activates Developer Options, and enables Wireless Debugging, allowing it to connect to the device's local ADB service and launch control agents with shell-level privileges.
The malware captures raw touch coordinates to reconstruct PINs and unlock patterns, bypassing screenshot protections. It also includes persistence mechanisms that prevent uninstallation by presenting a fake Google Play failure overlay and automatically reinstalling itself if removed.
LastPass has identified a sophisticated scheme targeting users of its Authenticator app, involving SEO poisoning and deceptive GitHub pages that distribute malicious ZIP files disguised as legitimate software. Users searching for "LastPass Authenticator download" may encounter these counterfeit pages, which redirect them to a malicious server delivering a ZIP file containing vsdbg.exe and vsdbg.dll. The executable is a legitimate Microsoft debugging tool exploited to execute the malicious DLL through DLL sideloading, allowing the malware to run undetected.
Named Rapuncel by security researchers from Delphos, this malware is undetectable by antivirus engines and targets a hardcoded list of 145 antivirus and endpoint security products, disabling them upon detection. Rapuncel harvests sensitive information, including saved passwords from over 25 web browsers, cryptocurrency wallet files from more than 30 applications, and session tokens from platforms like Discord and Steam. It also captures screenshots and compiles a profile of the infected system, uploading the stolen data to an attacker-controlled server. The malware includes a kernel driver that intercepts web traffic, allowing for advertisement injection and search result manipulation.
This campaign has been active for several months, with LastPass vaults remaining unaffected. Users are advised to download applications only from trusted sources. Rapuncel establishes persistence on infected machines by installing itself as a Windows service that starts with the system and terminates activated security products. Removing the kernel driver requires booting into Safe Mode or using external recovery tools, as standard Windows utilities cannot eliminate software operating at that level.
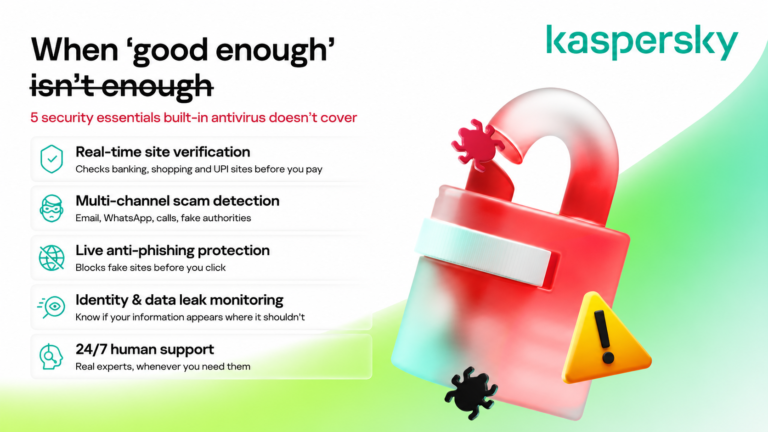
India's internet usage has rapidly evolved, with the Unified Payments Interface (UPI) transforming smartphones into banking hubs and daily tasks being conducted online. Despite this digital shift, many users rely on pre-installed security software, which may not be sufficient against increasing cyber threats. In 2025, nearly one in four internet users in India faced web-based cyber threats, with over 47.5 million threats blocked, averaging about 130,000 daily. Kaspersky's Safe Money feature provides real-time verification of banking and shopping sites, while its anti-phishing capabilities respond to rapidly changing scams. Scammers are using multi-channel approaches, prompting Kaspersky's system to flag suspicious activity across platforms. Credential theft increased by 20% in 2025, with over 225,000 attacks thwarted, and Kaspersky offers identity monitoring to alert users of data leaks. Additionally, Kaspersky Premium provides 24/7 human support for suspicious activities, addressing the limitations of standard antivirus tools in a complex digital threat landscape.