fake

Winsage
October 5, 2026
Microsoft has warned Windows users about a cyber threat that disguises itself as a CAPTCHA test, where cybercriminals use fraudulent verification pages to trick users into executing commands that can install malware. This tactic involves users being directed to a compromised website that presents a fake verification window, prompting them to copy text and execute it in the Windows Run dialog. This method allows attackers to bypass antivirus software by pre-loading malicious scripts disguised as harmless images in the browser's cache. Once activated, the malware collects system information, steals data, and maintains long-term control over the system. Microsoft recommends using robust security software and being aware that no legitimate service will ask users to copy and paste commands into system dialogs.
BetaBeacon
October 4, 2026
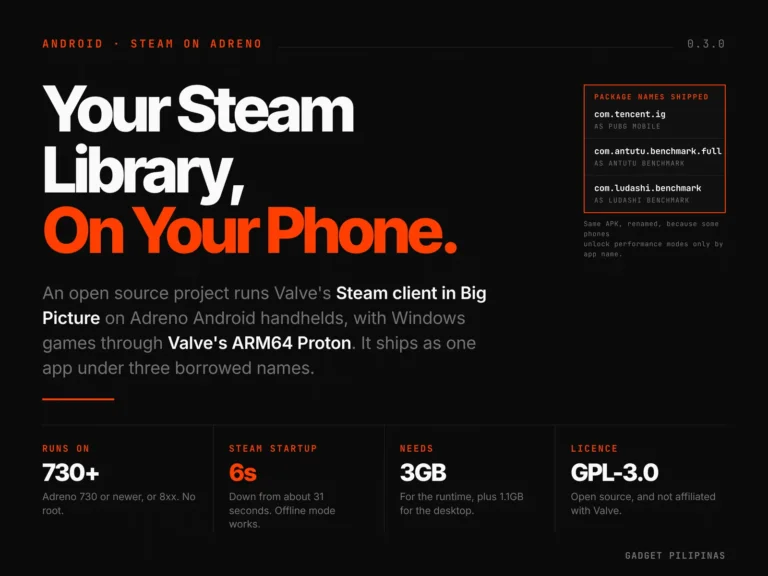
DroidDeck is an open-source project that allows users to run Valve's Steam client in Big Picture mode on Adreno Android devices and play Windows games through Valve's ARM64 Proton.
Winsage
September 29, 2026
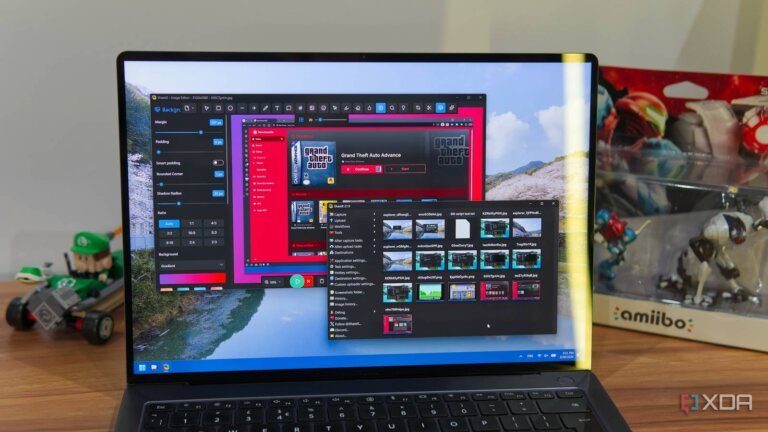
The Snipping Tool in Windows has been modernized in Windows 11 but still has bugs that can disrupt user workflow. ShareX is a free and open-source alternative that excels in screenshot capabilities and offers advanced features, including precise selection tools, real-time editing, video recording, and GIF creation. ShareX supports multiple upload targets, including Imgur and cloud services like OneDrive and Google Drive, and allows users to upload various file types, including text documents to Pastebin. It includes bonus features such as a video converter, image comparison tools, and customization options for hotkeys. However, ShareX may be overwhelming for newcomers seeking basic screenshot functions, for whom the Snipping Tool remains a valid choice.
Tech Optimizer
September 25, 2026
Cybercriminals have developed an infostealer called MacSync, targeting Mac devices by using iCloud calendar events and cloud storage. This malware disguises itself as fake cryptocurrency wallets and pirated software. It begins with a loader that retrieves instructions from calendar entries and deploys malware to exfiltrate sensitive information, including credentials and cryptocurrency wallets. Recent versions have introduced an Objective-C backdoor that mimics Finder. Victims are often tricked into downloading these malicious applications, and effective antivirus solutions can prevent damage. Cybercriminals use tactics like SEO poisoning and phishing to direct victims to fraudulent websites or social media promoting pirated software. In one case, the loader was marketed as a cryptocurrency wallet, and victims encountered a misleading ClickFix error message that prompted them to execute a command in the Terminal.
Winsage
September 24, 2026
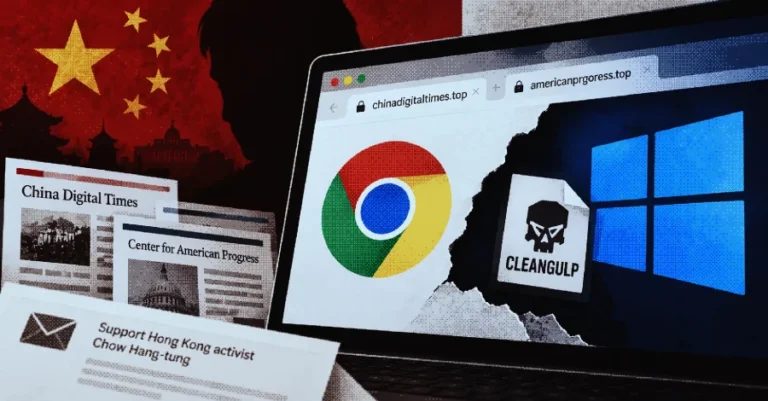
A Chinese threat actor, codenamed UTA0565, has exploited newly disclosed vulnerabilities in Google Chrome (CVE-2026-85046, CVE-2026-87491) and Windows (CVE-2026-85880) through deceptive websites, achieving remote code execution. The attacks were detected on September 3 and 4, 2026, and involved impersonating organizations to mislead victims, particularly targeting Asian government entities with phishing emails related to Hong Kong activist Chow Hang-tung. The phishing messages directed users to fraudulent sites that loaded an HTML element using the BlueMoon exploit kit, which delivered a payload named "chrome_cleanup.exe," associated with the CLEANGULP malware family. This malware allows for command execution, process listing, file uploads and downloads, and uses a hard-coded domain for command-and-control communications. The exploit's widespread use suggests a coordinated effort within the Chinese cyber espionage community, with indications that multiple groups are sharing and weaponizing the exploit.
Search