file access

Winsage
October 12, 2026
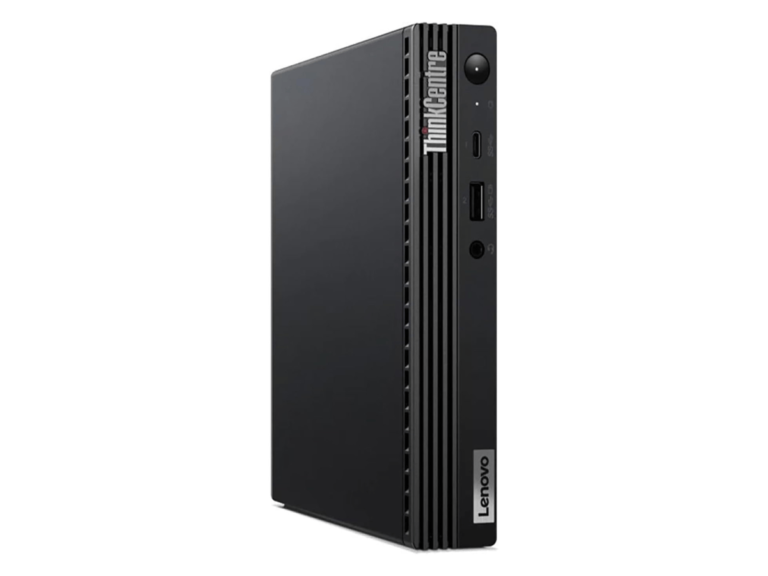
The refurbished Lenovo ThinkCentre M75q Gen 2 mini PC is available for .99, reduced from its original price of .99. It comes pre-installed with Windows 11 Pro, features an AMD Ryzen 5 PRO 5650GE processor with six cores, 16GB of DDR4 RAM (upgradeable to 32GB), and a 256GB NVMe SSD. The compact unit measures 7.2 by 7.1 by 1.4 inches and weighs 2.9 pounds. It supports up to three monitors via HDMI and DisplayPort, includes USB-C and USB 3.2 ports, gigabit Ethernet, Wi-Fi, and Bluetooth 4.2. A wired keyboard and mouse are included, along with a third-party 90-day parts-and-labor warranty. No coupon is needed for this offer.
AppWizard
October 9, 2026
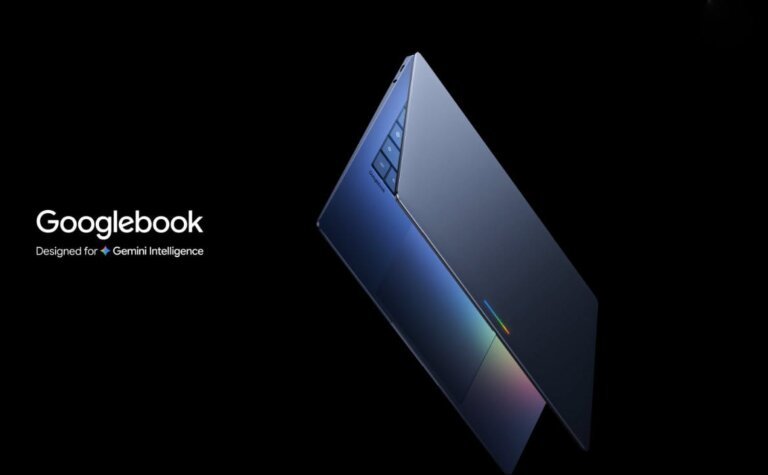
Google has identified a first-time setup timing issue that caused connectivity problems for users pairing their phones with new Googlebook laptops. This issue is not related to hardware malfunctions. A fix is being rolled out via a Google Play Services app update, which began this week, addressing the setup sequence and ensuring the QR code clears correctly for phone recognition. Supported devices running Android 17 can pair successfully, but some users may still experience issues if the update hasn't reached their devices. Samsung Galaxy phones, including the latest models, are not yet compatible, and a fix for these devices is expected in the coming weeks. The update is free and delivered through Google Play Services.
AppWizard
October 6, 2026
Google's new Googlebook cross-device features require a smartphone running Android 17 to access functionalities like phone app streaming, task continuity, and shared file access. Only recent Google Pixel models and Samsung foldable devices with One UI 9 come pre-installed with Android 17, leaving many users with older flagship and mid-range devices unable to utilize these features. New models, such as the POCO F9 series, also launch with Android 16, making them incompatible. Additionally, applications with DRM-protected content or sensitive information will not stream to the laptop, displaying a blank privacy screen instead. The features are included at no extra cost, but their availability depends on the smartphone's Android version.
AppWizard
October 2, 2026
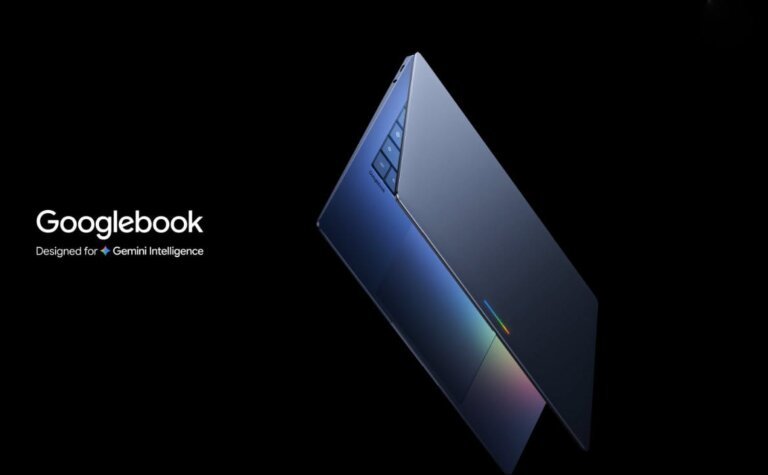
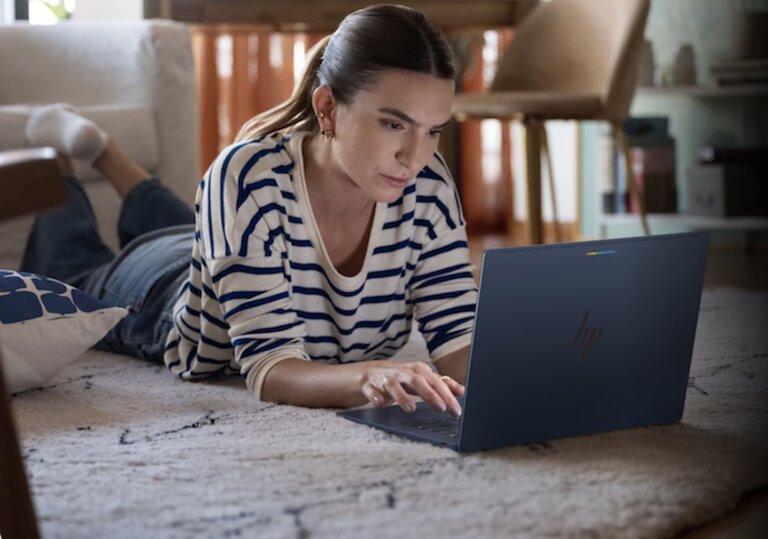
HP has introduced the Googlebook 14, a premium laptop designed to integrate seamlessly with Android phones, featuring phone-file access, app streaming, and a 2.8K OLED touchscreen powered by Snapdragon X Elite hardware. The laptop starts at ,199.99, with Google listing it at ,299 for a configuration with 16GB of RAM and 512GB of storage. It supports Android 17 or newer phones, allowing users to access phone files and applications directly from the laptop. The Googlebook 14 has a slim profile, vapor-chamber cooling, a 5MP infrared camera, and supports up to two UHD external displays. Battery life is claimed to be up to 19 hours, but testing methods vary. The laptop includes AI features like Magic Pointer and Rambler, but some features are limited by region and age. Eligible buyers receive 12 months of Google AI Pro with 5TB of cloud storage, available in select countries.
Tech Optimizer
September 12, 2026
If you hold Microsoft 365 E5, you already have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended. CrowdStrike is suitable for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses without IT staff, VIPRE for budget-conscious organizations, and Expel for tool-agnostic managed detection and response. It is essential to assess your organization's current situation honestly when evaluating endpoint protection options. Antivirus and EDR are now essentially the same agent, and organizations should inquire about update staging processes and review independent tests for protection rates. Coverage for servers and Linux environments is often overlooked but crucial, as Linux servers are prime targets for ransomware. Key recommendations include: - Microsoft Defender for Endpoint for organizations already on Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a well-funded security operations function. - SentinelOne for mid-sized organizations needing autonomous operation. - ESET for organizations with older hardware or virtual desktop infrastructure. - Avast Business for micro and small businesses. - VIPRE for budget-conscious organizations. - Expel for those seeking managed detection across various environments. During deployment, avoid running two real-time agents simultaneously, ensure prevention features are activated, and test on line-of-business applications first. Verify update staging and rollback procedures with vendors, and confirm whether Microsoft licensing covers your needs to avoid unnecessary purchases.
Tech Optimizer
September 10, 2026
If you hold Microsoft 365 E5, you have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly platform. CrowdStrike is suggested for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses, VIPRE for budget-conscious mixed estates, and Expel for tool-agnostic managed detection and response. Antivirus and EDR are now unified under a single agent, and organizations should inquire about update staging processes to avoid issues like those experienced in July 2024 with a major vendor's faulty content update. Independent tests from organizations like AV-Comparatives and AV-TEST are crucial for evaluating protection rates and false positives. Linux servers require attention as they are often targeted by ransomware. When deploying endpoint protection, avoid running two real-time agents simultaneously, activate prevention features promptly, and test deployments on critical applications first. Organizations should confirm their Microsoft licensing covers necessary features and ensure there is a plan for responding to alerts. Common pitfalls include neglecting identity management and failing to test response workflows before incidents occur.
Winsage
September 10, 2026
On September 8, 2026, Microsoft released 966 security updates, the largest Patch Tuesday to date, addressing various vulnerabilities. Among these, 105 were classified as critical, including two zero-day vulnerabilities: CVE-2026-81963 and CVE-2026-85880. Both allow authorized local attackers to escalate privileges to SYSTEM level. CVE-2026-81963 is related to the Windows Update Stack, while CVE-2026-85880 involves a heap-based buffer overflow in the Windows Advanced Local Procedure Call (ALPC). The updates included 438 vulnerabilities related to privilege escalation, 258 concerning remote code execution, and 173 involving information disclosures. Users are advised to prioritize the installation of these updates due to the potential exploitation of the two critical vulnerabilities.
Winsage
September 10, 2026
Microsoft's Patch Tuesday on September 8, 2026, addressed two critical Windows privilege escalation vulnerabilities: CVE-2026-85880 and CVE-2026-81963, both with a CVSS score of 7.8. CVE-2026-85880 is a heap-based buffer overflow in the Windows Advanced Local Procedure Call (ALPC), allowing attackers with low-privilege local access to escalate privileges to SYSTEM. CVE-2026-81963 involves improper link resolution in the Windows Update Stack, enabling similar privilege escalation. Both vulnerabilities require no user interaction and have been actively exploited prior to the patch release. CISA added them to its Known Exploited Vulnerabilities catalog on September 8, 2026, with a remediation deadline of September 22 for U.S. federal agencies. CVE-2026-85880 affects various Windows 10 and Server versions but excludes Windows 11 and Windows Server 2025. CVE-2026-81963 impacts newer Windows platforms, including Windows 11 and Windows Server 2025. Microsoft released security updates for both vulnerabilities on September 8, 2026, and organizations are advised to prioritize these updates. Security teams should monitor for signs of privilege escalation and unusual SYSTEM-level activities related to these vulnerabilities.
Search