file access

Tech Optimizer
September 12, 2026
If you hold Microsoft 365 E5, you already have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended. CrowdStrike is suitable for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses without IT staff, VIPRE for budget-conscious organizations, and Expel for tool-agnostic managed detection and response. It is essential to assess your organization's current situation honestly when evaluating endpoint protection options. Antivirus and EDR are now essentially the same agent, and organizations should inquire about update staging processes and review independent tests for protection rates. Coverage for servers and Linux environments is often overlooked but crucial, as Linux servers are prime targets for ransomware. Key recommendations include: - Microsoft Defender for Endpoint for organizations already on Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a well-funded security operations function. - SentinelOne for mid-sized organizations needing autonomous operation. - ESET for organizations with older hardware or virtual desktop infrastructure. - Avast Business for micro and small businesses. - VIPRE for budget-conscious organizations. - Expel for those seeking managed detection across various environments. During deployment, avoid running two real-time agents simultaneously, ensure prevention features are activated, and test on line-of-business applications first. Verify update staging and rollback procedures with vendors, and confirm whether Microsoft licensing covers your needs to avoid unnecessary purchases.
Tech Optimizer
September 10, 2026
If you hold Microsoft 365 E5, you have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended for its user-friendly platform. CrowdStrike is suggested for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses, VIPRE for budget-conscious mixed estates, and Expel for tool-agnostic managed detection and response. Antivirus and EDR are now unified under a single agent, and organizations should inquire about update staging processes to avoid issues like those experienced in July 2024 with a major vendor's faulty content update. Independent tests from organizations like AV-Comparatives and AV-TEST are crucial for evaluating protection rates and false positives. Linux servers require attention as they are often targeted by ransomware. When deploying endpoint protection, avoid running two real-time agents simultaneously, activate prevention features promptly, and test deployments on critical applications first. Organizations should confirm their Microsoft licensing covers necessary features and ensure there is a plan for responding to alerts. Common pitfalls include neglecting identity management and failing to test response workflows before incidents occur.
Winsage
September 10, 2026
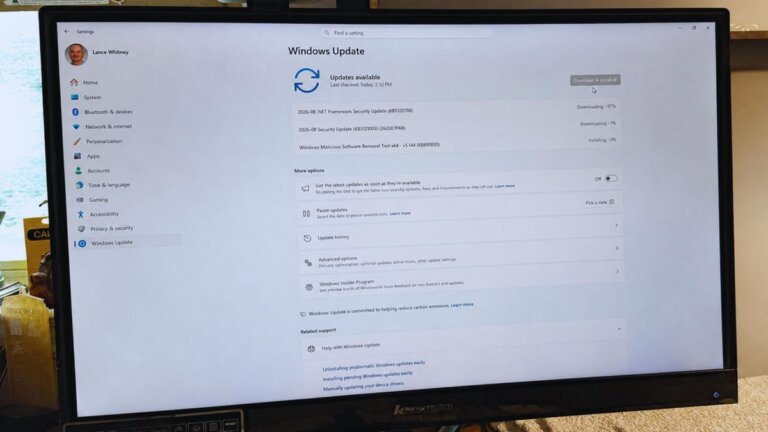
On September 8, 2026, Microsoft released 966 security updates, the largest Patch Tuesday to date, addressing various vulnerabilities. Among these, 105 were classified as critical, including two zero-day vulnerabilities: CVE-2026-81963 and CVE-2026-85880. Both allow authorized local attackers to escalate privileges to SYSTEM level. CVE-2026-81963 is related to the Windows Update Stack, while CVE-2026-85880 involves a heap-based buffer overflow in the Windows Advanced Local Procedure Call (ALPC). The updates included 438 vulnerabilities related to privilege escalation, 258 concerning remote code execution, and 173 involving information disclosures. Users are advised to prioritize the installation of these updates due to the potential exploitation of the two critical vulnerabilities.
Winsage
September 10, 2026
Microsoft's Patch Tuesday on September 8, 2026, addressed two critical Windows privilege escalation vulnerabilities: CVE-2026-85880 and CVE-2026-81963, both with a CVSS score of 7.8. CVE-2026-85880 is a heap-based buffer overflow in the Windows Advanced Local Procedure Call (ALPC), allowing attackers with low-privilege local access to escalate privileges to SYSTEM. CVE-2026-81963 involves improper link resolution in the Windows Update Stack, enabling similar privilege escalation. Both vulnerabilities require no user interaction and have been actively exploited prior to the patch release. CISA added them to its Known Exploited Vulnerabilities catalog on September 8, 2026, with a remediation deadline of September 22 for U.S. federal agencies. CVE-2026-85880 affects various Windows 10 and Server versions but excludes Windows 11 and Windows Server 2025. CVE-2026-81963 impacts newer Windows platforms, including Windows 11 and Windows Server 2025. Microsoft released security updates for both vulnerabilities on September 8, 2026, and organizations are advised to prioritize these updates. Security teams should monitor for signs of privilege escalation and unusual SYSTEM-level activities related to these vulnerabilities.
Winsage
September 9, 2026
Microsoft's September 2026 security update revealed 973 vulnerabilities, with 113 classified as critical. Two actively exploited vulnerabilities are CVE-2026-81963 (Windows Update Stack, elevation of privilege, CVSS 7.8) and CVE-2026-85880 (Windows ALPC, elevation of privilege, CVSS 7.8). Among the 113 critical vulnerabilities, 82 are remote code execution (RCE) vulnerabilities. Notable vulnerabilities include: - CVE-2026-69676: RCE in Windows Kerberos, CVSS 8.8, authentication bypass. - CVE-2026-69852: RCE in Windows RRAS, CVSS 7.5, heap-based buffer overflow. - CVE-2026-72957: RCE in Windows Deployment Services, CVSS 7.8. - CVE-2026-69854: Elevation of privilege in Spring Cloud Azure, CVSS 9.0, improper authentication. - CVE-2026-83501: Information disclosure in Windows VBS, CVSS 5.5. - CVE-2026-69730: RCE in Windows DNS Server, CVSS 9.8. Less likely to be exploited vulnerabilities include: - CVE-2026-69845: RCE in Windows DHCP Server, CVSS 9.8, heap-based buffer overflow. - CVE-2026-65772: Vulnerability in Microsoft Dynamics 365 On-Premises, CVSS 8.8, deserialization of untrusted data. - CVE-2026-66302: RCE in Skype for Business, CVSS 9.8. Additional critical vulnerabilities include: - CVE-2026-62916: Elevation of privilege in Microsoft Entra ID, CVSS 9.1. - CVE-2026-83941: Elevation of privilege in Entra ID, CVSS 9.9. - CVE-2026-80098: Vulnerability in Copilot Studio, CVSS 9.3, improper verification of cryptographic signatures. Talos is releasing a new Snort ruleset to detect attempts to exploit these vulnerabilities, with specific SIDs for Snort 2 and Snort 3 rule coverage.
Winsage
August 30, 2026
Yt-dlp is a free tool that allows users to download content from over 1,700 websites, including YouTube, Twitter, Facebook, and Instagram. It is available for various platforms and can be installed on Windows by downloading the .exe package. Users can download videos by entering the command yt-dlp in the terminal, and they can specify download locations, formats, and resolutions. Microsoft PowerToys is a suite of utilities designed to enhance the Windows experience by adding features not included in the standard installation. It includes tools for pinning windows, creating custom layouts, automating theme changes, quick file access, bulk renaming, and extracting text from images and PDFs. KSnip is a screenshot tool available on Linux, Windows, and macOS, which allows users to capture screenshots quickly with customizable hotkeys. It includes built-in editing tools for annotations and can automatically upload screenshots to an FTP server or Imgur.
AppWizard
August 28, 2026
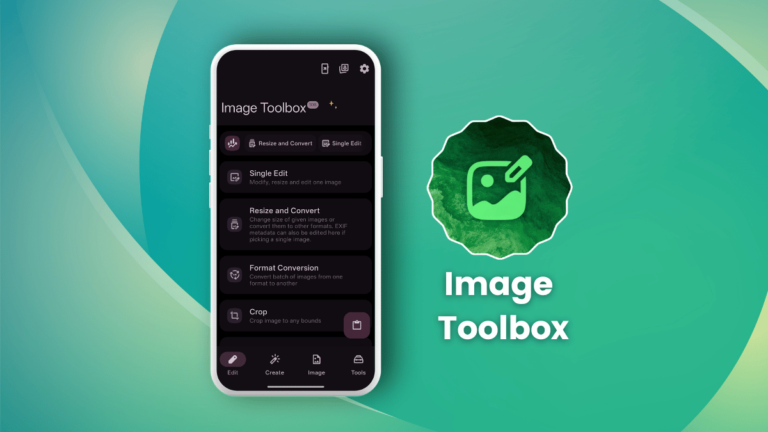
Image Toolbox is an Android app developed by Malik Mukhametzyanov, designed to assist content creators by consolidating essential functions such as resizing, format conversion, watermarking, and platform-specific exports into a single interface. It features batch processing capabilities, 61 built-in export presets for platforms like Instagram, X, and YouTube, and background removal options using various AI models. The app is free, ad-free, and released under the Apache License 2.0. Users can customize the app's color scheme, and it includes a "Usage Statistics" page that tracks app usage while ensuring user privacy. Image Toolbox is available on F-Droid and the Play Store, with both versions being identical except for the inclusion of Google-related trackers in the Play Store version. There is no paid plan, and donations are welcomed. APK files can also be downloaded from the project's GitHub repository.
Winsage
August 12, 2026
Microsoft's August Patch Tuesday update addressed 421 vulnerabilities across various products, including multiple versions of Windows (11 25H2/24H2, 11 23H2, and 10). A critical zero-day flaw, the "Windows Ancillary Function Driver for WinSock Elevation of Privilege Vulnerability," allows attackers with lower-level access to gain system privileges without user interaction. Additionally, the update addresses two other zero-day flaws, including the "Windows User Profile Service Elevation of Privilege Vulnerability," which has not yet been exploited but was publicly disclosed. The update is mandatory and should automatically install on supported PCs, with users encouraged to verify its application. The update also includes minor improvements to Windows features, such as enhancements to File Explorer, Windows Hello, Voice Access, and touchpad controls.
Tech Optimizer
July 22, 2026
The user experienced a slow computer with prolonged startup times and storage shortages despite manual cleanup efforts, including emptying the Recycle Bin and using Windows Disk Cleanup. A deeper system scan revealed hidden junk files such as temporary files, browser cache, and outdated logs. The user then utilized Advanced SystemCare 19 Free, which effectively identified and removed 3GB of junk files, resulting in improved startup speed, program launch times, and overall performance. Advanced SystemCare also includes features like a registry cleaner, large file finder, disk cleaner, and app/extension cleaner, and it serves as a comprehensive system optimization suite with tools for enhancing boot time and protecting privacy. The software does not delete files automatically and should be used alongside antivirus software for complete protection.
Search