file uploads

AppWizard
October 10, 2026
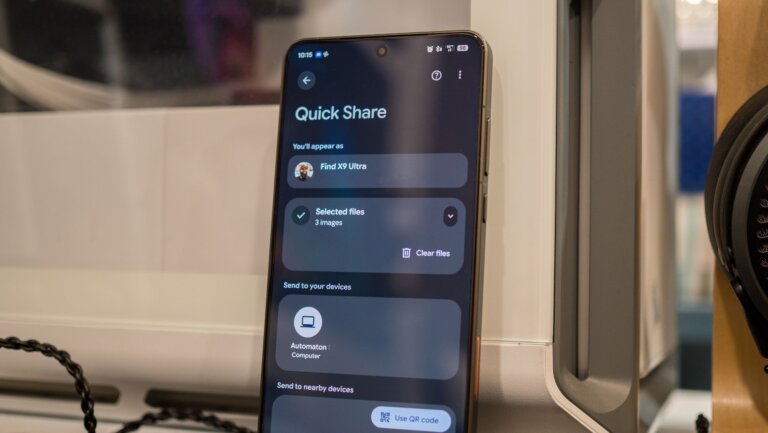
Google has updated the search bar on the home screen of its Android app in version 17.65.17, introducing a new "plus" button for easier access to file uploads and AI tools. The redesigned search bar is slimmer with a white background, a border, and a shadow effect. The plus icon on the left allows users to attach images or files, create visuals with Nano Banana, or switch models in AI Mode, while the microphone and Google Lens icons remain on the right. The two shortcut buttons beneath the search bar now have text labels: "Create" for Nano Banana and "Talk" for Search Live, improving usability. The update is being rolled out broadly, but no specific timeline has been provided for when users in the UAE will receive it. Users need to update the app to version 17.65.17 to access the new search bar, and the plus button does not add new features but provides quicker access to existing ones.
Winsage
September 24, 2026
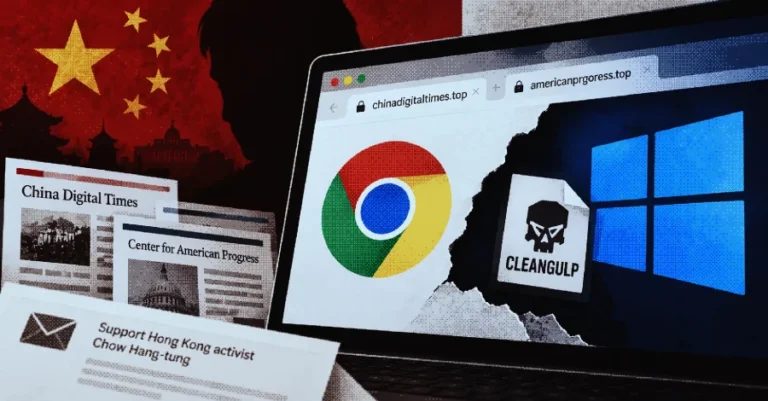
A Chinese threat actor, codenamed UTA0565, has exploited newly disclosed vulnerabilities in Google Chrome (CVE-2026-85046, CVE-2026-87491) and Windows (CVE-2026-85880) through deceptive websites, achieving remote code execution. The attacks were detected on September 3 and 4, 2026, and involved impersonating organizations to mislead victims, particularly targeting Asian government entities with phishing emails related to Hong Kong activist Chow Hang-tung. The phishing messages directed users to fraudulent sites that loaded an HTML element using the BlueMoon exploit kit, which delivered a payload named "chrome_cleanup.exe," associated with the CLEANGULP malware family. This malware allows for command execution, process listing, file uploads and downloads, and uses a hard-coded domain for command-and-control communications. The exploit's widespread use suggests a coordinated effort within the Chinese cyber espionage community, with indications that multiple groups are sharing and weaponizing the exploit.
AppWizard
September 14, 2026
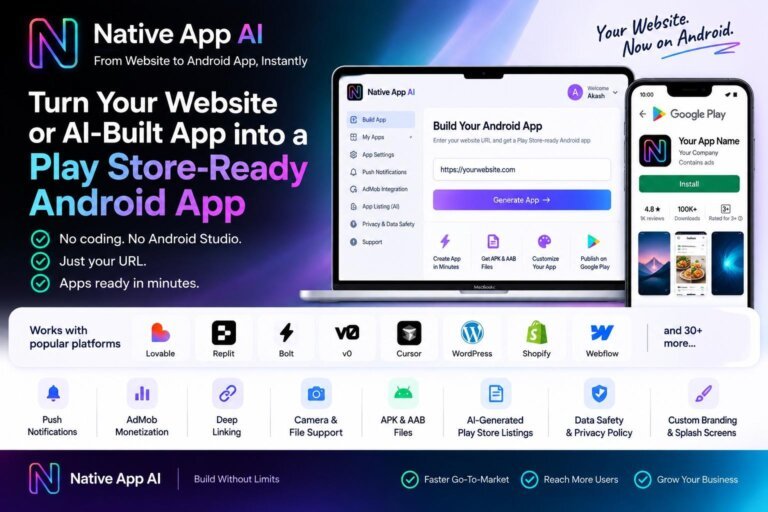
Native App AI simplifies the process of converting websites or AI-generated web apps into Android applications ready for the Play Store without needing to rebuild from scratch. It allows users to input a website URL, customize the app's features, and generate APK and AAB files for testing and publishing. The platform supports various features such as push notifications, AdMob monetization, deep linking, and custom branding. It also assists in preparing necessary information for Google Play, ensuring compliance with policies and technical requirements. This service is beneficial for SaaS companies, startups, e-commerce ventures, and creators who have existing web products.
Tech Optimizer
July 28, 2026
Malware can threaten Linux systems, which are often mistakenly believed to be immune to viruses. It can be introduced through email attachments, infected files, or compromised plugins, especially when Linux servers interact with Windows clients or handle internet uploads. ClamAV is an open-source antivirus engine maintained by Cisco Talos, designed for scanning mail traffic and file uploads. As of mid-2026, the stable release is ClamAV 1.5.x, with version 1.5.2 being the latest patch. To deploy ClamAV, users need root or sudo access on a compatible Linux machine, at least 2 vCPUs and 2GB of RAM, 5GB of free disk space, and outbound HTTPS access to ClamAV’s signature mirrors. The installation process involves several steps, including configuring freshclam for automatic updates, validating detection with the EICAR test file, and setting up cron jobs for regular scans. ClamAV can also be integrated with mail servers and a SIEM for enhanced security. Common pitfalls in deployment include skipping the initial freshclam run and using clamscan instead of clamdscan for repeated scans. ClamAV is free for commercial use and can also scan Windows systems, although it does not replace comprehensive endpoint protection solutions.
Winsage
June 16, 2026
Cybersecurity researchers have identified two new Windows variants of the SprySOCKS backdoor, named WINDRV and WINPLUS, which were previously thought to be exclusive to Linux systems. Both variants feature hard-coded command-and-control configurations and can communicate via TCP, UDP, and WebSocket protocols. They support over 30 commands for operations such as system information collection and file management. WINDRV employs kernel drivers for stealth, obscuring network connections and allowing TCP traffic diversion. SprySOCKS was first documented by Trend Micro in September 2023, linked to the Chinese state-sponsored threat actor Earth Lusca, also known as FishMonger. The Windows variants belong to version 1.8 of SprySOCKS and utilize a kernel driver named RawWNPF for enhanced stealth. The attack chain begins with an initial access method that drops a batch script, leading to the installation of the backdoor. Evidence suggests these variants may have been used in attacks against government organizations in Honduras, Taiwan, Thailand, and Pakistan between 2023 and 2024. The WINPLUS variant was first detected in July 2024 in Pakistan. There are indications of a potential UEFI bootkit involvement exploiting CVE-2023-24932, a vulnerability in the Windows Boot Manager.
Search