financial applications

AppWizard
September 19, 2026
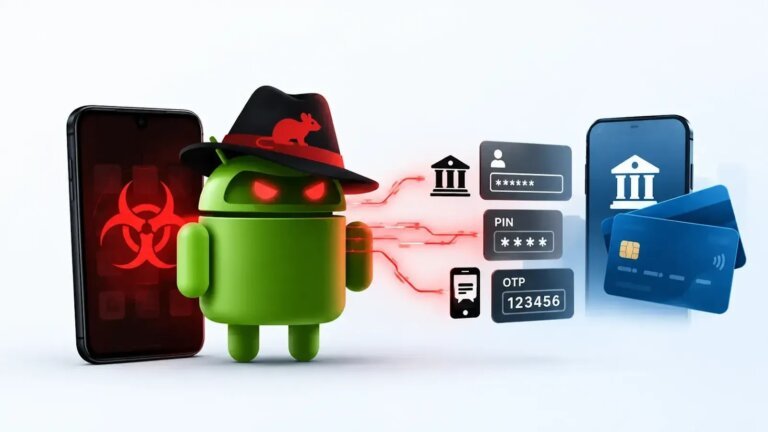
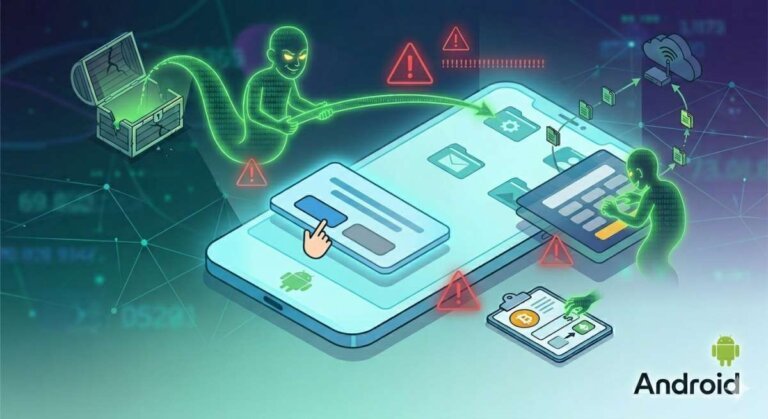
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
BetaBeacon
August 21, 2026
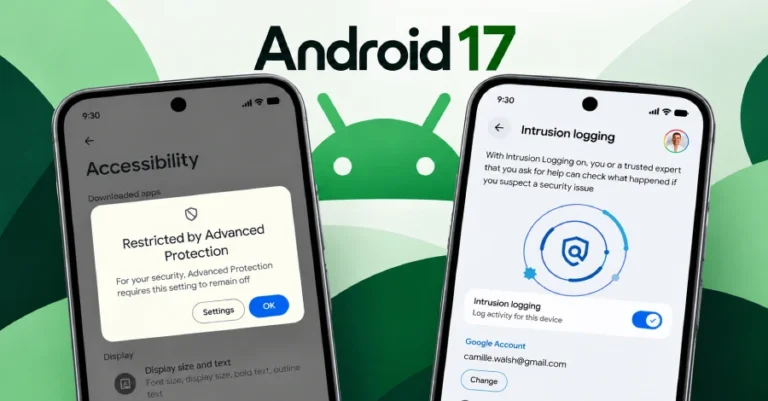
Android is used across a wide range of devices, encouraging developers to create applications for various use cases. Android users can find apps for messaging, video editing, photography, productivity, music, navigation, fitness, education, file management, streaming, social networking, and mobile gaming. Modern phones can run games with console-like graphics, multiplayer systems, cloud synchronization, controller support, and large open worlds. Users can download APK files outside Google Play for various reasons, such as version availability and geographic restrictions. A reliable APK download website should provide detailed information about the application before installation. Users should verify the application name, package name, version, Android compatibility, and permissions before installing an APK. XAPK files package the APK with additional resources required by larger applications or games. Android security is becoming stricter, with more protections around application permissions, background activity, storage access, outdated applications, and unknown installation sources. Access to previous app versions can be useful in case updates introduce issues. Android applications are becoming more powerful, performing tasks that previously required computers, thanks to hardware improvements such as powerful processors, large memory, high-refresh-rate displays, fast storage, and capable GPUs.
AppWizard
June 12, 2026
Google will soon notify Android users when an app they installed has lost developer support. Currently, users only receive alerts from Play Protect for significant security threats or potentially harmful apps. The only way to discover if an app has been delisted is through external sources or by trying to install it on a new device. Recent findings in the Play Store indicate that Google is preparing to inform users when apps have been removed from the Play Store and will no longer receive updates. Abandoned apps pose significant security risks, as they may contain vulnerabilities that can be exploited by malicious actors. Google's new notifications aim to encourage users to uninstall unsupported apps to protect their personal data.
Tech Optimizer
May 22, 2026
Financial service institutions are increasingly exploring AI applications to alleviate operational burdens and gain a competitive edge, but face challenges with legacy data infrastructures that may not meet modern demands. The need for continuous availability and compliance is critical, as even brief downtime can have catastrophic consequences. Aging databases struggle with high-volume transactions and real-time analytics, prompting a focus on predictive maintenance and infrastructure automation. Microsoft Azure's PostgreSQL managed services, including Azure Database for PostgreSQL, address these challenges by providing flexible performance scaling and ensuring high availability. The service can trigger automatic failover within 60 to 120 seconds during outages, guaranteeing up to a 99.99% availability SLA. It supports read replicas for offloading analytics without impacting primary database performance and offers layered security controls, including encryption at rest and network isolation. Azure Database for PostgreSQL simplifies compliance with standards such as PCI DSS and SOC by enabling centralized identity and access management through Microsoft Entra ID authentication. It integrates seamlessly with the Microsoft ecosystem, allowing organizations to connect data to analytics and AI services without complex ETL processes. BNY Mellon successfully modernized its data platform by migrating to Azure Database for PostgreSQL in nine months, achieving improved resilience and allowing engineering teams to focus on innovation. The platform supports high availability, backup capabilities, and extensibility, empowering financial institutions to remain innovative in the era of AI.
Search