financial fraud

AppWizard
September 14, 2026
Malicious Android applications are being promoted through social media advertisements, particularly on platforms like Instagram and Facebook, posing significant risks to users. The Indian Cyber Crime Coordination Centre (I4C) has warned about deceptive apps advertised under names such as Night Play, Reloop, Kyss, Vimo, Rivo, Nezo, and Vixa, which often redirect users to pornographic websites to download APK files. These applications can exploit sensitive device permissions, leading to malware infections, unauthorized financial transactions, and various forms of cyber fraud. Users may be tricked into granting accessibility permissions that allow the malware to operate in the background and potentially install a VPN, rerouting internet traffic through servers controlled by attackers. Cybersecurity experts advise users to verify the legitimacy of applications before installation and to be cautious of permissions requested by unknown apps.
AppWizard
September 10, 2026
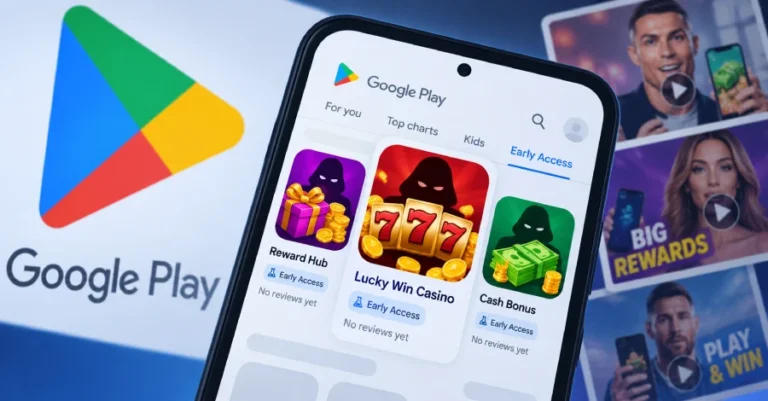
Bad actors are exploiting Google Play's Early Access program to distribute misleading applications that promise money, rewards, and casino winnings. This program allows developers to gather user feedback on unreleased apps but lacks public reviews or star ratings, enabling malicious actors to launch numerous fraudulent applications without immediate scrutiny. An example is the app "Vice Streets: Open World," which mimics Grand Theft Auto, has over 1 million downloads, and recently disappeared from the store without reviews or ratings. These deceptive apps are often promoted on social media with misleading advertisements and promise cash rewards, but users face obstacles when trying to withdraw their earnings. The primary goal of these apps is to generate revenue through excessive advertisements while circumventing regulatory requirements for legitimate gambling apps. Additionally, various malware families targeting Android devices have emerged, including Hagaseca, Mantax Otax, StreamRat, and GoldFactory's use of the Gigabud banking trojan, highlighting ongoing security threats in the digital landscape.
AppWizard
September 3, 2026
The National Cybercrime Threat Analytics Unit (NCTAU) has reported a rise in financial fraud linked to deceptive Android applications that pose as pornography apps. These apps are advertised on social media platforms like Facebook and Instagram under names such as ‘Night Play’, ‘Reloop’, ‘Kyss’, ‘Vimo’, ‘Rivo’, ‘Nexo’, and ‘Vixa’. Users who click on these ads are redirected to websites promising adult content, where they are encouraged to download APK files. Once installed, these apps often request sensitive permissions, particularly Accessibility access, which can allow malware to take control of the device and facilitate financial fraud. Some malicious apps may also install a VPN, rerouting internet traffic through servers controlled by attackers and exposing sensitive data. The malware is primarily promoted through ads linked to pornographic content, redirecting users to phishing websites that prompt APK downloads from non-Google Play sources, often using the “.live” domain extension. After installation, the initial app may download a second malicious package disguised as an update, exploiting the permissions granted to the original app.
AppWizard
August 31, 2026
India's cybercrime authorities have warned about the misuse of dating and adult-themed advertisements on social media platforms like Instagram and Facebook, which are being exploited by criminals to distribute malicious Android applications. These ads redirect users to external websites where they are prompted to download APK files, bypassing security measures of trusted app stores. The Indian Cybercrime Coordination Centre (I4C) has identified several malicious applications, including Night Play, Reloop, Kyss, Vimo, Rivo, Nexo, and Vixa, and cautions against installing unfamiliar applications promoted through unsolicited ads. These apps may request sensitive permissions, such as access to SMS messages, contacts, photos, device storage, and Accessibility Services, which can allow fraudsters to access valuable information. Compromised devices can lead to financial fraud by intercepting OTPs and other verification details. The I4C recommends using trusted app stores, keeping Google Play Protect active, reviewing app permissions, and being cautious with social media ads. If a suspicious app is installed, users should restart their phone in Safe Mode to uninstall it, disable its permissions if necessary, and consider a factory reset if removal fails. Users who suspect fraud are encouraged to report incidents promptly.
AppWizard
August 23, 2026
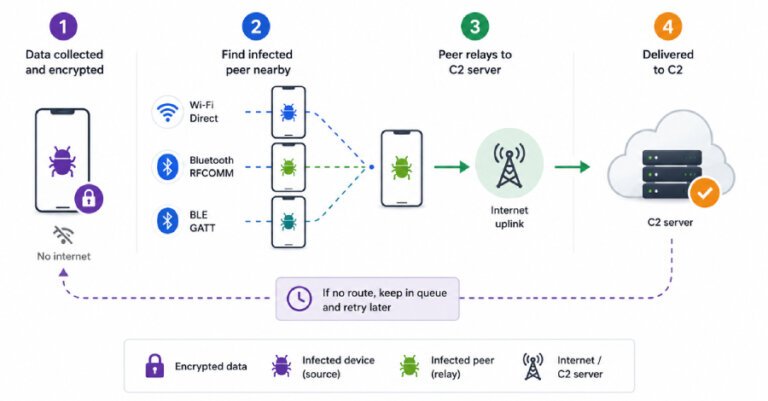
A new Android malware threat, codenamed Manic, poses significant risks to Ukrainian banks, government services, and messaging applications, with a reach extending to Russian and European financial institutions, global fintech platforms, cryptocurrency services, and military communication channels. Manic combines Android banking malware and mobile spyware, targeting sensitive applications and enabling comprehensive device takeover. It features a novel Wi-Fi mesh technique for data relay through compromised devices and utilizes phishing sites and dropper apps. The malware originated in February 2026, with initial development leading to its first deployment by late May. It monitors 169 package IDs related to banks, payment services, and messaging applications, primarily affecting Ukrainian targets but also impacting applications in Russia and Europe. Manic can infiltrate commercial and military messaging apps, track locations, monitor notifications, and collect files. It exploits Android's accessibility services to capture sensitive data and employs a store-and-forward relay mechanism for data exfiltration through nearby compromised devices. Google has stated that no apps containing this malware are found on Google Play, and Android users are protected by Google Play Protect.
Tech Optimizer
July 29, 2026
A study by Kaspersky surveyed 7,200 Gen Z individuals across 18 countries and found that only 27% use mobile antivirus software, while 28% regularly back up their phone data. Many have experienced cyberattacks, with 17% reporting hacked social media accounts and 12% losing access to gaming accounts. The study highlights that compromised smartphones can expose sensitive personal information, increasing the risk of identity theft and financial fraud. Kaspersky has introduced an interactive online game, Case 404, to educate Gen Z on recognizing scams and phishing attempts.
Tech Optimizer
July 1, 2026
Antivirus software has evolved from focusing solely on detecting and eliminating computer viruses to providing comprehensive digital security solutions. The modern threat landscape includes advanced persistent threats, ransomware, phishing schemes, fraud apps, and AI-enabled cyber threats, necessitating a broader approach to cybersecurity. Current digital security systems must detect behavioral anomalies, protect user identities, monitor network activity, identify scam links, and provide multi-layered protection across various platforms. Contemporary antivirus solutions now incorporate AI-based threat detection, cloud intelligence, web protection, email security, identity protection, and ransomware monitoring, reflecting a shift from reactive measures to proactive prevention. Users are now active holders of digital identities, and antivirus software is expected to safeguard their entire digital lives.
Search