firmware update

AppWizard
September 13, 2026
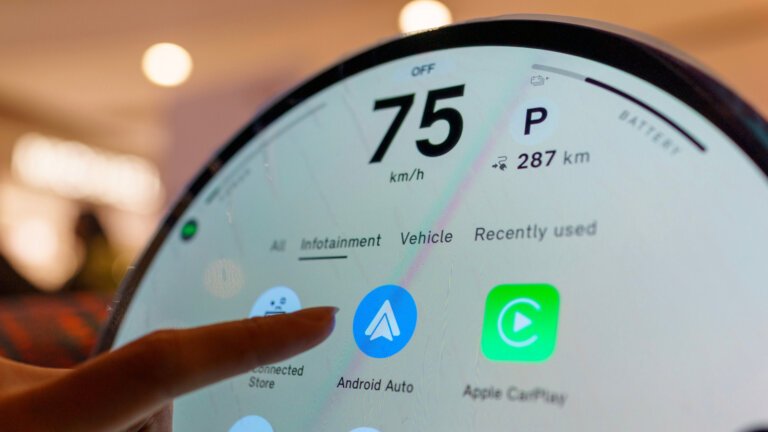
When troubleshooting Android Auto connectivity issues, it's important to consider both the smartphone and the car's infotainment system, as the latter also runs on software that may need updating. Google recommends restarting the infotainment system and checking for firmware updates, especially for aftermarket units. Automakers are releasing updates to improve Android Auto performance, such as Hyundai's February 2026 update for ccNC-equipped vehicles in Europe, which enhanced wireless connectivity and reconnection capabilities. The method for installing updates varies by manufacturer, with some allowing direct downloads via Wi-Fi and others requiring a USB drive or dealer assistance. A firmware update may not resolve all Android Auto issues, particularly if problems arise after a phone or Android Auto update. It's advisable to check Google's Known Issues page for specific models before updating the car's software. Compatibility should be verified, and Android Auto must be enabled in the infotainment system. Updating the car's software is a troubleshooting step, not a guaranteed fix, and firmware updates cannot enable Android Auto on unsupported hardware.
AppWizard
September 13, 2026
When troubleshooting Android Auto issues, it's important to consider both the smartphone and the car's infotainment system. Users should check for firmware updates for their vehicle, as automakers are increasingly releasing updates to improve Android Auto performance. For example, Hyundai's February 2026 update enhanced wireless connectivity for Android Auto and Apple CarPlay. The update process varies by manufacturer, with some systems allowing direct downloads via Wi-Fi, while others may require a USB drive or dealer assistance. A firmware update is not a guaranteed fix for all Android Auto problems, and users should consult Google's Known Issues page for specific device-related problems before making changes to the car's software. Additionally, firmware updates cannot enable Android Auto on hardware that was not designed to support it.
Winsage
September 10, 2026
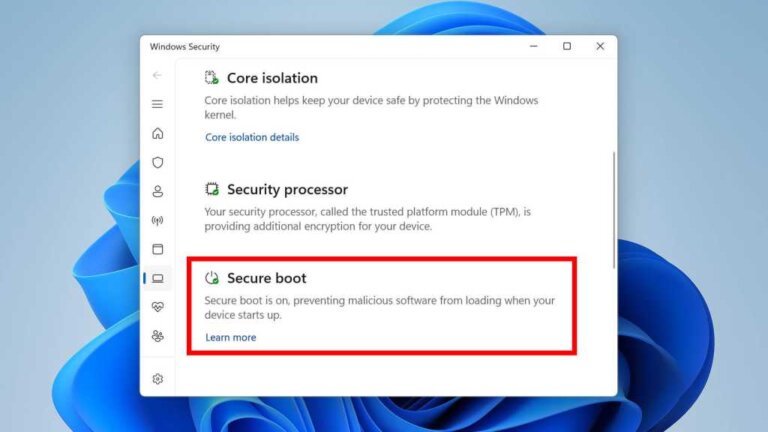
Microsoft is continuing the rollout of Secure Boot certificate updates, with the next significant deadline on October 19, 2026, when the Microsoft Windows Production PCA 2011 certificate expires. The September 2026 Patch Tuesday update has expanded eligibility for Secure Boot certificates to more PCs classified as “high confidence.” Users may need to reboot their PCs to install these updates, and some may require firmware updates beforehand. Microsoft has confirmed that the update process will persist beyond established deadlines, and older certificates are expiring in stages, with the first two deadlines having already passed. Users should ensure they have the latest updates installed and check their Secure Boot status in Windows Security. Microsoft has assured that PCs without the newer certificates will continue to boot normally and receive standard updates while the rollout continues.
AppWizard
August 19, 2026
Navitel has released a software update to fix an aspect ratio issue affecting users of Android Auto, which was first reported in July. The problem was traced to the Navitel head unit software, not the Android Auto app, and impacted multiple head unit models. Users experienced distorted images and text, despite troubleshooting efforts. The update requires manual installation via a microSD card, as it is not available over-the-air. After the update, users can reconnect their Android phones, and Android Auto should function correctly. The latest version of Android Auto, 17.4, is available on the Google Play Store, with a new build expected by the end of the month and a major update planned for the next quarter.
Winsage
July 29, 2026
Microsoft's July Intune update includes enhancements for IT administrators, such as real-time monitoring of Windows device sync progress, custom compliance settings for macOS, and improved firmware update management for Samsung devices. The Intune admin center now allows real-time monitoring of sync progress for Windows devices, enabling simultaneous updates across various management aspects. Custom compliance settings for macOS enable organizations to define specific compliance requirements beyond Apple's standard checks, allowing for a unified compliance management experience across Windows, Linux, and macOS. The update also enhances Samsung Galaxy firmware management through Samsung Knox E-FOTA, allowing administrators to control firmware version deployment and update schedules. Additionally, the update clarifies that newer Windows Autopilot methods allow provisioning of Windows 11 devices without prior registration.
Winsage
July 18, 2026
Microsoft held its OEM Secure Boot Office Hours event on July 15, where engineers collaborated with OEM representatives from companies like Acer, Asus, Cisco, Dell, and HP. IT administrators were able to ask live questions about the Secure Boot 2023 rollout. The discussion thread became a detailed technical record, especially following the expiration of the first certificates three weeks prior. Concerns raised by IT admins included BitLocker recovery loops, stuck confidence ratings, and unhelpful Intune error codes. Key facts include: - Devices offline for long periods will still receive the 2023 certificates upon reconnecting to Windows Update. - Devices with existing 2023 certificates in firmware will switch to the new boot manager after the latest Windows patches are installed. - A new script, Detect-SecureBootCertUpdateStatus.ps1, is available in Windows for checking certificate status. - BIOS updates may reset a device’s confidence rating to unrated, which is normal and does not indicate certificate failure. - Admins should edit the AvailableUpdates registry key, not the AvailableUpdatesPolicy, which is managed by Intune and Group Policy. - A licensing bug affecting AvailableUpdatesPolicy on devices upgraded from Pro to Enterprise was resolved by Microsoft in 2026. - BitLocker recovery is not typically linked to the certificate update process but may relate to firmware or PCR issues. - Dell and HP provided guidance on which BIOS versions include the 2023 certificates for their newer models. - Older HP EliteBook 840 G5 units require a manual update package for the new certificates. - Eligible devices can still receive the 2023 certificates in the future, and Surface devices released from 2024 onward come pre-equipped with them. - Microsoft confirmed that devices running 2011 certificates will not lose the ability to receive the 2023 chain. - The Microsoft Corporation KEK CA 2011 and Microsoft UEFI CA 2011 certificates have expired, with the Microsoft Windows Production PCA 2011 set to expire on October 19, 2026.
Winsage
July 14, 2026
Microsoft has acknowledged that several older Secure Boot certificates have expired, necessitating updates for Windows 10 and 11 users. A temporary halt in the issuance of new Secure Boot certificates affects specific PCs, particularly various HP models. Most PCs will receive updates automatically through Windows Update, but some may require a firmware update from the manufacturer. Users may see messages indicating that Secure Boot certificate updates are paused or blocked due to known issues or hardware/firmware limitations. Until manufacturers like HP release necessary firmware updates, users cannot update their Secure Boot certificates. Although the immediate risk from expired certificates is low, it is expected to increase over time. Devices with un-updated Secure Boot certificates will continue to function normally, but they will not receive new security updates, making them vulnerable to emerging threats. Essential features that rely on updated security measures may cease to function correctly as new security challenges arise.
Winsage
July 10, 2026
Microsoft has acknowledged that some Windows 11 PCs are facing issues with Secure Boot certificate updates, which may fail to install or be blocked. The company is working with PC manufacturers to develop a patch, while users may need to take proactive measures if their certificates are obstructed. Microsoft has temporarily halted the rollout of Secure Boot for certain devices due to complications, and affected users will receive detailed error messages in the Windows Security app regarding their Secure Boot certificates. Secure Boot certificates issued in 2011 have expired, and Microsoft is replacing them with new certificates issued in 2023. Most modern hardware is already utilizing the new certificates, but some devices may have disabled Secure Boot or faulty firmware. Users can check their Secure Boot status in the Windows Security app. HP has confirmed that Secure Boot updates are being blocked on some of its PCs due to a BitLocker issue, which prevents the installation of new certificates. Microsoft has paused Secure Boot certificate updates for devices affected by known issues while collaborating with manufacturers to identify specific devices or firmware complications. A firmware update will be necessary for affected devices, but it is not yet available. The majority of PCs have received the Secure Boot certificates via Windows Update, but compatibility issues may prevent some devices from receiving the update. Older devices or those not among the OEM’s top-selling models may not receive updates if the UEFI firmware is unsupported. Secure Boot is a security feature required for Windows 11, preventing unauthorized software from executing at boot. While an expired Secure Boot certificate does not stop a PC from functioning, it may limit long-term security protection. Microsoft advises users not to disable Secure Boot, as it would compromise security further.
Search