firmware

AppWizard
October 20, 2026
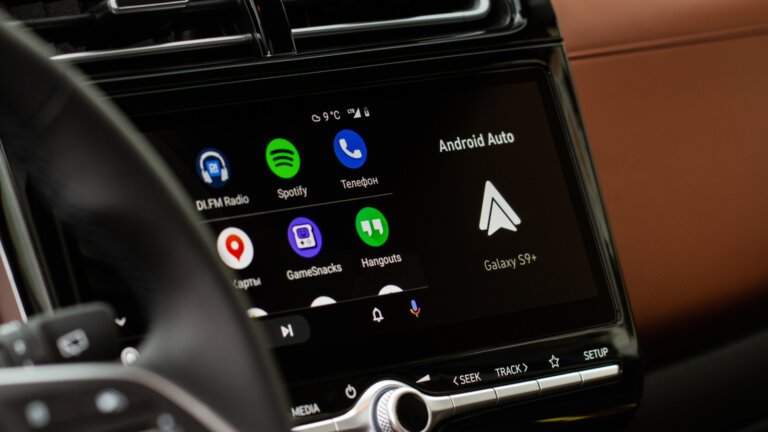
Many drivers experience unexpected audio playback when starting their vehicle with Android Auto, as the last listened-to content resumes at the previous volume. To stop this autoplay, users can disable the "Start music automatically" option in Android Auto's settings under Settings > Connected devices > Android Auto. If this does not resolve the issue, it may be related to Bluetooth interactions. Users are advised to remove their phone from the car's Bluetooth memory and reconnect via USB. Additionally, Bluetooth devices paired with the phone can influence autoplay behavior, and users should test different devices to identify the cause. Keeping Spotify and device software updated may help, but a universal solution is not guaranteed. If necessary, users can remove Spotify from Android Auto, though this will limit access to the app through the car's display.
AppWizard
October 18, 2026
A developer named Gathin has created tv-vibehack, a free and open-source tool for Android TV users that removes unwanted advertisements and preloaded applications. The tool operates over Wi-Fi and allows users to customize their home screens to resemble an Apple TV interface without rooting or physical connections. It can identify and debloat various TV models, such as Xiaomi, Redmi, TCL, Hisense, Sony, OnePlus, Realme, and Nvidia Shield, but does not support Samsung, LG, or Amazon Fire TV. The process takes about 15 minutes and includes a custom launcher with features like a sleek black background, a dock for favorite apps, and a drifting clock screensaver. Users must enable USB debugging and trust their computer to initiate the debloating process, which is facilitated by a coding assistant. While the tool does not root or permanently delete anything, users are advised to back up data and review documentation carefully, as disabling critical packages may disrupt essential features.
Winsage
October 18, 2026
Microsoft Windows Production PCA 2011, the certificate for signing the Windows boot loader, will expire on October 19, 2026. This follows the earlier expiration of two other 2011 certificates in June 2026. PCs without the new certificates will still boot and receive standard updates but will miss out on new security enhancements for the early boot process. The new certificates from 2023 are replacing the 2011 certificates. The KEK certificate, essential for authorizing updates to signature databases, and the Microsoft UEFI CA 2011, which signs third-party boot loaders, will also be replaced by new certificates. Users can check their Secure Boot status through the System Information tool or Windows Security. Microsoft is gradually rolling out the new Secure Boot certificates through Windows Update, and users are advised not to disable Secure Boot to avoid complications. Dell will not issue BIOS updates for platforms that reached their end of service life before January 1, 2026. The transition to Secure Boot has faced challenges for older PCs, and developers are advised against pinning Secure Boot certificates in their applications. Multiple restarts may be required for full integration of the new certificates.
AppWizard
October 16, 2026
A report from Bitdefender reveals a malware campaign named "Midnight Mimosa" affecting budget and midrange Android smartphones, particularly those using low-energy MediaTek chipsets. This malware, embedded in devices marketed under various labels like Cubot and Doogee, operates through an application called "System" (package name com.android.system.lite) that displays hidden ads and can allow hackers to control the devices. Thousands of devices have been tracked with this malware, with 13% of affected devices located in Mexico, 8% in the United States, and less than 3% in Canada. The malware's source traces back to Android ODM Shenzhen Zediel. Additionally, Bitdefender identified 13 other ad fraud-related apps signed by the same entity that were previously available on the Google Play Store. Major manufacturers like Google, Motorola, and Samsung have security protocols to protect their firmware, unlike the affected budget brands.
AppWizard
October 15, 2026
Cybersecurity experts from Bitdefender have found that budget Android smartphones, such as the Doogee S200 X, Doogee Fire 3 Max, and Cubot KINGKONG X, may come pre-loaded with malware embedded in their firmware, posing significant security risks. This malware is introduced during the manufacturing process, particularly affecting devices with MediaTek chipsets. Thousands of users in around 150 countries, including Mexico, France, Italy, the United States, Germany, Brazil, and Spain, have been impacted. Bitdefender identified a network of 32 malicious applications disguised as legitimate utilities that generate fraudulent ad impressions. Some infected phones can function as residential proxies for criminal activities, including spam campaigns and DDoS attacks. Uninstalling the malicious app may not eliminate the infection if it is integrated into the system software, potentially requiring firmware-level remediation. Buyers of budget phones should research manufacturers' supply chain control and commitment to security updates.
AppWizard
October 13, 2026
LineageOS has released a new nightly build, LineageOS 24.0, for the Google Pixel 10 (codenamed frankel), dated October 11, 2026, with a size of 1.61 GiB and an October 2026 security patch level. The build is named lineage-24.0-20261011-nightly-frankel-signed.zip and is based on the Android 17 framework. Installation requires the latest Android 17 firmware, a computer with adb and fastboot, USB debugging enabled, and prior booting into the stock operating system. Users should check essential features like SMS and calls, and remove Google accounts to avoid Factory Reset Protection issues. Apps requiring device-integrity checks may not function correctly. Nightly builds for the Pixel 10 Pro were reported available on October 12, 2026, while builds for other models like the Pixel 10a, Pixel 10 Pro XL, and Pixel 10 Pro Fold have not yet been released.
AppWizard
October 11, 2026
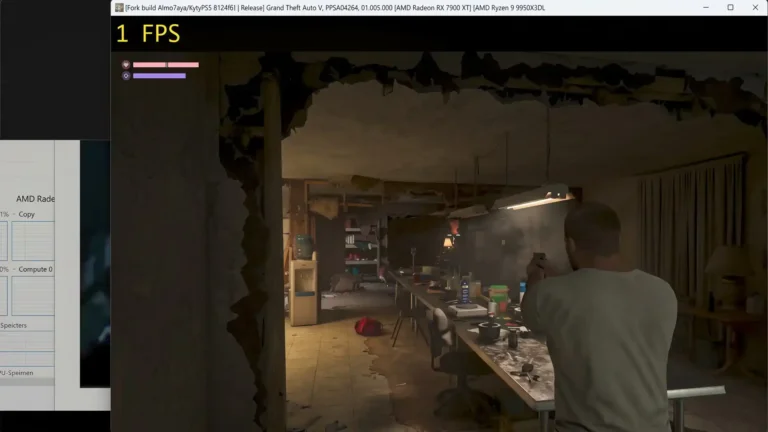
The gaming community is discussing the potential emulation of Grand Theft Auto VI on PCs, with its release scheduled for November 19th. Users are considering emulators like KytyPS5, SharpEmu, and RPCSX, but experts warn against downloading unreliable software such as PCSX5. The main challenge for emulation is the console's multi-layered security system, requiring developers to find vulnerabilities in the console's kernel and hypervisor. Current emulators can only handle basic games, and significant code optimization may take months to years. Legal challenges from Rockstar Games and Sony complicate efforts to distribute unauthorized game dumps. A stable PC port is seen as a distant goal, with the best experience expected on official consoles at launch.
Search