forensics

Winsage
October 3, 2026
Windows 11 uses a thumbnail caching mechanism to store previews of images in specific databases located in %LocalAppData%MicrosoftWindowsExplorer, such as thumbcache32.db and thumbcache1024.db. When a user deletes an image, the corresponding thumbnail may remain in the cache, as deletion does not automatically remove it from the thumbnail database. The cache retains only reduced versions of images, not the original files, which is significant in digital forensics where thumbnails can provide insights even when original files are missing. Users can manage their thumbnail cache using the cleanmgr tool to clear saved thumbnails or disable thumbnail caching through the Local Group Policy Editor or File Explorer settings.
AppWizard
July 13, 2026
Chris Livingston is exploring job simulations to find a new career and is currently engaged in a Forensics: Crime Scene Detective simulation. His understanding of crime scene investigations is influenced by media portrayals, particularly CSI: Miami. In his first case, he successfully solves a bullet-in-wall scenario, scoring 100% after several attempts. However, he struggles with a coin burglary case, ultimately scoring only 16 out of 100 due to missed evidence and failed analyses. He reflects on whether he would enjoy being a real-life crime scene detective, finding the documentation appealing but the reality of blood and violence unappealing. Livingston appreciates the game's approach to failure, which allows for learning from mistakes.
AppWizard
July 13, 2026
Edwin is currently sidelined by an illness following TennoCon, and he is expected to submit stories on Soulframe and Warframe: Tau before fully resting. New PC games being released this week include: - Ascend to Zero: A sci-fi action-roguelike with temporal manipulation. - Forensics: Crime Scene Detective: A game focused on managing fingerprint and bullet comparisons. - Soulforge Lost Path: A Survivorslike/bullet heaven game with limited inventory management. - D-Topia: A puzzle adventure about maintaining an AI-managed society. - The Incident at Galley House: A visual novel remake of a murder mystery text adventure. - Happy's Humble Burger Cult: A cooking horror game for 1-4 players. - Moss: The Forgotten Relic: A 3D platformer available for non-VR PC players. - Storebound: A cooperative horror puzzler launching into version 1.0. - Wreck Runners: A multiplayer game set in a haunted Bermuda Triangle. - Fogpiercer: A tactical roguelike deckbuilder focused on defending a train. - Frozen Ship: A first-person survival game launching in early access on the 17th. Additionally, today marks RPS’s 19th birthday, and the team will be scattered in the coming days for various events and holidays.
AppWizard
July 12, 2026
Indie developer Crux Game Studios is offering two free games, Within and Decrypt, available for download on Itch.io until July 13. Within is a 30-minute game where players control Maya, who confronts nightmarish foes to rescue her brother, Nikil. Decrypt is a sci-fi survival-horror game that takes about an hour to complete, where players investigate a missing cargo ship and uncover a sinister reality.
Tech Optimizer
June 23, 2026
A critical security vulnerability, SVD-2026-0603 (CVE-2026-20253), has been identified in Splunk Enterprise versions 10.0.0 through 10.0.6 and 10.2.0 through 10.2.3. This flaw allows unauthenticated, remote attackers to create or truncate arbitrary files on the host system by exploiting the PostgreSQL Sidecar Service endpoints. The vulnerability is actively exploited, with public proof-of-concept code available, and has been added to the CISA Known Exploited Vulnerabilities (KEV) list. Successful exploitation can lead to full remote code execution (RCE) as the Splunk user. The vulnerability arises from inadequate authentication controls on the PostgreSQL Sidecar Service endpoints, specifically /v1/postgres/recovery/backup and /v1/postgres/recovery/restore, which are accessible without authentication. It is classified under CWE-306: Missing Authentication for Critical Function and has a CVSS v3.1 base score of 9.8 (Critical). Attackers can exploit the vulnerability by sending crafted HTTP POST requests to the exposed endpoints, allowing them to create or truncate files and potentially execute malicious scripts. Indicators of compromise include unexpected files in directories such as /tmp/ or /opt/splunk/var/run/supervisor/pkg-run/, modified Splunk Python scripts, and unusual outbound connections from Splunk to unknown PostgreSQL servers. The vulnerability aligns with several MITRE ATT&CK techniques, including T1190 (Exploit Public-Facing Application) and T1059 (Command and Scripting Interpreter). Active exploitation of CVE-2026-20253 has been confirmed, and it is likely that both opportunistic cybercriminals and sophisticated threat actors will use this exploit. The affected versions of Splunk Enterprise are 10.2.0 through 10.2.3 and 10.0.0 through 10.0.6, with the issue resolved in versions 10.2.4 and 10.0.7. Organizations are advised to upgrade to fixed versions or disable the PostgreSQL Sidecar Service as a mitigation strategy.
AppWizard
May 12, 2026
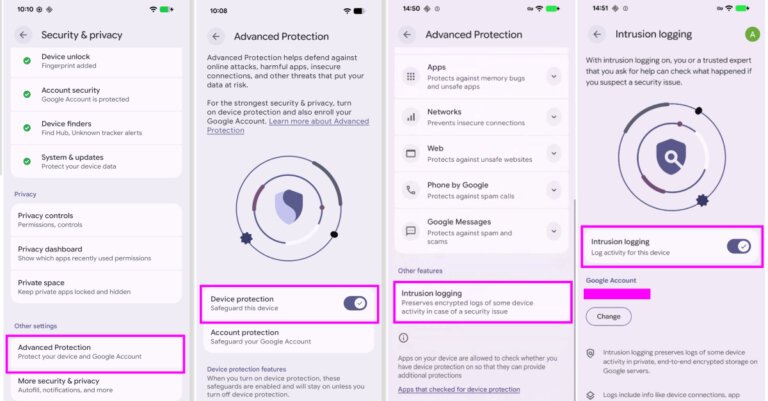
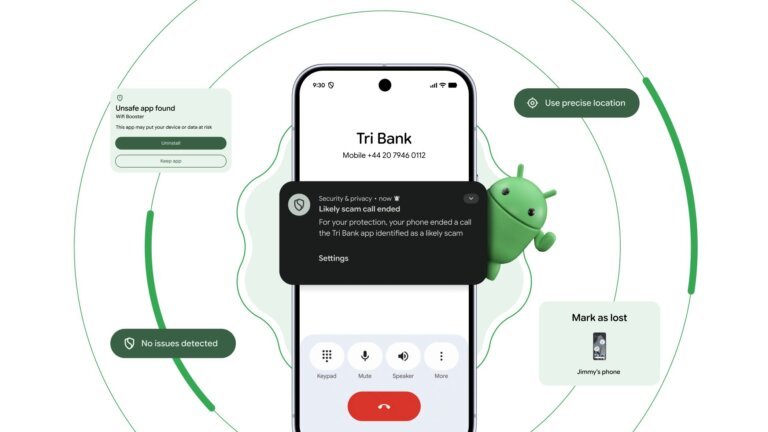
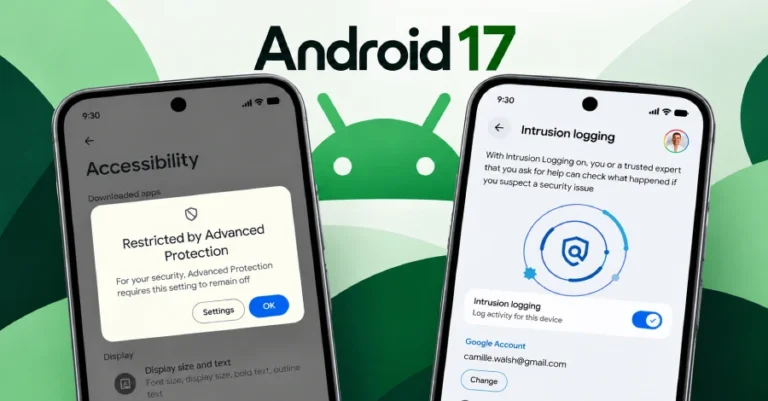
Google announced significant security and privacy enhancements at the Android Show, including features in the upcoming Android 17. Users will have increased transparency regarding location access and can manage which apps track their location. New protections against banking scams and a "Mark as Lost" feature with biometric security will be introduced. A "temporary precise location" button will allow quick access to surroundings while preventing unwanted tracking. Live Threat Detection will receive an upgrade for 2026, focusing on harmful behaviors like SMS forwarding. Dynamic signal monitoring will alert users to suspicious app behavior. Improvements to the Advanced Protection program include USB Protection for all Pixel devices running Android 16 or higher and Intrusion Logging for all Android 16 devices with the December update. Chrome on Android will enhance Safe Browsing to analyze APKs for malware. The "Mark as Lost" feature will allow biometric locking of devices, hide Quick Settings, and disable new connections. Theft protections will be enabled by default in several countries, including Argentina, Chile, Colombia, Mexico, and the U.K.
Search