fraud

AppWizard
October 9, 2026
Bitdefender researchers have identified a malware campaign called Midnight Mimosa that can be embedded in the software of low-cost Android devices before sale. This malware operates stealthily, allowing it to install and remove applications without user knowledge, generate fraudulent advertising activity, and convert devices into residential-proxy relay nodes for a botnet. It has been found on MediaTek-based, white-label devices marketed under misleading names. Users should be cautious of suspiciously cheap devices and look for signs of infection, such as unexplained ads, unfamiliar apps, sudden battery drain, and discrepancies in model names. Standard uninstallation or factory resets may not remove this malware, and users are advised to update their devices, review app lists, and contact sellers for refunds or replacements if they suspect infection. Mobile protection solutions can help monitor app behavior and alert users to potential threats.
AppWizard
October 9, 2026
Researchers from Bitdefender have discovered that thousands of inexpensive Android devices are preloaded with malware called "Midnight Mimosa," which generates fraudulent advertising revenue. This malware is embedded in the device firmware before the first power-up, making it impossible for users to uninstall. It operates with system-level privileges, allowing it to install or remove applications without user consent and to download additional code. The malware primarily aims for financial gain through advertising and click fraud, while also gathering information about devices. Bitdefender has detected this malware on thousands of devices across over 150 countries, with the highest concentrations in Mexico, France, and Italy, followed by the United States, Germany, Brazil, and Spain. Many affected devices are low-cost, white-label, or counterfeit models, often sold online. The malware stealthily installs legitimate-looking applications that display ads in invisible windows, generating ad impressions without user awareness. Bitdefender identified at least 32 disguised applications and found 13 apps in the Google Play Store with similar ad-fraud code. The source of the malware remains unidentified, but some affected firmware was signed with certificates from Shenzhen Zediel, a Chinese company. The researchers suggest that the malware could have been introduced at various stages of the supply chain, potentially by manufacturers or intermediaries.
AppWizard
September 18, 2026
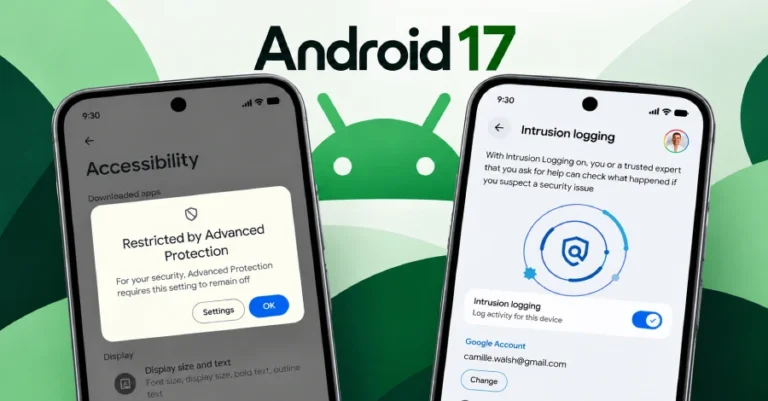
Android 17 QPR2 Beta 5 was released on September 15, 2026, with a public rollout for Pixel devices starting the next day. This beta version enhances the Proactive Assistance feature on Pixel 10 and Pixel 11 devices, allowing users more control over personalized suggestions and addressing various bugs. It is a development build for supported Pixel devices and Android Emulator images, with identified builds CP41.260828.004.A8 and CP41.260828.005.A6, and a security patch level dated August 5, 2026. The update package size for the Pixel 10 Pro XL is approximately 667 MB. The notable change in Beta 5 is the introduction of two Proactive Assistance entries in the Settings menu, allowing users to manage proactive suggestions more effectively. The updated settings page includes a "Use app content for suggestions" option, enabling users to control which applications can share screen content and notifications. Google's release notes list several fixes, including issues with Bluetooth device icons, unexpected reboots, missing volume controls, search-field highlight rendering, unlocking Private Space, HDR behavior, Google Wallet touchscreen unresponsiveness, camera crashes, and distorted Bluetooth call audio. The stable release of Android 17 QPR2 is expected in December 2026, and users are advised that Beta 5 is a developmental tool that may contain errors. Additionally, new restrictions on programmatic USSD requests for call forwarding have been introduced to reduce potential fraud.
AppWizard
September 17, 2026
On September 15, 2026, Google released the beta OS update "Android 17 QPR2 Beta 5" for Google Pixel devices in the Android Beta Program. This update includes support for new Pixel devices: "Pixel 11," "Pixel 11 Pro," "Pixel 11 Pro XL," and "Pixel 11 Pro Fold," while excluding "Pixel 6" and "Pixel 6 Pro." The update is distributed via Over-the-Air (OTA) to 23 models, including "Pixel 6a," "Pixel 7," and "Pixel 8 Pro." Key features include "Call Forwarding Hardening," which restricts access to call-forwarding USSD codes to enhance security against scams. The update also includes eight bug fixes, addressing issues with Bluetooth device type display, unexpected reboots, volume slider UI, text rendering, Private Space unlocking, HDR mode, Camera app crashes, and Bluetooth audio distortion. The build number changes to "CP41.260828.004.A8" or "CP41.260828.005.A6," with the Android security patch level updated to "August 5, 2026," and "Google Play services" upgraded to version 26.28.33 or later.
AppWizard
September 14, 2026
Malicious Android applications are being promoted through social media advertisements, particularly on platforms like Instagram and Facebook, posing significant risks to users. The Indian Cyber Crime Coordination Centre (I4C) has warned about deceptive apps advertised under names such as Night Play, Reloop, Kyss, Vimo, Rivo, Nezo, and Vixa, which often redirect users to pornographic websites to download APK files. These applications can exploit sensitive device permissions, leading to malware infections, unauthorized financial transactions, and various forms of cyber fraud. Users may be tricked into granting accessibility permissions that allow the malware to operate in the background and potentially install a VPN, rerouting internet traffic through servers controlled by attackers. Cybersecurity experts advise users to verify the legitimacy of applications before installation and to be cautious of permissions requested by unknown apps.
Search