fraud

AppWizard
September 18, 2026
Android 17 QPR2 Beta 5 was released on September 15, 2026, with a public rollout for Pixel devices starting the next day. This beta version enhances the Proactive Assistance feature on Pixel 10 and Pixel 11 devices, allowing users more control over personalized suggestions and addressing various bugs. It is a development build for supported Pixel devices and Android Emulator images, with identified builds CP41.260828.004.A8 and CP41.260828.005.A6, and a security patch level dated August 5, 2026. The update package size for the Pixel 10 Pro XL is approximately 667 MB. The notable change in Beta 5 is the introduction of two Proactive Assistance entries in the Settings menu, allowing users to manage proactive suggestions more effectively. The updated settings page includes a "Use app content for suggestions" option, enabling users to control which applications can share screen content and notifications. Google's release notes list several fixes, including issues with Bluetooth device icons, unexpected reboots, missing volume controls, search-field highlight rendering, unlocking Private Space, HDR behavior, Google Wallet touchscreen unresponsiveness, camera crashes, and distorted Bluetooth call audio. The stable release of Android 17 QPR2 is expected in December 2026, and users are advised that Beta 5 is a developmental tool that may contain errors. Additionally, new restrictions on programmatic USSD requests for call forwarding have been introduced to reduce potential fraud.
AppWizard
September 17, 2026
On September 15, 2026, Google released the beta OS update "Android 17 QPR2 Beta 5" for Google Pixel devices in the Android Beta Program. This update includes support for new Pixel devices: "Pixel 11," "Pixel 11 Pro," "Pixel 11 Pro XL," and "Pixel 11 Pro Fold," while excluding "Pixel 6" and "Pixel 6 Pro." The update is distributed via Over-the-Air (OTA) to 23 models, including "Pixel 6a," "Pixel 7," and "Pixel 8 Pro." Key features include "Call Forwarding Hardening," which restricts access to call-forwarding USSD codes to enhance security against scams. The update also includes eight bug fixes, addressing issues with Bluetooth device type display, unexpected reboots, volume slider UI, text rendering, Private Space unlocking, HDR mode, Camera app crashes, and Bluetooth audio distortion. The build number changes to "CP41.260828.004.A8" or "CP41.260828.005.A6," with the Android security patch level updated to "August 5, 2026," and "Google Play services" upgraded to version 26.28.33 or later.
AppWizard
September 14, 2026
Malicious Android applications are being promoted through social media advertisements, particularly on platforms like Instagram and Facebook, posing significant risks to users. The Indian Cyber Crime Coordination Centre (I4C) has warned about deceptive apps advertised under names such as Night Play, Reloop, Kyss, Vimo, Rivo, Nezo, and Vixa, which often redirect users to pornographic websites to download APK files. These applications can exploit sensitive device permissions, leading to malware infections, unauthorized financial transactions, and various forms of cyber fraud. Users may be tricked into granting accessibility permissions that allow the malware to operate in the background and potentially install a VPN, rerouting internet traffic through servers controlled by attackers. Cybersecurity experts advise users to verify the legitimacy of applications before installation and to be cautious of permissions requested by unknown apps.
Winsage
September 13, 2026
Cookies and data, including IP addresses, are used to deliver and maintain Google services, monitor outages, protect against spam and fraud, and measure audience engagement. When users accept all cookies, additional uses include developing new services, placing and measuring advertisements, and displaying personalized content. If users decline all cookies, only non-personalized content and ads will be shown, influenced by current content and general location. Personalized content may include tailored video recommendations and customized homepages based on user activity. Further information on managing privacy settings is available at g.co/privacytools.
AppWizard
September 10, 2026
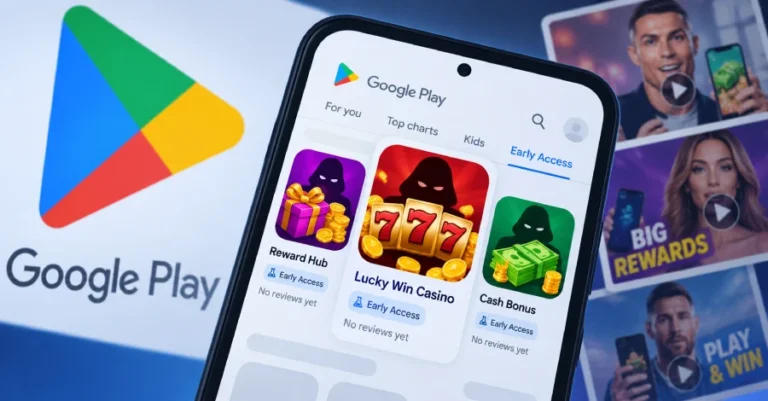
Bad actors are exploiting Google Play's Early Access program to distribute misleading applications that promise money, rewards, and casino winnings. This program allows developers to gather user feedback on unreleased apps but lacks public reviews or star ratings, enabling malicious actors to launch numerous fraudulent applications without immediate scrutiny. An example is the app "Vice Streets: Open World," which mimics Grand Theft Auto, has over 1 million downloads, and recently disappeared from the store without reviews or ratings. These deceptive apps are often promoted on social media with misleading advertisements and promise cash rewards, but users face obstacles when trying to withdraw their earnings. The primary goal of these apps is to generate revenue through excessive advertisements while circumventing regulatory requirements for legitimate gambling apps. Additionally, various malware families targeting Android devices have emerged, including Hagaseca, Mantax Otax, StreamRat, and GoldFactory's use of the Gigabud banking trojan, highlighting ongoing security threats in the digital landscape.
AppWizard
September 4, 2026
The Indian Cyber Crime Coordination Centre (I4C) has issued an advisory about malicious Android applications disguised as adult-content apps, which are promoted through social media and distributed outside official app stores. The National Cybercrime Threat Analytics Unit (NCTAU) warned that these apps can compromise mobile device security by requesting sensitive permissions and may install additional software without user consent, leading to unauthorized financial transactions. Users are advised to download apps only from trusted sources like the Google Play Store, avoid installing APK files from unverified sources, and refrain from granting accessibility permissions to untrusted applications. Recommendations include regularly reviewing installed apps, keeping Google Play Protect enabled, and monitoring bank accounts for unauthorized activities. Victims of cyber fraud are encouraged to report incidents via the national cybercrime helpline or the government’s reporting portal.
Search