Group Policy Editor

Winsage
September 22, 2026
Administrators can manage taskbar settings in Windows by either freezing current configurations or restricting user modifications through the Registry or Group Policy. The Group Policy Editor is available in Windows Professional, Education, and Business editions. To lock down taskbar changes via the Registry, access the Registry Editor, navigate to HKEYCURRENTUSERSoftwareMicrosoftWindowsCurrentVersionPoliciesExplorer, create a new DWORD (32-bit) value named TaskbarLockAll, set its value to 1, and confirm. This will grey out certain options in the Taskbar settings. In the Group Policy Editor, navigate to User Configuration → Administrative Templates → Start Menu and Taskbar, enable "Lock all Taskbar Settings," and confirm. To prevent standard users from altering taskbar settings, navigate to HKEYCURRENTUSERSoftwarePoliciesMicrosoftWindowsExplorer in the Registry and create a new DWORD (32-bit) value.
Winsage
September 19, 2026
Users are experiencing freezing issues with web applications on PCs due to a bug in Microsoft Edge version 153, which causes windows to become unresponsive to mouse and keyboard inputs. Microsoft has acknowledged the problem and suggested reverting to version 152 as a temporary solution. To downgrade Microsoft Edge, users must disable updates through the Group Policy Editor, download the MSI file for version 152, and execute a rollback command in the Windows command prompt. After completing these steps, users can verify the version of Microsoft Edge to confirm the rollback.
Tech Optimizer
July 9, 2026
Certain LG monitors are reportedly installing software on Windows PCs without user consent, including unsolicited advertisements for McAfee antivirus. This was discovered by a Reddit user who found the "LG Monitor App Installer" in their Windows event log. The application may install itself automatically via the Microsoft Store or Windows Update and is difficult to remove. Users can disable the app's automatic startup or uninstall it, but it may reinstall in the future. Windows Pro users can use the Group Policy Editor to prevent automatic installations of manufacturer-specific applications. The incident raises concerns about user control and transparency regarding unsolicited software installations.
Winsage
June 11, 2026
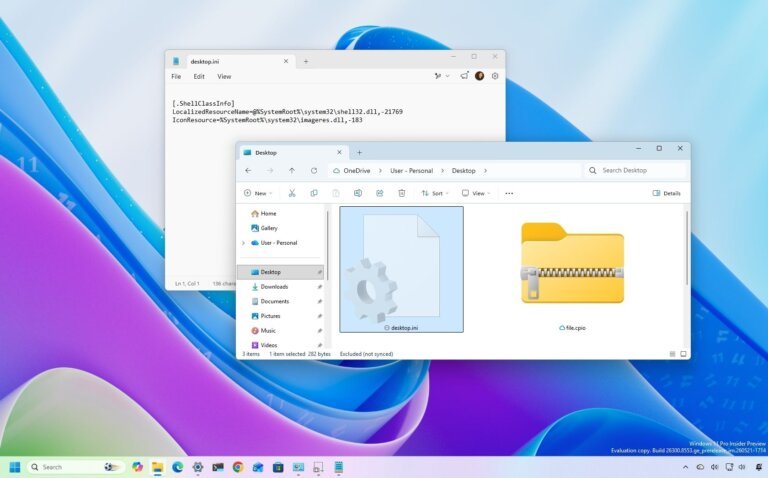
In the June 2026 Security Update for Windows 11 and Windows 10, Microsoft implemented a change that prevents custom folder icons and localized folder names from appearing if derived from an untrusted "desktop.ini" file. Users may initially perceive this as a bug, as folders may revert to default settings without user intervention. To maintain customizations, organizations should add trusted sources to the "Trusted Sites" list via Control Panel. Businesses can enable the "Allow the use of remote paths in file shortcut icons" policy through the Group Policy Editor, although this may reduce security. Users can also remove the Mark-of-the-Web tag from trusted "desktop.ini" files using PowerShell commands. This update reflects a broader trend of prioritizing security over customization in the operating system.
Winsage
June 11, 2026
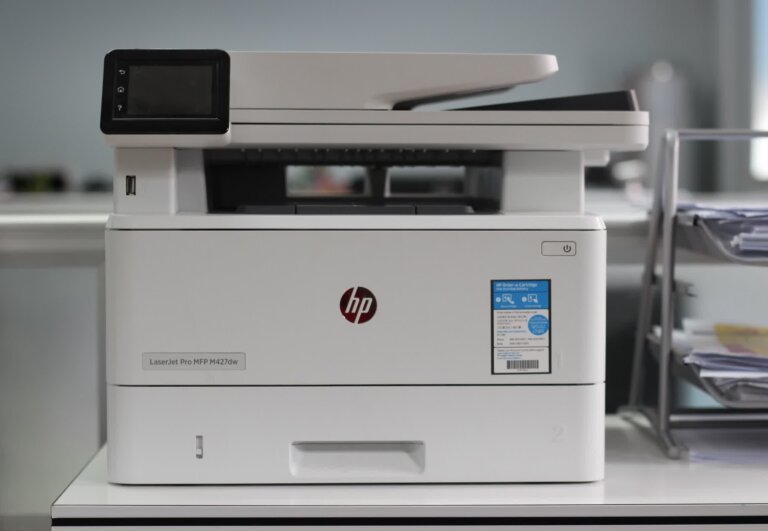
Microsoft is introducing Windows Ready Print (WRP), a new printing model that aims to modernize the printing experience on Windows by integrating contemporary communication standards like the Internet Printing Protocol (IPP) and Universal Print. WRP will manage newly installed printing devices by default starting in July 2026, while older printers and OEM drivers will still function on newer Windows releases. The initiative focuses on simplifying printing processes and enhancing reliability, with new options for customization available in Windows printer preferences. Users and administrators can choose to enforce or disable WRP-based print management. Additionally, new policies in Group Policy Editor will allow for the selection or blocking of drivers through WRP. The initiative is supported by the Mopria Alliance to improve security and compatibility in printer management across devices.
Winsage
June 10, 2026
Microsoft has released Windows 11 Experimental build 26300.8553, which includes customizable Start menus, enhanced search functionalities, and a refined Taskbar. A significant upgrade is the rebranding of the Modern Print Platform to Windows Ready Print, aimed at modernizing and securing the printing process. Microsoft is phasing out support for third-party printer drivers via Windows Update, transitioning to the Internet Printing Protocol (IPP) and the native Windows IPP printer driver. Starting July 2026, new printer installations on eligible devices will default to Windows Ready Print, though users can choose between Windows Ready Print and the traditional OEM process. This setting can be adjusted through the printer preferences in Settings and modified via Group Policy. Users can also enable Windows protected print mode to default to Windows Ready Print.
Winsage
May 30, 2026
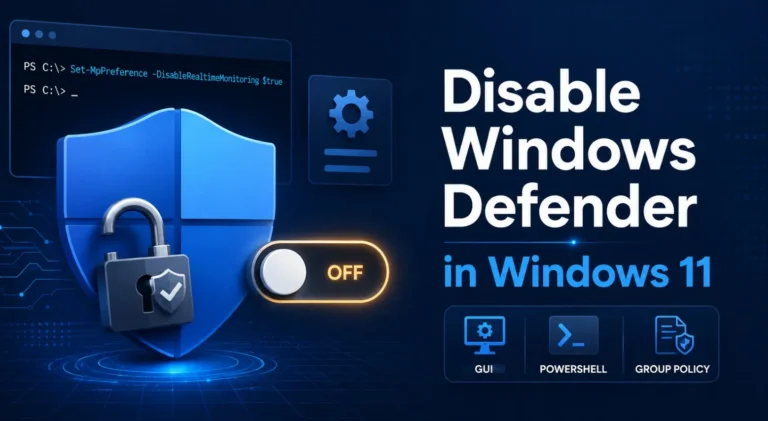
Disabling Windows Defender is common among users setting up virtual machines or optimizing build processes, but it can be frustrating due to Windows 11's resistance to such actions. Many guides suggest using outdated registry keys, which are often reverted by updates, leading to repeated attempts to disable the protections. Users may disable Defender for several reasons, including performance issues with virtual machines, conflicts with Android emulators, hindrances in development environments, troubleshooting disk performance, and security testing in isolated labs. However, disabling antivirus software increases exposure to threats. Microsoft Defender includes components such as Antivirus, Real-Time Protection, Cloud-Delivered Protection, Tamper Protection, and Defender for Endpoint. Tamper Protection is a significant barrier to disabling Defender, as it prevents unauthorized changes to security settings. Key considerations before disabling Defender include the need for administrator rights, the effect of Tamper Protection, potential resets from Windows Updates, temporary toggles for Real-Time Protection, and the option to install third-party antivirus software, which places Defender in passive mode. Methods to disable Defender include using the Windows Security GUI, PowerShell commands, Command Prompt, or Group Policy (available only for certain editions). Disabling Tamper Protection requires accessing the GUI or being managed by an organization. To check if Defender is disabled, users can use PowerShell to review specific fields. Common reasons for Defender reactivating include enabled Tamper Protection, system reboots, Windows Updates, lack of third-party antivirus, and security policy refreshes. Installing a legitimate third-party antivirus is often the best way to maintain a consistent state. Instead of disabling Defender, users can add exclusions for specific folders related to virtual machines or development tools, allowing them to maintain protection while avoiding conflicts. Troubleshooting common problems includes ensuring elevated sessions for PowerShell, checking Tamper Protection status, and understanding the limitations of the Group Policy editor based on the Windows edition. Disabling Defender may be appropriate in specific scenarios, but for regular use, especially on machines handling sensitive tasks, the risks generally outweigh the benefits. Using exclusions is recommended for performance improvements without compromising security.
Search