harvesting

AppWizard
October 10, 2026
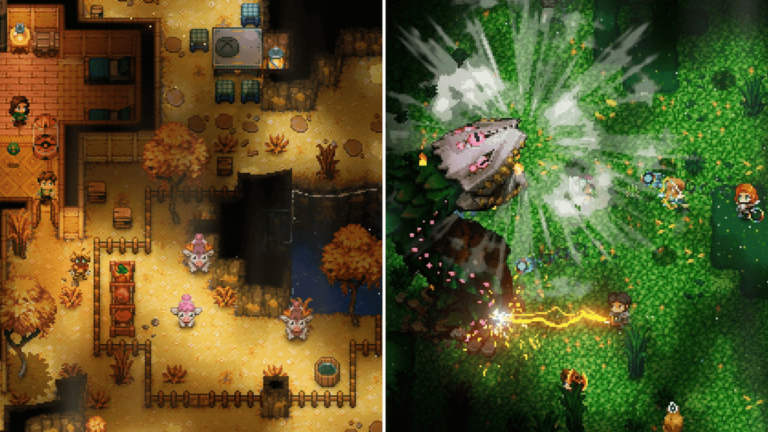
Developer Pugstorm is offering a free play weekend for its open-world survival game, Core Keeper, on Steam. The game, launched two years ago, allows solo or cooperative play with up to seven friends and features survival tasks like resource harvesting, crafting, and base building. Players can explore diverse biomes, level up skills, and engage in life simulation activities while combating legendary titans. The free play weekend ends at 6 PM BST on October 12, and players' progress will be saved if they decide to purchase the game afterward. Core Keeper is currently available at a 40% discount, priced at £9.59/$.99, down from £15.99/$.99, until October 22. The game has a 'Very Positive' review score of 94% on Steam.
AppWizard
August 30, 2026
The author revisited the MMO Star Wars Galaxies on a private server, experiencing its chaotic environment in Mos Eisley and reflecting on the game's charm despite its outdated graphics and minimal quests. The gameplay allowed for leisurely exploration and connection with other players, contrasting sharply with the fast-paced, task-oriented nature of modern MMOs like World of Warcraft. The author appreciated the freedom to engage with the game at their own pace, discovering player-created content and enjoying incidental interactions that evoke the essence of the MMO experience. The community surrounding Star Wars Galaxies continues to preserve its spirit, highlighting a sense of life and connection that is often lacking in contemporary MMOs.
TrendTechie
August 21, 2026
A playable version of GTA 6 has not been released, despite numerous online claims and links on torrent trackers that often contain malicious software. Speculation began with a user named CyberLeek posting alleged gameplay recordings, leading to misinformation, impersonations, and AI-generated videos. Experts from NordVPN have noted an increase in fake leaks and the risks associated with accessing dubious links. Marius Briedis from NordVPN highlighted that fake downloads and credential harvesting thrive in this environment. There are community speculations about potential leaks from Rockstar, but no official comments have been made by Rockstar Games or Take-Two Interactive. An official gameplay reveal for GTA 6 is scheduled for August 27, with the game set to launch on PS5 and Xbox Series on November 19.
AppWizard
August 16, 2026
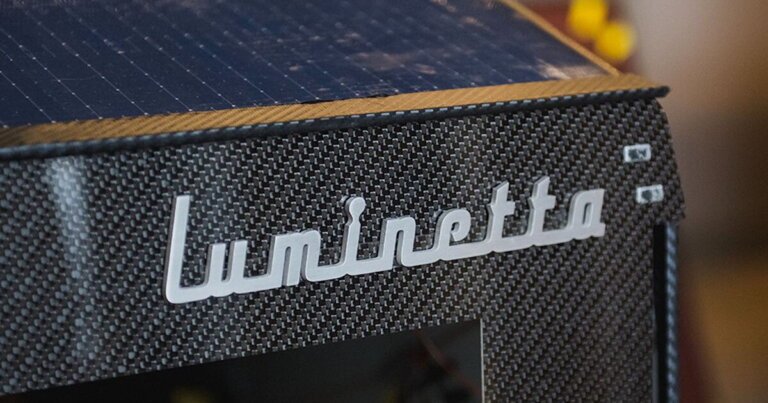
The Deep Orange 17, an experimental solar prototype developed by graduate students at Clemson University, is named 'Luminetta' and features a boxy design inspired by the boxfish. It weighs 1,212 lb (550 kg) and incorporates over 1,700 photovoltaic cells, allowing it to generate up to 5.7 kWh of energy per day. The vehicle's solar array can potentially provide an additional 31 miles (50 km) of range from sunlight. The design focuses on extreme weight reduction and employs a skeletal chassis made from 3D-printed metal joints and lightweight composite body panels. The project aims to demonstrate the feasibility of an energy-positive vehicle, although its performance relies on ideal conditions and raises concerns about crash safety and comfort.
Winsage
August 14, 2026
CoolClient is a sophisticated backdoor family linked to the HoneyMyte APT group, actively used in cyber-espionage campaigns targeting organizations in Asia and Russia since its initial disclosure in 2022. It has capabilities such as keylogging, clipboard theft, credential harvesting, and system reconnaissance. Investigations in 2023 revealed enhancements, including clipboard theft and HTTP traffic interception. By late 2025 and into 2026, a variant was noted that could deploy a signed kernel-mode driver as a Windows service, improving its stealth and operational capabilities. In a recent campaign targeting Myanmar, the HoneyMyte group used PlugX to deploy CoolClient components. They configured Microsoft Defender to exclude a fake Windows Defender installation directory and a renamed executable, defender.exe, to avoid detection. Persistence was achieved through a scheduled task that executed defender.exe with SYSTEM privileges at startup, which sideloaded the malicious libngs.dll to initiate the CoolClient execution chain. The latest CoolClient variant has a multi-stage execution chain, including: - defender.exe / Sang.exe: Exploited legitimate application for DLL sideloading. - libsrapc.dll: Benign dependency for the Sangfor application. - libngs.dll: First-stage loader that decrypts and loads the next stage. - loadcert.ini: Second-stage DLL implementing core functionalities. - cert.ini: Final-stage implant for command and control communication. - time.ini: Configuration file for CoolClient. The execution begins with the legitimate Sangfor application loading libngs.dll, which uses obfuscation to conceal its operations. The second stage, loadcert.ini, is injected into synchost.exe and performs tasks including persistence and process injection. The kernel-mode driver deployment routine involves decrypting time.ini, verifying privileges, and creating a service to execute the driver, enhancing stealth. The deployed kernel-mode driver, msagent.sys, is digitally signed and helps hide processes, files, and registry objects, making detection more difficult. The latest variant continues to target organizations consistent with previous HoneyMyte activities, with confirmed victims in Myanmar, Mongolia, Pakistan, and Russia, including government entities. The deployment of CoolClient as a secondary backdoor after a PlugX infection indicates a strategic approach to maintain access to compromised systems. The malware is confirmed as a new variant of CoolClient associated with the HoneyMyte threat group, with the kernel-mode driver marking a significant advancement in its capabilities.
AppWizard
August 6, 2026
A report from the Electronic Frontier Foundation (EFF) highlights concerns about third-party software development kits (SDKs) in mobile applications collecting and sharing user location data with advertising companies, often without user consent. Many developers use these advertising SDKs for monetization, but their default settings allow for location data collection. This data is sent to advertising companies and location data brokers, which can misuse it in sensitive contexts. Users may unknowingly expose their location data when granting permissions to apps, as third-party SDKs can access this information without clear user awareness. The EFF identified several advertising SDKs, including InMobi, BidMachine, Verve’s HyBid, and Huawei’s Petal Ads, that collect and share location data by default. Developers are encouraged to review SDK settings to protect user privacy, and the EFF calls for regulatory scrutiny of data harvesting practices.
Search