infection

AppWizard
October 9, 2026
Bitdefender researchers have identified a malware campaign called Midnight Mimosa that can be embedded in the software of low-cost Android devices before sale. This malware operates stealthily, allowing it to install and remove applications without user knowledge, generate fraudulent advertising activity, and convert devices into residential-proxy relay nodes for a botnet. It has been found on MediaTek-based, white-label devices marketed under misleading names. Users should be cautious of suspiciously cheap devices and look for signs of infection, such as unexplained ads, unfamiliar apps, sudden battery drain, and discrepancies in model names. Standard uninstallation or factory resets may not remove this malware, and users are advised to update their devices, review app lists, and contact sellers for refunds or replacements if they suspect infection. Mobile protection solutions can help monitor app behavior and alert users to potential threats.
Winsage
October 5, 2026
Microsoft has warned Windows users about a cyber threat that disguises itself as a CAPTCHA test, where cybercriminals use fraudulent verification pages to trick users into executing commands that can install malware. This tactic involves users being directed to a compromised website that presents a fake verification window, prompting them to copy text and execute it in the Windows Run dialog. This method allows attackers to bypass antivirus software by pre-loading malicious scripts disguised as harmless images in the browser's cache. Once activated, the malware collects system information, steals data, and maintains long-term control over the system. Microsoft recommends using robust security software and being aware that no legitimate service will ask users to copy and paste commands into system dialogs.
AppWizard
September 30, 2026
September 30 marks 28 years since the events that shaped Leon S. Kennedy in the Resident Evil franchise, particularly the Raccoon City incident caused by Umbrella Corporation's bioweapon experimentation. Key moments from the series include: - In Resident Evil Village, players experience a terrifying chase involving a giant fetus, creating a lasting impression of horror. - Resident Evil 7 features Marguerite Baker, known as "Spider-Mum," whose grotesque appearance leaves a significant impact on players. - In Resident Evil 2, the tension from being pursued by Mr. X (T-00) is heightened by the haunting sound of his footsteps. - The emotional scene in Resident Evil 2 with Robert Kendo trying to comfort his daughter Emma as she succumbs to the outbreak resonates deeply with players. - In Resident Evil: Revelations 2, the decision to leave Moira behind results in a gut-wrenching emotional fallout. - The Keeper's Diary from the original Resident Evil explores the descent into madness due to T-virus infection, creating a disturbing narrative.
AppWizard
September 30, 2026
FOV 90 discusses the first-person shooter (FPS) genre, highlighting its history, community traditions like organized scrimmages, and various gameplay modes. The column features a voting round with matchups between different FPS modes, including Team Deathmatch vs. FFA/Deathmatch, Battle Royale vs. Extraction, Conquest vs. Domination, Bomb Defusal vs. Hostage, Gun Game vs. Payload, Infection vs. Prop Hunt, VIP vs. Capture The Flag, and Attack & Defend vs. King of the Hill. Voting closes on Saturday, October 3 at 11:59 PM PDT, with results to be revealed the following week.
AppWizard
September 28, 2026
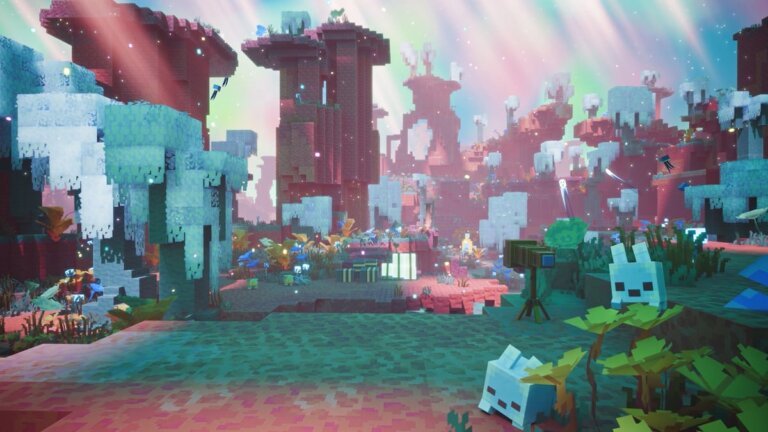
Mojang hosted Minecraft Live, revealing developments including Minecraft Dungeons II and new icy biomes. The most notable announcement was the introduction of a new dimension called "the Sift," which will be added after 14 years. The Sift features a vibrant, cotton candy-colored aesthetic with elements like pink weeds and a blue bunny, contrasting with the darker themes of previous updates. It will be included in the core game in 2027 but will first appear in Dungeons II. Discussions among players are mixed, with some expressing excitement and others skepticism about its design.
AppWizard
September 22, 2026
Cybersecurity researchers at Zimperium have identified a new strain of malware called RatHat, targeting Android devices and linked to threat actors from China. RatHat uses generative AI to maintain persistence and control over infected devices. The malware is typically spread through social engineering, tricking users into downloading counterfeit applications that appear legitimate. Once installed, RatHat requests accessibility permissions, activates Wireless Debugging, and can capture text messages, create overlays, and steal passwords and multi-factor authentication codes. Its AI capabilities allow it to navigate the device interface in real-time, making detection by security software more difficult. To protect against RatHat, users should avoid downloading apps from untrustworthy sources, and removal requires a factory reset of the device.
AppWizard
September 19, 2026
A new Android malware called RatHat has emerged, analyzed by researchers from Zimperium's zLabs. It spreads through deceptive smishing texts and malicious ads that lead users to counterfeit download pages for popular apps. Once installed, it manipulates Android's Accessibility Service to gain elevated access by enabling Wireless Debugging and retrieving authentication codes without user intervention. RatHat targets finance and banking apps to steal user IDs, passwords, and MFA codes, using techniques to obtain touch coordinates for PIN recovery. It can intercept SMS messages, gain limited control of the device, and reinstall itself. Users are advised against sideloading apps and granting unnecessary accessibility permissions. Google's Advanced Protection Mode and Malwarebytes for Android can help mitigate risks associated with RatHat.
AppWizard
September 19, 2026
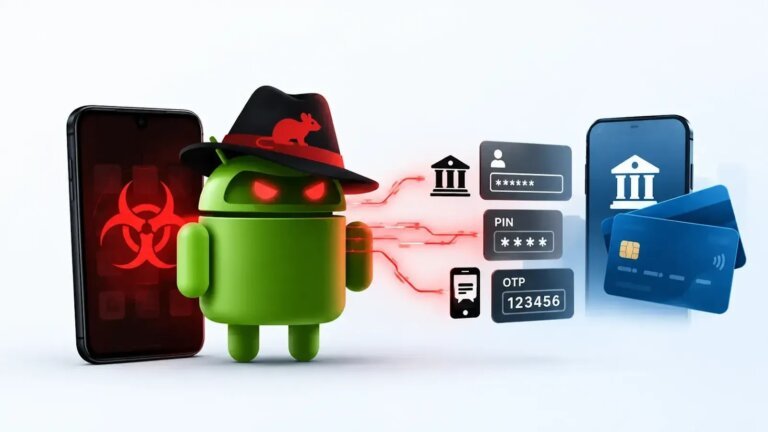
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
Search