infostealer malware

Tech Optimizer
September 10, 2026
Bitdefender is recognized for its strong detection capabilities, mid-range pricing, and minimal system impact. Malwarebytes offers a free scanner for cleaning infected Macs, while Intego specializes in macOS with features tailored for Apple users. Norton provides a comprehensive security package with VPN, backup, and identity monitoring features. Gen Digital owns Norton, Avast, AVG, and Avira, indicating that these brands share threat intelligence and engineering resources. The 2026 Mac Antivirus Scorecard ranks Bitdefender highest with a score of 8.8, followed by Intego (8.2), Malwarebytes (8.3), ESET (8.3), and Norton (7.4). Pricing structures often include discounted first-year rates that can double upon renewal. Free options include Avast and Avira with real-time protection, while Malwarebytes offers a free on-demand scanner. Multi-device licensing can provide better value, and business Macs should use business licenses for essential features. macOS has built-in protections like XProtect and Gatekeeper, but third-party antivirus solutions can enhance security against newer threats.
Winsage
August 27, 2026
Windows holds a 71 percent share of the desktop market, with over 1.6 billion active Windows PCs globally. In contrast, macOS accounts for just over seven percent of the market, rising to nearly 20 percent when combined with OS X. Windows users face a variety of threats, including trojans and riskware, and in 2025, Windows users encountered seven times more malware than macOS users. Surfshark's data indicates that macOS users are increasingly targeted by phishing attacks, which pose significant financial and personal risks.
AppWizard
April 30, 2026
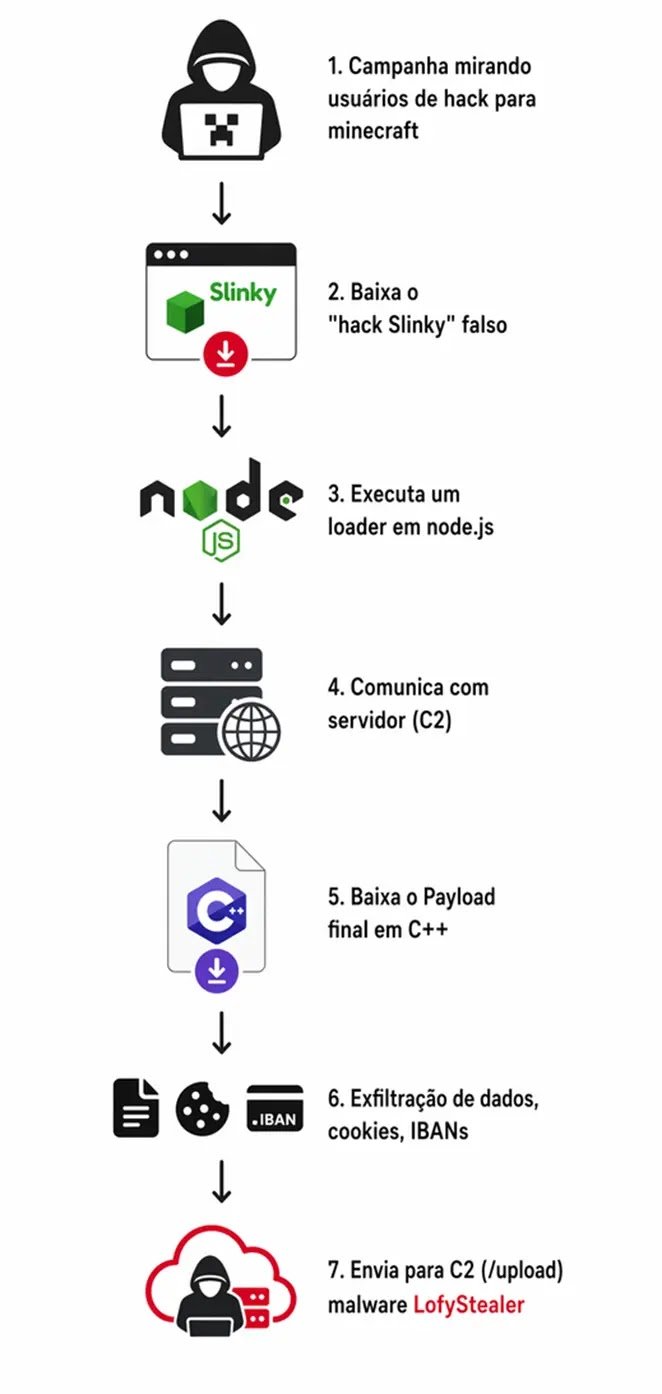
A new infostealer malware called LofyStealer is targeting the gaming community, particularly Minecraft players, by disguising itself as a cheat tool named “Slinky.” It employs a two-stage attack to extract sensitive information from eight major web browsers, including Chrome and Firefox, while evading detection by security software. The malware siphons off cookies, saved passwords, payment card information, and session tokens. Researchers at Zenox.ai identified LofyStealer, linking it to the Brazilian cybercrime group LofyGang, which has been active since October 2022. The malware uses social engineering tactics to appear legitimate and operates as a Malware-as-a-Service platform, offering both Free and Premium tiers to buyers. Its technical sophistication is evident in its method of in-memory browser injection, which allows it to bypass security defenses. The stolen data is compressed and sent to a command-and-control server. Users are advised to avoid downloading unofficial game mods and enable multi-factor authentication to reduce the risk of credential theft. Security teams should monitor for specific behavioral indicators related to the malware's operations.
AppWizard
March 13, 2026
The FBI is investigating malware hidden in several video games on the Steam platform, targeting users from May 2024 to January 2026. The investigation includes games like BlockBlasters, Chemia, Dashverse, DashFPS, Lampy, Lunara, PirateFi, and Tokenova, with some previously removed from Steam for malicious content. Steam had over 132 million monthly active users and more than 117,000 games in 2025. The FBI is reaching out to affected gamers, ensuring victim confidentiality and potential eligibility for services under federal and state law. This incident is part of a broader trend of malware targeting gamers, with previous cases involving fan games and cheat software affecting millions of accounts.
Tech Optimizer
October 21, 2025
Lumma Infostealer is a sophisticated information-stealing malware that targets high-value credentials and sensitive assets on Windows systems. It is distributed through a Malware-as-a-Service (MaaS) model, allowing inexperienced attackers to conduct data theft campaigns. Lumma is primarily deployed via phishing campaigns disguised as cracked or pirated software, often hosted on legitimate platforms like MEGA Cloud. Upon execution, Lumma uses a multi-stage decryption process and process injection techniques to activate its payload while evading detection. The latest samples utilize the Nullsoft Scriptable Install System (NSIS) as a deceptive installer, extracting malicious payloads into the %Temp% directory and launching a counterfeit document that triggers a sequence of commands to deploy Lumma’s core. Once activated, Lumma communicates with command-and-control servers (including rhussois[.]su, diadtuky[.]su, and todoexy[.]su) to gather stored browser credentials, session cookies, Telegram data, remote access configuration files, and cryptocurrency wallet information, which is then exfiltrated for exploitation. The malware avoids detection by checking for security solutions and has a modular architecture that complicates signature-based detection. Effective detection requires behavior-based Endpoint Detection and Response (EDR) systems that monitor real-time activities. To mitigate exposure, security professionals recommend avoiding storing credentials in browsers, enforcing multi-factor authentication (MFA), and monitoring suspicious processes. Indicators of Compromise (IoC) include: - E6252824BE8FF46E9A56993EEECE0DE6 - E1726693C85E59F14548658A0D82C7E8 - 19259D9575D229B0412077753C6EF9E7 - 2832B640E80731D229C8068A2F0BCC39 Command-and-control domains include: - diadtuky[.]su - rhussois[.]su - todoexy[.]su
Search