Injection

Tech Optimizer
September 22, 2026
LastPass has identified a sophisticated scheme targeting users of its Authenticator app, involving SEO poisoning and deceptive GitHub pages that distribute malicious ZIP files disguised as legitimate software. Users searching for "LastPass Authenticator download" may encounter these counterfeit pages, which redirect them to a malicious server delivering a ZIP file containing vsdbg.exe and vsdbg.dll. The executable is a legitimate Microsoft debugging tool exploited to execute the malicious DLL through DLL sideloading, allowing the malware to run undetected. Named Rapuncel by security researchers from Delphos, this malware is undetectable by antivirus engines and targets a hardcoded list of 145 antivirus and endpoint security products, disabling them upon detection. Rapuncel harvests sensitive information, including saved passwords from over 25 web browsers, cryptocurrency wallet files from more than 30 applications, and session tokens from platforms like Discord and Steam. It also captures screenshots and compiles a profile of the infected system, uploading the stolen data to an attacker-controlled server. The malware includes a kernel driver that intercepts web traffic, allowing for advertisement injection and search result manipulation. This campaign has been active for several months, with LastPass vaults remaining unaffected. Users are advised to download applications only from trusted sources. Rapuncel establishes persistence on infected machines by installing itself as a Windows service that starts with the system and terminates activated security products. Removing the kernel driver requires booting into Safe Mode or using external recovery tools, as standard Windows utilities cannot eliminate software operating at that level.
AppWizard
September 19, 2026
The Russian government is pressuring citizens to download a mobile app called "Max," which has raised privacy and surveillance concerns. Max is a popular messaging platform in Russia and integrates messaging, government services, and payment functionalities. Research by a University of Michigan team found that Max can capture users' screens without consent, access sensitive information, impersonate users, and potentially enable cyberattacks via code injection. Despite these concerns, many Russians still use alternative messaging platforms like Telegram and Signal. Some government officials are using separate devices for Max, indicating unease about its surveillance capabilities. The app is linked to a social media company connected to the Russian government, and President Putin may have an indirect financial stake in it.
AppWizard
September 18, 2026
Google has released version 2.0 of Android Bench, which focuses on managing complex development tasks rather than minor adjustments. The new version evaluates tasks that may take engineers days or weeks to complete, such as adding features and building applications. A continuous scoring method has replaced the previous pass or fail system, assessing completion rates based on functionality, visual fidelity, and adherence to instructions. Various AI models have been tested, with GPT-6 Astra achieving a 28% pass rate, significantly lower than the previous scores around 90%. No model has achieved a 100% pass rate in porting cross-platform applications, with the best reaching 80%. AI performs better in writing new code than in refactoring existing code, facing challenges with architectural complexity and runtime validation. Android Bench utilized agents from model providers for evaluations and plans to incorporate various model combinations in future updates.
Winsage
September 15, 2026
A spear-phishing campaign linked to the Chinese threat actor UTA0560 targeted various NGOs on September 1, 2026, exploiting recently patched vulnerabilities in Google Chrome and Microsoft Windows. The campaign utilized a malicious JavaScript backdoor called GRIMWEDGE, which was deployed through a multi-stage exploit chain that involved three vulnerabilities: CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880. The attack began with spear-phishing emails that led recipients to a vulnerable U.S.-based university website, allowing attackers to redirect users to their infrastructure. The exploit chain enabled arbitrary code execution and facilitated the deployment of GRIMWEDGE, which is capable of host reconnaissance, file and process management, command execution, and payload delivery. The initial payload was an executable named "msgbox.exe," which extracted a legitimate Windows binary and a malicious DLL called "wsc.dll." This DLL initiated a sideloading chain and contacted a command-and-control server for further instructions. GRIMWEDGE allows for several commands, including system reconnaissance, directory listing, file deletion, and command execution in a hidden window. It lacks built-in persistence or lateral movement mechanisms but provides a foothold for further exploitation. Concurrently, another Chinese threat actor, JungleBamboo (APT31), used the same exploit chain to deploy a loader named SUPERSTOMP, which installs a credential-stealing Chrome extension called LONGTALE. The simultaneous use of the exploit chain by multiple actors suggests potential sharing or sale of the exploit, raising concerns about patch-gap vulnerabilities that pose risks for exploitation campaigns.
Winsage
September 9, 2026
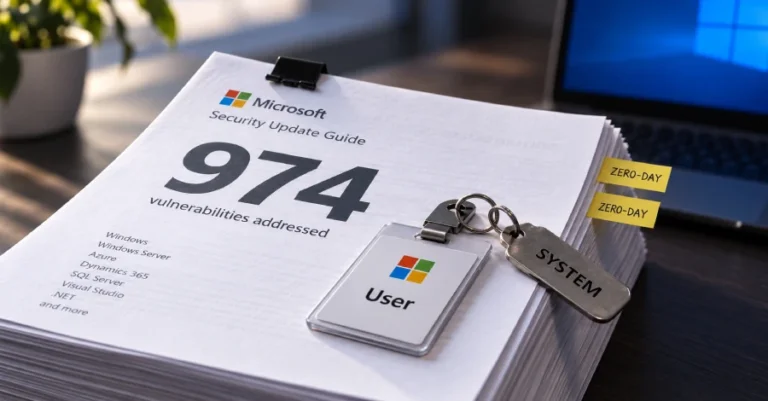
Microsoft addressed 974 vulnerabilities in its software suite during its recent Patch Tuesday, marking a record high. The breakdown includes 723 flaws in Windows, 111 in Office, 62 in SQL, and 22 in Developer Tools, with over 110 rated as critical. Two actively exploited vulnerabilities are CVE-2026-85880 and CVE-2026-81963, both allowing local privilege elevation. Other notable vulnerabilities include CVE-2026-55007 (8.1), CVE-2026-80097 (8.6), CVE-2026-69465 (8.8), and several with CVSS scores of 9.6 and above. Microsoft has patched a total of 2,760 security flaws this year, reflecting a trend of increasing vulnerability discoveries. Despite the extensive patching, no significant spike in active exploits has been observed.
Tech Optimizer
September 2, 2026
A stateful LangGraph agent was developed to streamline a 15-minute booking process, mimicking a customer service representative. It features a user-friendly Streamlit UI and a backend powered by a Postgres database. The agent can respond to customer queries, calculate service prices, manage acceptance or rejection of services, propose appointment time slots, and confirm booking details. The agent operates in two persistence modes: in-memory for quick testing and Postgres for durability. Testing can be conducted locally with Streamlit or using Docker to simulate a production environment. Docker allows the application to interact with a PostgreSQL server without local installation, enhancing reproducibility. The project includes a docker-compose.yml file to initiate a PostgreSQL container, and users can also utilize a cloud-based Postgres solution. The application behavior remains consistent regardless of the database setup. The complete source code is available on GitHub for testing and further enhancements.
Tech Optimizer
September 1, 2026
A stateful LangGraph agent was developed to streamline a 15-minute booking process, featuring a user-friendly Streamlit UI and a backend powered by a Postgres database. The agent responds to customer queries, calculates service pricing, manages service acceptance, suggests time slots, and confirms appointment details. It operates in two modes: in-memory for rapid testing and Postgres for persistent storage. Testing can be done locally using Docker, which simulates a Postgres environment, or with a hosted Postgres instance. The project includes a docker-compose.yml file to initiate a PostgreSQL 16 container, allowing the application to connect to the database. Data persistence is ensured through Docker volumes, and the application can be run with specific commands after setting up the environment variables. The system has been tested successfully, demonstrating its ability to manage bookings and maintain data integrity across sessions. Future enhancements are planned to improve the booking workflow and integrate additional communication channels.
Search