integrity checks

AppWizard
October 13, 2026
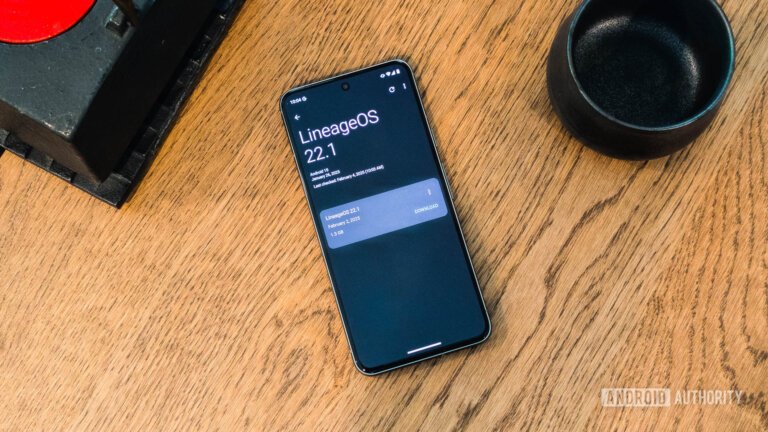
LineageOS has released a new nightly build, LineageOS 24.0, for the Google Pixel 10 (codenamed frankel), dated October 11, 2026, with a size of 1.61 GiB and an October 2026 security patch level. The build is named lineage-24.0-20261011-nightly-frankel-signed.zip and is based on the Android 17 framework. Installation requires the latest Android 17 firmware, a computer with adb and fastboot, USB debugging enabled, and prior booting into the stock operating system. Users should check essential features like SMS and calls, and remove Google accounts to avoid Factory Reset Protection issues. Apps requiring device-integrity checks may not function correctly. Nightly builds for the Pixel 10 Pro were reported available on October 12, 2026, while builds for other models like the Pixel 10a, Pixel 10 Pro XL, and Pixel 10 Pro Fold have not yet been released.
Tech Optimizer
October 10, 2026
In gaming, tools such as utilities, beta applications, and modding tools are often distributed as APK, IPA, or desktop files, and it is essential to investigate their origin, version, and any security warnings before installation. Antivirus software flags potential threats based on known malicious signatures, behavior patterns, and reputation data. Tools that modify game clients may receive heightened scrutiny, and classifications like “HackTool” or “Riskware” do not definitively indicate a file's functionality. Identical game utilities can exist on various platforms, and a familiar website does not guarantee authenticity. It is crucial to verify the publisher, update date, version, and installation method of a file. The SHA-256 hash verifies file integrity but does not ensure safety from malware. Calculating a file hash can be done using specific commands in Windows, macOS, or Linux. Multi-engine scanning platforms like VirusTotal provide insights, but a lack of detections does not guarantee safety. Even if a file matches its reference hash and raises no alerts, it may still violate online game terms. A pre-installation checklist includes confirming the publisher, checking file types, comparing SHA-256 hashes, reviewing security findings, keeping antivirus protection enabled, and consulting platform rules. A cautious approach integrates source verification, file integrity checks, security assessments, and compliance with platform regulations.
Winsage
September 3, 2026
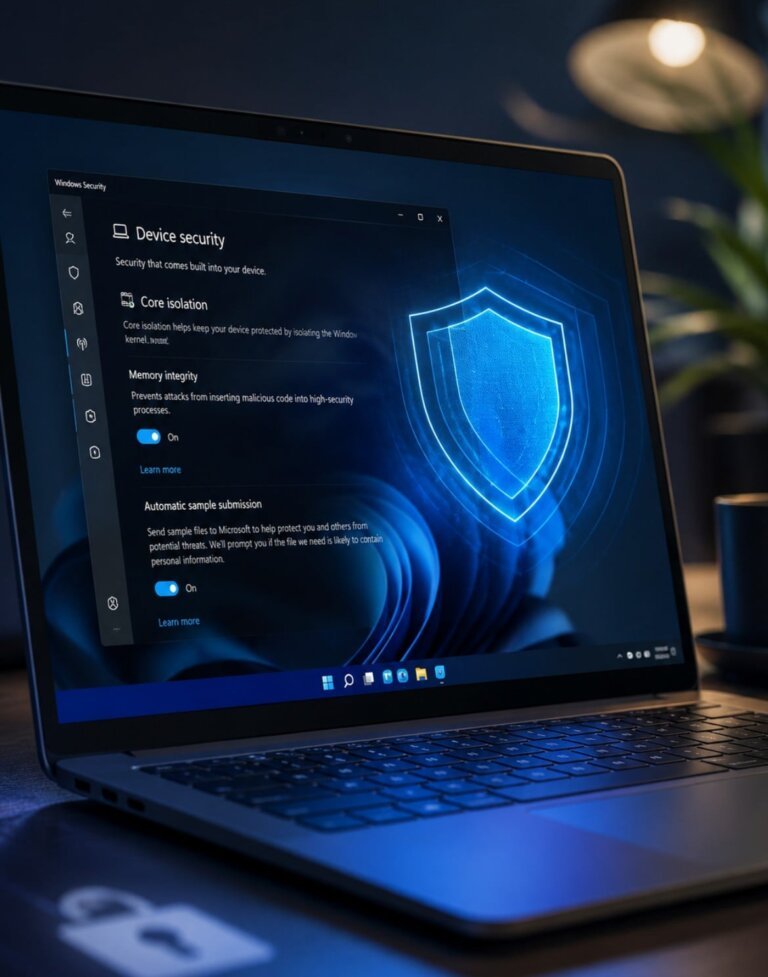
Microsoft plans to automatically activate Memory Integrity on a broader range of eligible systems starting October 2026, rolling it out through standard Windows quality updates. Prior to activation, Windows will assess hardware, drivers, and performance to ensure compatibility. Memory Integrity, part of Virtualization-based Security (VBS), uses the Windows hypervisor to create a secure environment for integrity checks on kernel code. Compatibility with drivers is crucial, as many older applications may not meet the stricter standards required for HVCI. Potential compatibility issues may arise with anti-cheat solutions, third-party input methods, and banking protection programs, which could lead to software malfunctions or boot failures. A readiness check will evaluate hardware compatibility, with eligible systems including Intel processors from the 8th generation, AMD processors from Zen 2, and Qualcomm Snapdragon 8180 or newer, along with specific RAM and storage requirements. The rollout will be gradual, and users who previously disabled HVCI will not face unexpected reactivation. Microsoft recommends updating affected applications or drivers in case of compatibility issues.
Winsage
September 2, 2026
Microsoft will automatically enable its Memory Integrity feature on more eligible Windows PCs starting in October 2026, enhancing kernel-level protection. PCs with Memory Integrity currently disabled will retain their settings. Windows will also activate Virtualization-based Security (VBS) where necessary, which supports Memory Integrity. An automatic assessment will determine device eligibility based on hardware capabilities and compatibility. The rollout applies to Windows 11 installations meeting specific hardware specifications, including an 8th Generation or newer Intel processor or AMD Zen 2 or newer processor, at least 8GB of RAM, an SSD with a minimum of 64GB, compatible drivers, and enabled hardware virtualization. Memory Integrity, also known as Hypervisor-Protected Code Integrity (HVCI), has been part of Windows since the Windows 10 era and is now more integral to Windows 11 security for new installations. However, it may impact gaming performance, leading some gamers to disable it, which Microsoft has acknowledged in its recommendations.
Winsage
May 6, 2026
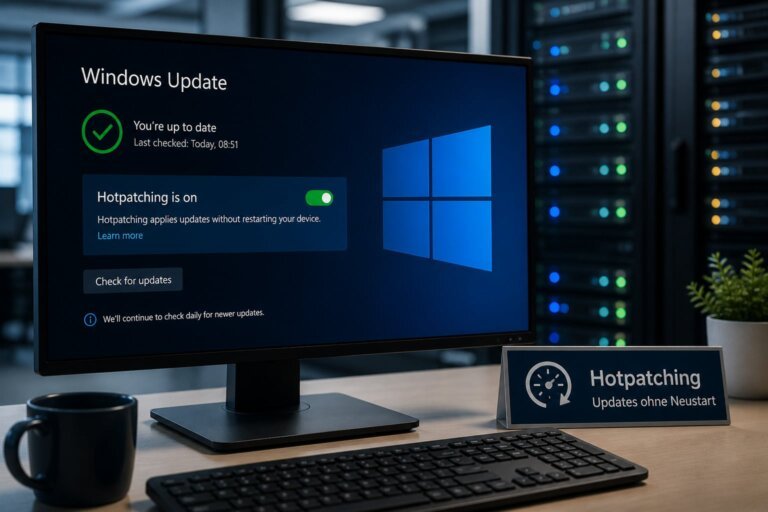
Beginning in May 2026, Microsoft will introduce Hotpatching as a default feature for compatible systems, allowing security updates to be applied without requiring a restart. Hotpatching updates code directly in the memory of running processes, enabling selective updates without interrupting the entire system. It does not replace monthly security updates but alters their activation process on eligible systems, categorized as security updates within the monthly B releases. Eligible systems must be running Windows 11 version 24H2 or newer and possess suitable licenses such as Enterprise, Education, Microsoft 365, or Windows 365. Management of these updates will be facilitated through Windows Autopatch or Microsoft Intune. Microsoft will continue to utilize baseline updates that require a restart, which will alternate with Hotpatch months. Hotpatching aims to reduce the frequency of restarts tied to security updates, particularly benefiting environments where uptime is critical. However, planned restarts will still be necessary, and robust telemetry and maintenance practices will be needed to ensure smooth operation.
Winsage
April 8, 2026
Gaming on Linux has advanced significantly due to Valve's Proton compatibility layer and the Steam Deck, allowing most single-player PC games to run on the platform. Data from ProtonDB indicates that nearly every Windows game is now playable on Linux. However, hypervisor-based DRM bypass techniques have emerged, weakening Denuvo's anti-tamper protections and reviving day-zero piracy. Hypervisors operate beneath the operating system, allowing pirates to manipulate Denuvo's validation checks, drastically reducing the time to crack games. This resurgence of piracy poses security risks, as users must disable kernel-level security features, exposing their systems to vulnerabilities. Irdeto, the company behind Denuvo, recognizes the need for updated security measures, but these could complicate the gaming experience for Linux users. Linux's open-source nature complicates enforcing kernel integrity, making effective anti-cheat and DRM systems challenging. Despite these issues, Linux gaming has seen considerable growth, but the threat of hypervisor-based piracy could jeopardize this progress and lead to tighter DRM measures that may reduce Linux compatibility.
AppWizard
March 11, 2026
UnifiedAttestation is a new initiative from Europe aimed at creating a free and open-source alternative to Google’s Play Integrity checks, which are essential for banking, financial, and government applications. Many of these applications currently rely on the Play Integrity API, which does not support custom ROMs or alternative Android forks, limiting access for users of these systems. The initiative is backed by smartphone manufacturer Volla and partners like Murena and iodé OS. UnifiedAttestation will be distributed under an Apache 2.0 license, allowing developers to adapt it, with Volla stating that integration requires only a few lines of code. However, the Graphene OS team has expressed concerns about the ethical implications of smartphone manufacturers determining which operating systems can use their applications, advocating for the regulation of the Play Integrity API instead.
Winsage
January 1, 2026
Microsoft's Resilient File System (ReFS) supports volumes up to 35 petabytes and offers robust data protection through checksums and continuous integrity checks, reducing the risk of data corruption. However, Windows 11 defaults to the NTFS file system, requiring users to use command-line tools to access ReFS features, which may deter average consumers. ReFS is primarily designed for Windows Server environments and has not gained popularity among general users. Testing shows that Windows 11 formats new drives as NTFS, making ReFS less accessible. ReFS can experience performance degradation on single-drive consumer PCs compared to NTFS and lacks features like file system compression, encryption, object IDs, and extended attributes, raising compatibility concerns. Microsoft has introduced the Agent Launchers framework for AI agent registration in Windows, amidst user backlash regarding the evolution of Windows into an "agentic OS." The Windows and Devices segment generated .3 billion in the last fiscal year, remaining flat over three years, while Gaming and LinkedIn generated higher revenues. Users have reported frequent feature changes and declining quality in Windows 11, with Microsoft's Controlled Feature Rollout system causing inconsistencies across devices. ReFS is accessible through the Dev Drive feature in Windows 11, which prioritizes performance over security. Microsoft faces competition from various fronts, including Valve's SteamOS, Apple's upcoming MacBook, and Google's Chrome OS, particularly in the education sector.
Search