JavaScript

AppWizard
September 23, 2026
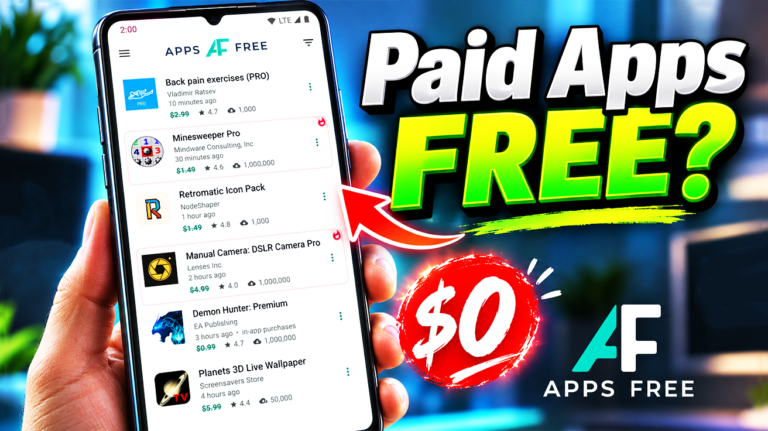
More than 70% of the world’s smartphones operate on the Android platform. Users often struggle to find apps that address specific issues, leading to a time-consuming search through numerous options. A curated list presents five applications that provide practical solutions to common mobile frustrations. 1. AppsFree: Monitors Google Play for premium apps, games, and wallpapers that temporarily drop to free, allowing users to snag deals that would otherwise be missed. Developed by ts-apps GmbH, it enables users to blacklist developers and filter low-quality offers. 2. Monocles Browser: Prioritizes user privacy by disabling JavaScript and cookies by default, reducing tracking. It has an APK size of approximately 13–14 MB and integrates ad blocking and supports Tor/Orbot proxy networks. Created by Arne-Brün Vogelsang, it offers a clean browsing experience. 3. Amarok: Allows users to instantly hide files and applications without resource-intensive encryption by obfuscating filenames and signatures. It supports multiple hiding modes and includes a “panic button” feature for quick data concealment. 4. Buckwheat: Budget manager: Requires manual input of total budget and days to cover, promoting financial reflection. It calculates daily spending allowances and provides detailed analytics. Developed by Danil Zakhvatkin, it has a user rating of around 4.6–4.7/5. 5. Chill Live Wallpaper: Offers minimalist landscapes that sync with local time and weather, providing a visually soothing experience. Compatible with Android 7.1+, it is ad-free and has a compact APK size of 5–6 MB.
AppWizard
September 22, 2026
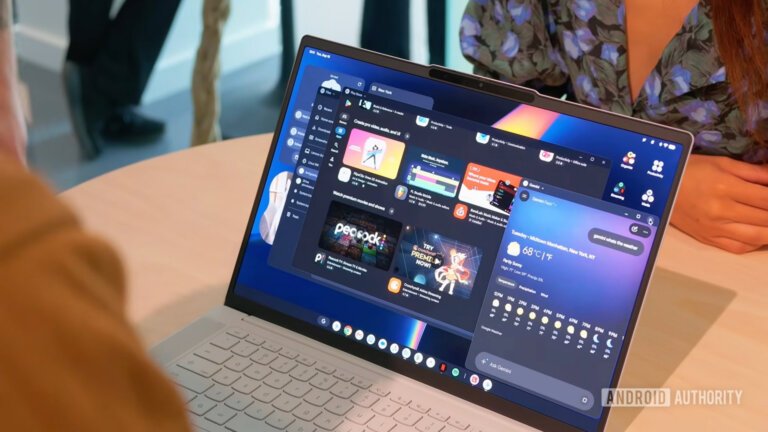
Googlebooks have officially started pre-orders ahead of their launch on October 4. The new laptop range includes a feature called Continue On, which facilitates seamless transitions between a Googlebook and a smartphone. An early preview of the Text app, a dedicated text editor available on the Google Play Store, shows it supports various programming languages and offers syntax highlighting. The app adapts well to different screen sizes, features a tab-based layout for managing multiple projects, and includes conventional tools like find and replace. While other text editor options will be available, the native Text app is specifically designed for Googlebooks. There are currently no plans to extend this app to other Android devices.
Winsage
September 15, 2026
A spear-phishing campaign linked to the Chinese threat actor UTA0560 targeted various NGOs on September 1, 2026, exploiting recently patched vulnerabilities in Google Chrome and Microsoft Windows. The campaign utilized a malicious JavaScript backdoor called GRIMWEDGE, which was deployed through a multi-stage exploit chain that involved three vulnerabilities: CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880. The attack began with spear-phishing emails that led recipients to a vulnerable U.S.-based university website, allowing attackers to redirect users to their infrastructure. The exploit chain enabled arbitrary code execution and facilitated the deployment of GRIMWEDGE, which is capable of host reconnaissance, file and process management, command execution, and payload delivery. The initial payload was an executable named "msgbox.exe," which extracted a legitimate Windows binary and a malicious DLL called "wsc.dll." This DLL initiated a sideloading chain and contacted a command-and-control server for further instructions. GRIMWEDGE allows for several commands, including system reconnaissance, directory listing, file deletion, and command execution in a hidden window. It lacks built-in persistence or lateral movement mechanisms but provides a foothold for further exploitation. Concurrently, another Chinese threat actor, JungleBamboo (APT31), used the same exploit chain to deploy a loader named SUPERSTOMP, which installs a credential-stealing Chrome extension called LONGTALE. The simultaneous use of the exploit chain by multiple actors suggests potential sharing or sale of the exploit, raising concerns about patch-gap vulnerabilities that pose risks for exploitation campaigns.
AppWizard
September 14, 2026
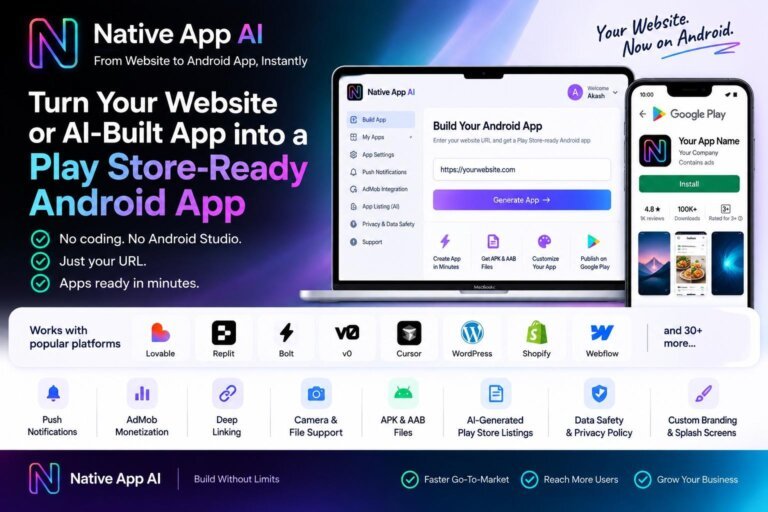
Native App AI simplifies the process of converting websites or AI-generated web apps into Android applications ready for the Play Store without needing to rebuild from scratch. It allows users to input a website URL, customize the app's features, and generate APK and AAB files for testing and publishing. The platform supports various features such as push notifications, AdMob monetization, deep linking, and custom branding. It also assists in preparing necessary information for Google Play, ensuring compliance with policies and technical requirements. This service is beneficial for SaaS companies, startups, e-commerce ventures, and creators who have existing web products.
Winsage
September 9, 2026
Recent investigations have identified the BlueMoon exploit kit, used by espionage-driven threat activity clusters, particularly linked to APT31, a China-aligned state-sponsored group, since August 28, 2026. BlueMoon exploits three vulnerabilities: CVE-2026-85046 (a type confusion vulnerability in Google Chrome's V8 engine), an unassigned V8 sandbox escape, and CVE-2026-85880 (a heap-based buffer overflow in Windows ALPC). Google and Microsoft have released patches for these vulnerabilities, which were exploited as "patch-gap" zero-days. The attack vectors typically begin with phishing emails that lead victims to malicious URLs, triggering the vulnerabilities for code execution and privilege escalation. Variants of BlueMoon have been detected, featuring modifications for specific campaigns. Notable attack chains include: - APT31 targeting NGOs and mining firms in the U.S. with a malicious browser add-on called GemStone. - UNK_LateNight targeting U.S. aerospace companies, deploying BlueMoon alongside the ShadowPad backdoor. - UNK_DoubleCheck targeting a Vietnamese manufacturer, using DLL sideloading to execute a Rust binary. - UNK_QuietRacket targeting government and financial organizations in Indonesia and Singapore, modifying BlueMoon to execute a .NET assembly. CISA added the Chrome flaw to its Known Exploited Vulnerabilities catalog on September 4, 2026, requiring federal agencies to apply patches by September 18, 2026. Indicators of compromise include specific process trees, files, folders, scheduled tasks, mutexes, and registry keys. Proofpoint has released detection rules to help organizations identify and mitigate these threats.
Winsage
August 7, 2026
Microsoft has identified a sophisticated malware campaign that uses the infrastructure of BNB Chain to spread harmful code through compromised websites. The attackers deceive visitors into executing malicious commands disguised as standard security checks, exploiting vulnerabilities in conventional website security measures. This campaign affects both businesses and individual users, utilizing ClickFix lures and EtherHiding techniques. An injected Base64-encoded JavaScript communicates with a BNB Smart Chain RPC gateway to facilitate these malicious operations.
AppWizard
July 31, 2026
Bitsight's investigation revealed that inexpensive Android TV boxes are being shipped with applications that can change their hardware identity, allowing them to impersonate popular smartphone brands like Samsung and Huawei. This operation, named Fuyao, is linked to Zhejiang Fengwo IoT Technology Co., Ltd., a Chinese company established in 2019. The H96MAXV11 model was frequently reported among the affected devices. In one day, the operation received 65,957 reports from about 38,000 unique MAC addresses, with many devices misidentified as phones due to spoofed identifiers. Fengwo has also promoted over 120,000 "AI digital humans," though details on this marketing term are vague. The command-and-control server for Fuyao sends phone profiles to devices, masking their actual hardware specifications. The operation uses machine vision technology and a YOLOv8s object-detection model to identify advertisements. Bitsight documented 40 fraud tasks, 21 unique campaigns, and 166 modules across four devices. The operation's payout structure involves 144 operator-owned domains, with an estimated gross return of .25 per device daily, potentially leading to annual revenues in the millions. Attribution to Fengwo is supported by shared TLS certificate data and public patent records, although the patents do not directly address advertising. There is uncertainty about how the fraudulent apps were installed and at what point in the supply chain they were introduced. Device owners are advised to verify Play Protect certification and disconnect suspicious devices.
Tech Optimizer
July 29, 2026
Cloud database provider Turso is developing a Postgres-compatible implementation based on its SQLite-compatible database, which was created from scratch in Rust. CEO Glauber Costa believes Postgres can benefit from modernization for cloud-native applications. Turso's SQLite reimplementation, now called Turso, uses a virtual machine architecture that may eventually support other database frontends, including MySQL and Redis. The company initially forked SQLite into libSQL but later pivoted to a cloud service named Turso. They focused on a virtual machine architecture for their rewrite, which translates SQL queries into a custom bytecode language. Turso has developed a Postgres-compatible prototype named pgmicro, which aims to run existing applications with minimal modifications. The company is also working on a database-as-a-cloud service that will allow customers to use various database types on the Turso platform.
Tech Optimizer
July 18, 2026
North Korea's Contagious Interview hackers have been using a deceptive strategy to target developers by posing as recruiters and embedding malware in SVG files. Elastic Security Labs discovered that the attackers hid malicious payloads within HTML comment blocks of these files, allowing the malware to evade antivirus detection. At the time of the findings, no antivirus engines flagged the compromised repositories, which included trojanized GitHub repositories disguised as coding challenges. The malware executed automatically at server startup and deployed four modules: a browser credential and cryptocurrency wallet stealer, a file stealer, a remote access Trojan, and a clipboard monitor. The campaign, tracked as REF9403, is part of the ongoing Contagious Interview operation attributed to North Korea's Lazarus Group, which aims to generate revenue through cryptocurrency theft. Developers are advised to audit any projects run from unsolicited sources and to monitor specific domains associated with the attack.
Search