kernel drivers

Winsage
September 27, 2026
Windows 11 requires drivers to be digitally signed, a policy aimed at enhancing security by preventing unauthorized code from executing at the kernel level. This requirement, which began with Windows Vista and became mandatory with Windows 10, version 1607, has tightened over the years, especially with the introduction of UEFI Secure Boot and TPM in Windows 11. While this enforcement protects against malware and supports anti-cheat systems in gaming, it limits user autonomy and imposes significant challenges for developers, particularly those working on smaller projects. In contrast, Linux allows users more freedom to modify their systems, though this flexibility can compromise security.
AppWizard
September 18, 2026
Google's September 2026 Pixel Update Bulletin includes patches that affect standard Android platform code, relevant to both Pixel and non-Pixel devices, which have not been included in the regular monthly Android Security Bulletin. GrapheneOS has noted that Android 17 QPR1 introduced new developer APIs not present in the Android Open Source Project (AOSP) for the first time since Android Honeycomb, with one new package and modifications to sixteen others. GrapheneOS is backporting Pixel firmware and drivers from QPR1 onto Android 17 but lacks permissions to distribute this work. Additionally, there has been a delay in Google’s compliance with a GPL source request, with access granted over two weeks after the initial request. Starting in 2027, Google will require all Android app developers to register with them and provide legal identification and signing key evidence, complicating the process of sideloading unverified apps. GrapheneOS and other organizations are advocating for the Keep Android Open campaign against these developments, which may restrict competition and tighten Google's control over the Android ecosystem.
Winsage
September 3, 2026
Microsoft plans to automatically activate Memory Integrity on a broader range of eligible systems starting October 2026, rolling it out through standard Windows quality updates. Prior to activation, Windows will assess hardware, drivers, and performance to ensure compatibility. Memory Integrity, part of Virtualization-based Security (VBS), uses the Windows hypervisor to create a secure environment for integrity checks on kernel code. Compatibility with drivers is crucial, as many older applications may not meet the stricter standards required for HVCI. Potential compatibility issues may arise with anti-cheat solutions, third-party input methods, and banking protection programs, which could lead to software malfunctions or boot failures. A readiness check will evaluate hardware compatibility, with eligible systems including Intel processors from the 8th generation, AMD processors from Zen 2, and Qualcomm Snapdragon 8180 or newer, along with specific RAM and storage requirements. The rollout will be gradual, and users who previously disabled HVCI will not face unexpected reactivation. Microsoft recommends updating affected applications or drivers in case of compatibility issues.
Winsage
August 20, 2026
Microsoft is investigating reports of game stability issues following the August Patch Tuesday update for Windows 11, specifically the release of KB5121003 for versions 24H2 and 25H2. Users have reported that certain games may become unresponsive, unexpectedly close, or trigger an "EXCEPTIONACCESSVIOLATION" error, leading to device restarts. Affected titles include ARC Raiders, MARVEL Tōkon: Fighting Souls, and The Finals. Microsoft has not confirmed if the issues are caused by their update but is looking into the situation. The update addressed 421 Microsoft CVEs, with 236 affecting Windows systems. Microsoft has also tightened its stance on outdated kernel drivers and initiated the Driver Quality Initiative to enhance OS stability.
Winsage
June 17, 2026
The Windows variant of SprySOCKS malware, developed by the Chinese threat group Earth Lusca, targets government entities globally and features advanced capabilities such as rootkit-level stealth and extensive command-and-control (C2) functionalities. It operates on Windows systems, utilizing two main variants: WINDRV, which includes kernel drivers for stealth operations, and WINPLUS, a streamlined backdoor. The malware can communicate over TCP, UDP, and WebSocket, offering over 30 C2 commands for various operations, including system information gathering and keystroke logging. WINDRV loads a driver named ‘RawWNPF’ into memory using another signed kernel driver, allowing it to conceal processes and achieve persistence. The malware's design incorporates open-source elements and exploits vulnerabilities in the software supply chain, notably using a leaked certificate for driver signing. To combat SprySOCKS, organizations are advised to implement advanced endpoint detection and response (EDR) solutions, maintain regular patching, and manage supply chain risks vigilantly. The malware's adaptability and reliance on legitimate certificates complicate detection efforts, necessitating continuous refinement of security practices.
Winsage
June 16, 2026
Cybersecurity researchers have identified two new Windows variants of the SprySOCKS backdoor, named WINDRV and WINPLUS, which were previously thought to be exclusive to Linux systems. Both variants feature hard-coded command-and-control configurations and can communicate via TCP, UDP, and WebSocket protocols. They support over 30 commands for operations such as system information collection and file management. WINDRV employs kernel drivers for stealth, obscuring network connections and allowing TCP traffic diversion. SprySOCKS was first documented by Trend Micro in September 2023, linked to the Chinese state-sponsored threat actor Earth Lusca, also known as FishMonger. The Windows variants belong to version 1.8 of SprySOCKS and utilize a kernel driver named RawWNPF for enhanced stealth. The attack chain begins with an initial access method that drops a batch script, leading to the installation of the backdoor. Evidence suggests these variants may have been used in attacks against government organizations in Honduras, Taiwan, Thailand, and Pakistan between 2023 and 2024. The WINPLUS variant was first detected in July 2024 in Pakistan. There are indications of a potential UEFI bootkit involvement exploiting CVE-2023-24932, a vulnerability in the Windows Boot Manager.
Winsage
May 11, 2026
Open-source endpoint detection tools have typically been divided between Windows and Linux, with Windows solutions focused on Sysmon and Linux solutions on eBPF or auditd. Rustinel is a Rust-based endpoint agent that consolidates these efforts by gathering telemetry from both operating systems using ETW on Windows and eBPF on Linux, normalizing the data into a unified model. It evaluates the information against Sigma rules, YARA signatures, and atomic indicators of compromise, storing alerts in ECS-compatible NDJSON format for integration with SIEM or log-analysis platforms. Rustinel supports a range of events on Windows, including process creation, network activity, and PowerShell executions, while Linux support currently includes process, network, file, and DNS telemetry. It operates in user mode on both platforms, requiring specific conditions for installation. Unlike commercial EDR solutions that use kernel drivers, Rustinel's user-mode design prioritizes simplicity and stability, although it acknowledges limitations in tamper resistance and visibility. The agent utilizes three detection engines: Sigma for behavioral matching, YARA for scanning executables, and an IOC engine for deterministic checks. While it leverages existing content familiar to defenders, it has coverage gaps for certain advanced threats. Rustinel is available on GitHub under the Apache 2.0 license.
Winsage
May 10, 2026
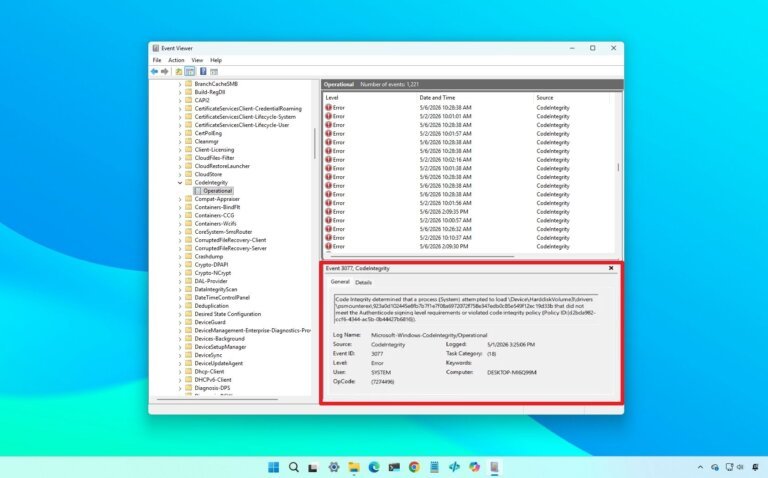
Microsoft's April 2026 Windows security update, KB5083769, may disrupt image-mount operations for backup applications such as Macrium Reflect, Acronis Cyber Protect Cloud, UrBackup Server, and NinjaOne Backup due to the addition of the psmounterex.sys kernel driver to its Vulnerable Driver Blocklist. This action was taken to address a high-severity buffer overflow vulnerability, CVE-2023-43896. The inclusion of this driver in the blocklist has rendered several backup products inoperable, and Microsoft will not retract the block for security reasons. Administrators can use Event ID 3077 in the Code Integrity log to confirm that the blocklist is causing the failures. Microsoft advises updating backup applications to versions that include necessary driver protections instead of uninstalling or pausing the security patch. Additionally, the April updates have caused other issues, such as failures in Windows Server installations and devices booting into BitLocker recovery mode.
Winsage
May 7, 2026
The Windows 11 security update KB5083769, released on April 14, 2026, introduces changes to the psmounterex.sys driver, causing compatibility issues with third-party backup solutions such as Macrium Reflect, Acronis Cyber Protect Cloud, UrBackup Server, and NinjaOne Backup. Microsoft states this is a necessary security adjustment, not a bug. The update also adds known vulnerable kernel drivers to a blocklist to enhance system security. Users can check if a driver is blocked by using the Event Viewer and looking for Event ID 3077 associated with a specific Policy ID.
Search