keystroke

Winsage
September 24, 2026
Security researchers from Graz University of Technology in Austria have discovered significant vulnerabilities in the file notification systems of major operating systems: Android, Linux, macOS, and Windows. These flaws have existed for decades and can lead to the leakage of sensitive system information. The affected systems include inotify on Linux (since 2005), FileObserver on Android (since 2008), ReadDirectoryChangesW on Windows (since 2000), and FSEvents on macOS (since 2007). The vulnerabilities allow unprivileged users to monitor file events without explicit read permissions, enabling potential attacks such as inter-keystroke timing attacks and website fingerprinting. For example, on Linux, monitoring a readable directory can leak events on files that cannot be read, allowing attackers to achieve a 93.1% to 100% accuracy rate in monitoring keystrokes. Specific vulnerabilities include CVE-2025-68788 on Linux, which received a partial fix in December 2025, and issues on Android where FileObserver can bypass app storage isolation. On macOS, limited information is available due to a lack of bypasses for private directories, while on Windows, monitoring the root directory can reveal the full path of every accessed file, allowing real-time tracking of web activity with a 97.8% accuracy rate. Microsoft has described the issue as "by-design," which has faced criticism. The researchers propose stronger mitigations, such as disallowing monitoring of entire drives on Windows and introducing a permission system for file monitoring on Windows and macOS. Their findings will be presented at the ACM CCS 2026 conference in November in The Hague, Netherlands.
Winsage
August 5, 2026
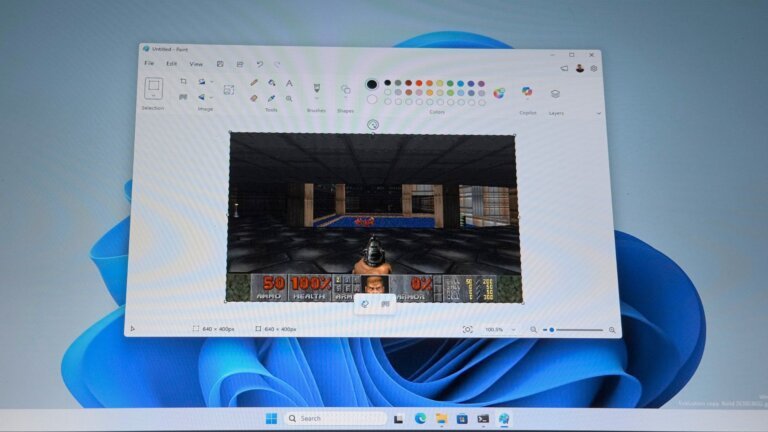
Mark Russinovich, the Chief Technology Officer of Microsoft Azure, has created a project called DoomPaint, which allows the classic game DOOM to be displayed within Microsoft Paint. The game operates through the ViZDoom engine, rendering frames headlessly and transferring them to Paint via the Windows clipboard. DoomPaint features full keyboard controls, sound effects, and a MIDI soundtrack, maintaining a frame rate of around 35 FPS. To run DoomPaint, users need to download the project from GitHub, ensure Python is installed, extract the folder, and run a batch file, which sets up a virtual environment and opens Microsoft Paint for gameplay. The default controls include movement with W/S or arrow keys, turning with A/D or arrow keys, strafing with Q/E, firing with Ctrl/F, and other functions assigned to different keys. The project uses the shareware DOOM1.WAD for the initial episode and additional maps from Freedoom due to licensing restrictions. DoomPaint differs from previous attempts to integrate DOOM into Paint by using Paint’s canvas as the sole display for the game. The clipboard race condition was addressed by allowing the application to own the clipboard as a reference-counted OLE data object. Sound effects come from ViZDoom through OpenAL, and music is played using a separate module that loops through the Windows MIDI sequencer. Russinovich utilized Claude Fable 5 for this project, demonstrating how AI tools can enhance software development.
Winsage
July 31, 2026
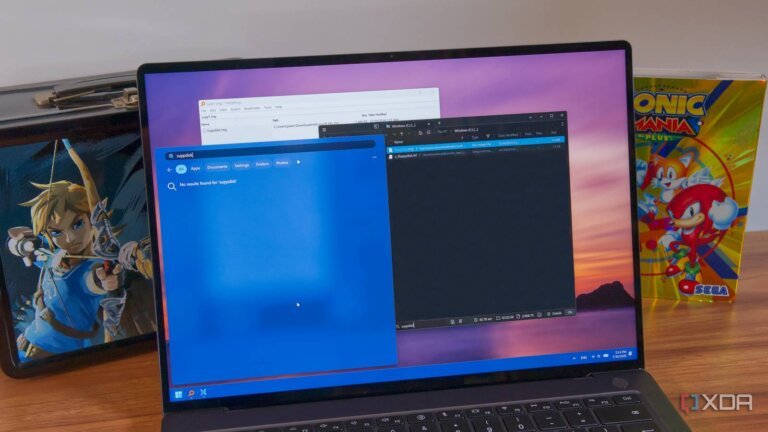
Many users struggle with disorganized files, and Windows 11's built-in search tool is often slow and unreliable, yielding poor results. Testing showed that it struggles to find files in subfolders, even with enhanced indexing enabled. In contrast, File Pilot offers faster search functionality, filtering results to the current folder and allowing expansion to subfolders with a keystroke, though it lacks wildcard search capabilities. Everything is highlighted as the best option, known for its rapid indexing and customizable search criteria, making it superior to both Windows Search and File Pilot.
Tech Optimizer
June 23, 2026
Meta has suspended its employee-tracking program after an internal security review revealed excessive accessibility to sensitive data collected from staff laptops. The program, part of the Model Capability Initiative (MCI), aimed to gather detailed information on employee interactions with work devices, including mouse movements, click locations, keystrokes, and screen content. Concerns arose regarding the privacy and security of the collected data, which included AI prompts, transcriptions, private conversations, and performance-related information. The initiative faced backlash, particularly after an engineer criticized "laptop surveillance," leading to a petition for its termination. The monitoring software was deployed on US workers’ laptops without an opt-out option, capturing comprehensive behavioral datasets. The situation highlighted significant legal and regulatory challenges, as well as the risks associated with managing sensitive data. Access controls, data minimization, and retention policies are critical to mitigate potential breaches.
Winsage
June 17, 2026
The Windows variant of SprySOCKS malware, developed by the Chinese threat group Earth Lusca, targets government entities globally and features advanced capabilities such as rootkit-level stealth and extensive command-and-control (C2) functionalities. It operates on Windows systems, utilizing two main variants: WINDRV, which includes kernel drivers for stealth operations, and WINPLUS, a streamlined backdoor. The malware can communicate over TCP, UDP, and WebSocket, offering over 30 C2 commands for various operations, including system information gathering and keystroke logging. WINDRV loads a driver named ‘RawWNPF’ into memory using another signed kernel driver, allowing it to conceal processes and achieve persistence. The malware's design incorporates open-source elements and exploits vulnerabilities in the software supply chain, notably using a leaked certificate for driver signing. To combat SprySOCKS, organizations are advised to implement advanced endpoint detection and response (EDR) solutions, maintain regular patching, and manage supply chain risks vigilantly. The malware's adaptability and reliance on legitimate certificates complicate detection efforts, necessitating continuous refinement of security practices.
BetaBeacon
May 5, 2026
ScarCruft compromised a video game platform in a supply chain attack, trojanizing its components with a backdoor called BirdCall to target ethnic Koreans residing in China. The attack enabled the threat actors to target both Windows and Android devices, turning it into a multi-platform threat. The campaign targeted sqgame[.]net, a gaming platform used by ethnic Koreans in China, known as a transit point for North Korean defectors. BirdCall has features like screenshot capture, keystroke logging, and data gathering, and relies on legitimate cloud services for command-and-control. The Android variant collects various data and has seen active development.
Search