Windows 11 Pro includes advanced features such as BitLocker for full disk encryption, Hyper-V and Windows Sandbox for running virtual machines, and integration with Azure Active Directory for business connectivity. It also offers Snap layouts for multitasking, DirectX 12 Ultimate for gaming, biometric login options with TPM 2.0 for enhanced security, and a Copilot feature for productivity assistance. A lifetime license for Windows 11 Pro is available for .97 until October 4.
A sophisticated PAYLOAD ransomware attack targeted an unnamed manufacturing organization in the Middle East, exploiting vulnerabilities in Microsoft Active Directory Group Policy. The attackers accessed the network through a compromised domain account via FortiGate SSL VPN on April 11, escalated privileges to domain administrator by April 13, and created a malicious Group Policy Object (GPO) named "PAYLOAD." This GPO was linked at the root of the domain, allowing it to affect nearly all domain-joined Windows workstations. The attackers distributed ransom notes, altered desktop images, displayed ransom messages at login, and disabled local administrator accounts. A second GPO, "win Firewall Off," was deployed to disable Windows Firewall across all profiles. The malicious policies activated on April 14 after systems were rebooted, causing widespread disruption. The attackers also exfiltrated data from file servers and published it on the dark web, while Kaspersky found no evidence of Windows file encryption or active malware processes. Recommendations for organizations include monitoring GPO creation, checking for unexpected changes, implementing multi-factor authentication for VPN access, and protecting privileged accounts.
A newly identified strain of Android malware, RatHat, utilizes generative AI to manipulate infected devices in real time. It is linked to threat actors believed to be operating out of China. RatHat serializes the device’s live Accessibility tree into XML format and communicates with a generative AI assistant to return screen coordinates, identify text, and issue navigation commands. The malware employs WebView-based HTML overlays to capture login credentials from banking and cryptocurrency applications and can infiltrate payment apps like WeChat and Alipay to extract PINs. It also features an SMS receiver and notification listener to intercept OTPs and 2FA codes.
RatHat is disseminated through smishing, malvertising campaigns, and misleading third-party forums. It employs anti-analysis techniques such as container tampering, manifest bombing, DEX bytecode poisoning, string encryption, and anti-debugging. Once installed, it gains Accessibility access, activates Developer Options, and enables Wireless Debugging, allowing it to connect to the device's local ADB service and launch control agents with shell-level privileges.
The malware captures raw touch coordinates to reconstruct PINs and unlock patterns, bypassing screenshot protections. It also includes persistence mechanisms that prevent uninstallation by presenting a fake Google Play failure overlay and automatically reinstalling itself if removed.
A sophisticated PAYLOAD ransomware attack targeted a manufacturing organization in the Middle East, exploiting vulnerabilities in Microsoft Active Directory Group Policy. The attackers gained initial access on April 11 by compromising a domain account through the company's FortiGate SSL VPN. By April 13, they escalated privileges to a domain administrator and created a malicious Group Policy Object (GPO) named “PAYLOAD,” which was linked at the root of the domain. This GPO allowed them to distribute a ransom note, change desktop images, display a ransom message during login, and disable the local administrator account. A secondary GPO, “win Firewall Off,” was used to disable Windows Firewall across all profiles. The malicious changes activated on April 14 after system reboots, causing widespread disruption. The attackers also exfiltrated sensitive data, which was later released on the dark web. Kaspersky's investigation found no evidence of file encryption or active malware processes, indicating the attack was contained within Active Directory. Recommendations for organizations include monitoring GPO modifications, implementing multi-factor authentication for VPN access, and safeguarding privileged accounts.
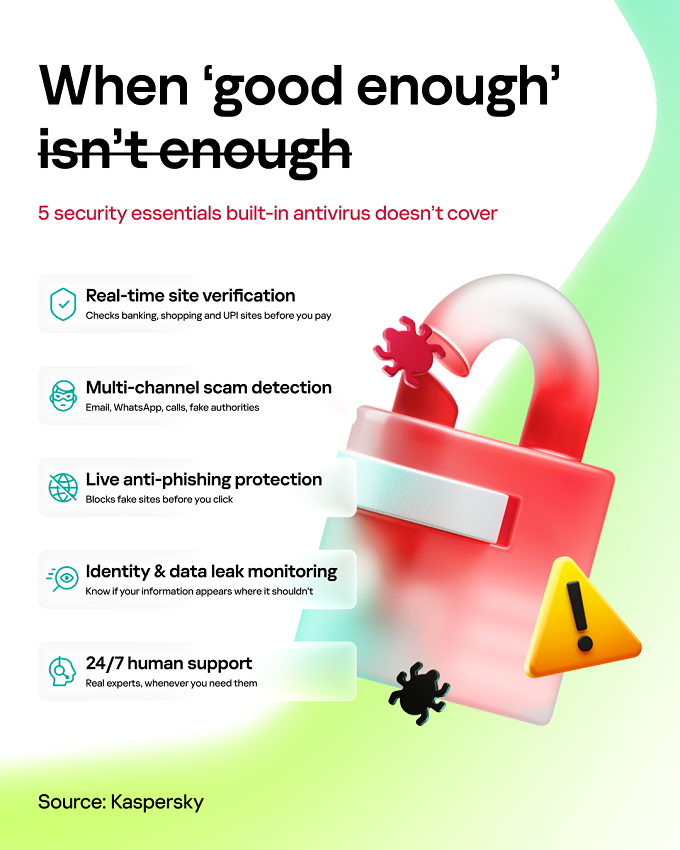
India's internet usage has rapidly evolved, with the Unified Payments Interface (UPI) transforming smartphones into banking hubs and daily tasks being conducted online. Despite this digital shift, many users rely on pre-installed security software, which may not be sufficient against increasing cyber threats. In 2025, nearly one in four internet users in India faced web-based cyber threats, with over 47.5 million threats blocked, averaging about 130,000 daily. Kaspersky's Safe Money feature provides real-time verification of banking and shopping sites, while its anti-phishing capabilities respond to rapidly changing scams. Scammers are using multi-channel approaches, prompting Kaspersky's system to flag suspicious activity across platforms. Credential theft increased by 20% in 2025, with over 225,000 attacks thwarted, and Kaspersky offers identity monitoring to alert users of data leaks. Additionally, Kaspersky Premium provides 24/7 human support for suspicious activities, addressing the limitations of standard antivirus tools in a complex digital threat landscape.
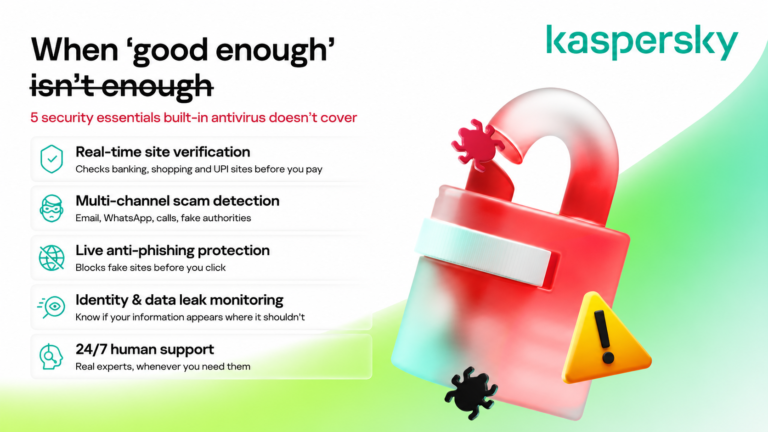
India's digital landscape has rapidly evolved, with the Unified Payments Interface (UPI) turning smartphones into banking hubs and shifting many routine tasks online. However, users often rely on basic pre-installed security software, underestimating online threats. In 2025, nearly one in four internet users in India faced web-based threats, with over 47.5 million incidents blocked. Kaspersky addresses five critical gaps in online security:
1. Real-Time Site Verification: Kaspersky’s Safe Money feature provides real-time verification of banking and shopping sites, which standard antivirus tools lack.
2. Live Anti-Phishing Protection: Kaspersky offers real-time anti-phishing capabilities with a continuously updated threat database, responding faster than traditional antivirus solutions.
3. Cross-Channel Threat Detection: Kaspersky flags suspicious activities across multiple channels, unlike single-channel antivirus tools.
4. Identity and Data-Leak Monitoring: Kaspersky alerts users when their information appears on the dark web, integrating this feature into its protection suite.
5. Round-the-Clock Human Support: Kaspersky Premium provides 24/7 human support for users facing suspicious transactions or alerts.
Credential theft targeting Indian networks increased by 20% in 2025, with over 225,000 attacks thwarted. The sophistication of digital threats in India has outpaced basic defenses, necessitating advanced protection layers.
Google has introduced a new feature called Passive Sign-In for YouTube users. This feature allows users to stay signed in to their Google accounts while using YouTube, making it easier to access videos and playlists without repeatedly entering login credentials.
Windows 11 is facing ongoing challenges with audio functionality following recent updates, particularly with the emergency update KB5129195 released on September 14. This update aimed to fix issues from the September Patch Tuesday update (KB5124008) but has led to new problems, including compromised audio output on some devices and disruptions in secure trust relationships for enterprise systems. Users have reported error messages like “This device cannot start (Code 10)” in Device Manager, and issues with USB audio devices. Microsoft is investigating these audio problems but has not provided a timeline for resolution.
Additionally, there are reports of GPU issues on AMD systems, including driver timeouts and black screens, affecting various Radeon models such as RX 6600, RX 7700 XT, RX 7800 XT, RX 7900 GRE, RX 7900 XTX, and RX 9070 XT. Some users found that uninstalling the September update alleviated these problems, but the emergency update KB5129195 does not address the GPU errors.
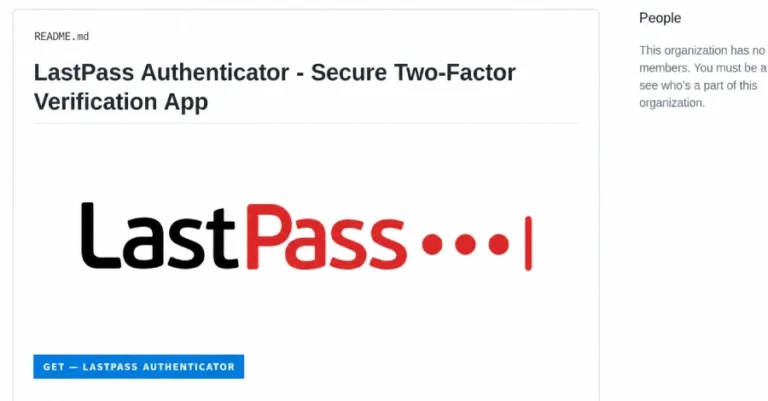
On September 17, researchers from LastPass and Delphos Labs discovered a counterfeit LastPass Authenticator installer on GitHub that installs a malicious Windows kernel driver designed to disable antivirus and steal passwords. The driver, named Alinubx.sys, was signed through Microsoft's hardware compatibility program and initially scored zero detections on VirusTotal. The fake installer is hosted on a fraudulent GitHub page that mimics a legitimate LastPass product page. When executed, the installer uses DLL side-loading to gain SYSTEM-level access and terminates security processes, allowing it to harvest saved passwords from various browsers and applications. The driver is a renamed variant of a known malicious driver, evading detection due to its new file hash. Delphos reported the driver to Microsoft, but it was not considered a security vulnerability. Users who executed the fake installer should treat their passwords and sensitive data as compromised and change them from a secure device. The malicious server has been linked to impersonation pages for multiple brands, and the loader was likely created using a specific crypter tool.