malicious app

AppWizard
September 17, 2026
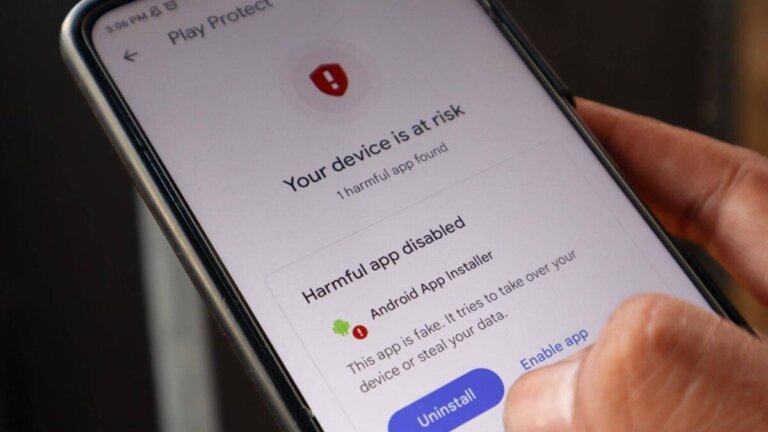
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures. RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands. The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
AppWizard
September 14, 2026
Malicious Android applications are being promoted through social media advertisements, particularly on platforms like Instagram and Facebook, posing significant risks to users. The Indian Cyber Crime Coordination Centre (I4C) has warned about deceptive apps advertised under names such as Night Play, Reloop, Kyss, Vimo, Rivo, Nezo, and Vixa, which often redirect users to pornographic websites to download APK files. These applications can exploit sensitive device permissions, leading to malware infections, unauthorized financial transactions, and various forms of cyber fraud. Users may be tricked into granting accessibility permissions that allow the malware to operate in the background and potentially install a VPN, rerouting internet traffic through servers controlled by attackers. Cybersecurity experts advise users to verify the legitimacy of applications before installation and to be cautious of permissions requested by unknown apps.
AppWizard
September 1, 2026
Cybercriminals are targeting Android users with deceptive advertisements for malicious applications disguised as pornographic content on platforms like Facebook and Instagram. The National Cybercrime Threat Analytics Unit (NCTAU) has reported that these ads lead users to phishing traps or malware downloads that can compromise banking credentials. Malicious applications linked to this threat include “Night Play,” “Reloop,” “Kyss,” “Vimo,” “Rivo,” “Nexo,” and “Vixa.” The scam involves promoting these apps through enticing ads, redirecting users to websites offering pornographic content, and prompting them to download APK files directly from these sites, often using “.live” domains. The initial app may request users to download a second package disguised as an update, which can exploit permissions granted to the first app. This malware can gain extensive control over the device, potentially installing a VPN that routes internet traffic through attackers' servers. To protect against this threat, users should download apps only from trusted sources, avoid installing APK files from ads or suspicious links, refrain from granting Accessibility access to unknown apps, regularly review installed apps, keep Google Play Protect enabled, and monitor bank accounts for unusual activity. If a suspicious app cannot be uninstalled, users can try Safe Mode, remove special permissions, or perform a factory reset as a last resort.
Search