malicious application

AppWizard
September 11, 2026
The Cybersecurity and Infrastructure Security Agency (CISA) warned of a critical vulnerability in NetScaler, identified as CVE-2026-19490, with a CVSS score of 9.3, which has been exploited and affects all NetScaler ADC and Gateway appliances. Citrix has patched this vulnerability as of August 19. AdaptHealth reported a data breach affecting over 4.1 million individuals, compromising personal, health, and insurance information, but not Social Security numbers or financial data. A new strain of Android malware, MantaxOtax, attributed to Indonesian threat actors, combines ransomware and spyware, stealing sensitive information and affecting older Android versions. The Gigabud banking trojan has evolved to evade detection by installing a secondary app that hides the malicious application. CISA acting director Nick Andersen emphasized the need for swift adaptation to cybersecurity threats and highlighted staffing improvements within CISA. Russian e-commerce giant Wildberries experienced disruptions from a DDoS attack affecting payments to sellers, following claims of a cyber operation by Ukraine's military intelligence. McKesson faced a cyberattack exposing sensitive data of 6.4 million individuals, with the ShinyHunters group releasing this data after a failed extortion attempt. IDScan confirmed a data breach affecting 150 million individuals, resulting in the theft of personally identifiable information and government-issued documents.
Tech Optimizer
August 17, 2026
The landscape of mobile security has shifted away from traditional third-party antivirus software, as modern Android devices are equipped with built-in security features. Key components of this security framework include Google Play Protect, which blocked 27 million malicious apps in 2025; application sandboxing that isolates apps; proactive permissions that enhance user privacy; AI-powered threat detection for sophisticated attacks; and strict sideloading policies to limit risks from off-market malware. Despite these defenses, threats such as social engineering, phishing, malicious push notifications, and unsecured public Wi-Fi remain prevalent, often evading traditional antivirus solutions. However, certain scenarios, such as frequent sideloading, using older devices, connecting to public Wi-Fi, or suspected infections, may warrant the use of third-party antivirus apps for additional protection. Overall, the built-in security features of Android provide a strong defense for most users, with user education being crucial for effective smartphone protection.
AppWizard
June 6, 2026
Arabic-speaking users are the target of a new Android spyware called Asin, identified by ESET in early 2025. The malware is distributed through fraudulent websites that mimic legitimate services, including: - govlens[.]net, registered on May 27, 2025, impersonating a government news source. - pdf-reader[.]help, registered on May 29, 2025, claiming to be a secure PDF editor. - live-war-map[.]com, registered on January 20, 2025, providing updates on military incidents. Two of these domains are promoted via social media accounts on Facebook and Telegram. The spyware combines legitimate functionality with covert capabilities, and its campaigns may target journalists and OSINT researchers in Arabic-speaking regions. Artifacts linked to Asin include an upload to VirusTotal from TĂĽrkiye in October 2025, an APK downloaded from c-pdf[.]net in December 2025, and a sample disguised as "Syria Defense Map" detected in January 2026. Users must manually install the applications and grant permissions for the spyware to operate.
AppWizard
May 28, 2026
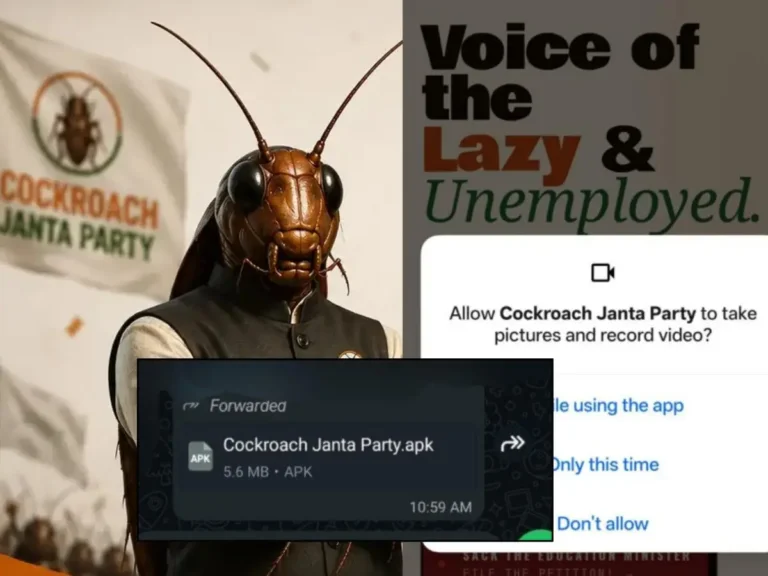
A cybersecurity report released on May 22, 2026, identifies a counterfeit Android application posing as the official app of the Cockroach Janta Party as a significant malware threat. The malicious app, known as Cockroach.Janta.Party, functions as a Remote Access Trojan (RAT) and can infiltrate Android devices, steal sensitive information, intercept communications, and control infected smartphones. The genuine Cockroach Janta Party has no affiliation with this app and is a victim of brand impersonation. The app is distributed through WhatsApp, Telegram, and misleading websites, particularly a rogue domain, cockroachjantaparty[.]org. It targets Android devices running versions 8.0 to 14 and requests elevated permissions, including access to camera, SMS, call logs, and contacts, while misusing the Android Accessibility Service to read on-screen content and grant itself additional permissions. The app contains multiple malicious modules for data exfiltration and uses a Command and Control infrastructure based on the Telegram Bot API. Users are advised to uninstall the app, disable Accessibility permissions, reset banking credentials, enable two-factor authentication, and conduct a full mobile security scan. The legitimate Cockroach Janta Party is encouraged to issue a formal clarification regarding the impersonation.
AppWizard
December 18, 2025
A new Android malware campaign has been launched by the North Korean threat actor Kimsuky, introducing a variant called DocSwap. This malware is distributed via QR codes on phishing websites that impersonate CJ Logistics. Attackers use QR codes and notification pop-ups to lure victims into downloading the malware, which decrypts an embedded APK and activates Remote Access Trojan (RAT) capabilities. The malicious app is disguised as a legitimate application to bypass Android's security measures. Victims are tricked into installing the app through smishing texts or phishing emails that mimic delivery companies. The app downloads an APK named "SecDelivery.apk," which then loads the malware. It requests permissions to access various device functions and registers a service that simulates an OTP authentication screen. The app connects to an attacker-controlled server, allowing execution of commands such as logging keystrokes, capturing audio, and gathering sensitive information. Additionally, two other malicious samples have been identified, disguised as a P2B Airdrop app and a trojanized version of the BYCOM VPN app. The campaign also includes phishing sites mimicking popular South Korean platforms to capture user credentials.
Winsage
October 22, 2025
The United States’ Cybersecurity and Infrastructure Security Agency (CISA) has issued an alert about a critical security vulnerability in the Windows SMB protocol, identified as CVE-2025-33073, which allows attackers to escalate their privileges to SYSTEM level. All versions of Windows Server, Windows 10, and Windows 11 up to version 24H2 are affected. Microsoft addressed this issue in June 2025 during its Patch Tuesday updates. The vulnerability arises from inadequate access control, enabling authenticated attackers to elevate their privileges by deceiving victims into connecting to a malicious server. Information about this vulnerability was public at the time of the patch, but Microsoft has not confirmed any active exploitation. CISA has mandated that U.S. federal agencies must secure their systems by November 10 and encourages the private sector to address the vulnerability as well. Organizations should prioritize installing the June 2025 security updates.
Search