As of September 30, Google has introduced a 24-hour waiting period for Android users in Brazil, Indonesia, Singapore, and Thailand before they can install applications from unregistered developers. This initiative aims to enhance security against potential scams. Users can still access apps from recognized stores, including Google Play and various manufacturer-specific app markets. The rollout is currently limited to the specified countries and has not been implemented globally. The new verification process may affect users who prefer alternative app stores and those who do not use a Google account.
A research team from Turkey, led by Erdal Başaran and Ömer Okucu of Ağrı İbrahim Çeçen University, along with Yusuf Alaca from Hitit University, has developed an innovative detection framework for Android malware that utilizes a visual approach. This framework transforms key features of Android applications into images, allowing a Vision Transformer to differentiate between benign software and malware. The researchers created two types of images from static and dynamic analysis features: a conventional 2D grayscale image and a QR code image. Separate Vision Transformer models were trained on each image type, and spatial pooling features were extracted from deeper layers to create a comprehensive representation of application behavior.
To refine the fused feature vector, Recursive Feature Elimination (RFE) was employed, enhancing classification clarity and reducing computational load. The final classification utilized a majority-voting ensemble strategy, achieving a detection accuracy of 98.72 percent, surpassing standalone models. The study demonstrates that the multimodal system outperforms individual grayscale or QR code pathways. The dataset used is publicly available, promoting reproducibility. The framework's reliance on static and dynamic analysis features allows it to adapt to new threats, and the novel QR code representation offers distinctive visual signatures of malicious behavior. However, challenges remain regarding feature extraction quality and computational demands.
Researchers from Bitdefender have discovered that thousands of inexpensive Android devices are preloaded with malware called "Midnight Mimosa," which generates fraudulent advertising revenue. This malware is embedded in the device firmware before the first power-up, making it impossible for users to uninstall. It operates with system-level privileges, allowing it to install or remove applications without user consent and to download additional code. The malware primarily aims for financial gain through advertising and click fraud, while also gathering information about devices.
Bitdefender has detected this malware on thousands of devices across over 150 countries, with the highest concentrations in Mexico, France, and Italy, followed by the United States, Germany, Brazil, and Spain. Many affected devices are low-cost, white-label, or counterfeit models, often sold online. The malware stealthily installs legitimate-looking applications that display ads in invisible windows, generating ad impressions without user awareness. Bitdefender identified at least 32 disguised applications and found 13 apps in the Google Play Store with similar ad-fraud code.
The source of the malware remains unidentified, but some affected firmware was signed with certificates from Shenzhen Zediel, a Chinese company. The researchers suggest that the malware could have been introduced at various stages of the supply chain, potentially by manufacturers or intermediaries.
Purchasing antivirus software is often seen as necessary but can be frustrating, especially with built-in security features available on most computers. Windows includes Microsoft Defender Antivirus, which has been independently tested and scored well for protection, performance, and usability. Mac users have XProtect for malware detection. Users should verify that their existing protection is enabled and up-to-date before considering a subscription. Antivirus programs combat various types of malware, using methods like signature scanning and heuristic analysis, but they are not infallible. Research on antivirus effectiveness varies, with scores reflecting different criteria and not universally applicable detection rates. Subscriptions may be worthwhile if they offer specific features, but users should be cautious about renewal prices and unnecessary multiple installations. Maintaining updated software and practicing good security habits are essential for protection. For everyday use, built-in protection is often sufficient unless additional benefits justify the cost of extra software.
Google has implemented new developer verification requirements for Android app installations, effective September 30, focusing initially on Brazil, Indonesia, Singapore, and Thailand for certified devices running Android 7 or later. Apps must be linked to verified developers, and users can install apps from these developers without extra steps. However, downloading apps from unverified sources will require a new protocol called the Advanced Flow, which includes enabling settings in Developer options and a mandatory 24-hour waiting period before installation. These measures aim to enhance security against malicious software while still allowing sideloading. Google plans to expand these verification measures globally by 2027, while maintaining an open ecosystem for app distribution.
Microsoft has warned Windows users about a cyber threat that disguises itself as a CAPTCHA test, where cybercriminals use fraudulent verification pages to trick users into executing commands that can install malware. This tactic involves users being directed to a compromised website that presents a fake verification window, prompting them to copy text and execute it in the Windows Run dialog. This method allows attackers to bypass antivirus software by pre-loading malicious scripts disguised as harmless images in the browser's cache. Once activated, the malware collects system information, steals data, and maintains long-term control over the system. Microsoft recommends using robust security software and being aware that no legitimate service will ask users to copy and paste commands into system dialogs.
Antivirus software prevents malicious software from infiltrating devices. A VPN encrypts internet traffic, providing privacy, especially on public Wi-Fi. Scam protection tools use AI to scan for signs of fraud in texts, emails, and videos. McAfee offers bundled security plans that include antivirus, VPN, and scam protection, with higher tiers providing features like Personal Data Cleanup, credit monitoring, and identity-theft protection.
Users can save over 0 in the first year by consolidating security subscriptions. Antivirus software typically costs to 0 annually, standalone scam protection apps range from to per year, and VPN access costs between to 0 annually. McAfee’s Basic plan is available for .99 for the first year for one device, while the Essential plan covers up to five devices for an additional fee.
McAfee’s plans include different features based on tiers:
- Basic: Covers one device with essential security tools.
- Essential: Covers up to five devices with core security tools.
- Premium: Unlimited devices with personal info scans.
- Advanced: Unlimited devices with personal info removal and identity restoration.
- Ultimate: Unlimited devices with extensive financial monitoring and identity-theft coverage.
Setting up McAfee involves downloading the app, creating an account, following setup instructions, turning on the Scam Detector, configuring the VPN, and adding other devices. McAfee plans include unlimited VPN data and support multiple operating systems under a single subscription. McAfee's Scam Detector has an accuracy of over 99% and works on both iPhone and Android.
Endpoint security is a suite of technologies and processes designed to protect devices connected to a business network from cyber threats. It includes various devices such as laptops, smartphones, tablets, servers, and IoT devices. Endpoint security employs a multi-layered approach, scanning for malware, regulating applications, and monitoring device activity for unusual behavior. It is distinct from antivirus software, encompassing a broader range of protective measures, including firewalls, encryption, application controls, patch management, and Endpoint Detection and Response (EDR). The rise of remote work and the increasing number of devices create a larger attack surface, making endpoint security essential for preventing breaches and safeguarding business operations.
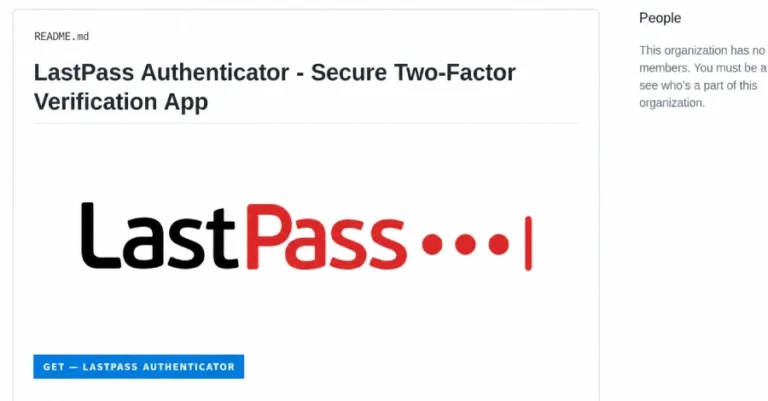
On September 17, researchers from LastPass and Delphos Labs discovered a counterfeit LastPass Authenticator installer on GitHub that installs a malicious Windows kernel driver designed to disable antivirus and steal passwords. The driver, named Alinubx.sys, was signed through Microsoft's hardware compatibility program and initially scored zero detections on VirusTotal. The fake installer is hosted on a fraudulent GitHub page that mimics a legitimate LastPass product page. When executed, the installer uses DLL side-loading to gain SYSTEM-level access and terminates security processes, allowing it to harvest saved passwords from various browsers and applications. The driver is a renamed variant of a known malicious driver, evading detection due to its new file hash. Delphos reported the driver to Microsoft, but it was not considered a security vulnerability. Users who executed the fake installer should treat their passwords and sensitive data as compromised and change them from a secure device. The malicious server has been linked to impersonation pages for multiple brands, and the loader was likely created using a specific crypter tool.
Avast Free Antivirus is recognized as the best free antivirus solution for Windows in 2026, achieving a perfect score from AV-TEST. It operates on the same engine as paid versions, providing comprehensive protection. Other notable free antivirus options include Bitdefender Antivirus Free, which is efficient for older systems; Microsoft Defender, a built-in option with solid protection; AVG AntiVirus Free, suited for older hardware; Avira Free Security, which includes additional tools; and Malwarebytes Free, best for cleaning infections. Each product generates revenue through upselling or data collection. Avast scored 99.78% in detection tests, while Bitdefender achieved 97.6%, and Microsoft Defender reached 99.93%. AVG matched Avast with a 99.97% protection rate, and Avira recorded 99.96%. Malwarebytes had a detection rate of 99.57%. Kaspersky is noted as a product to avoid due to misleading trial offers.