malware

Tech Optimizer
September 15, 2026
Iranian state-sponsored hackers are targeting dissidents, activists, and journalists using deceptive tactics, including malicious applications that impersonate reputable cybersecurity products like Norton Antivirus and KeePass. The FBI and UK authorities issued a warning about these hackers, who establish rapport with targets via social messaging platforms, posing as IT support or known contacts. They convince victims to download files that appear authentic, including AI video creation applications and other software. The spyware, named “Chosen Brick,” infects Windows PCs and has capabilities such as capturing screen content, recording audio, collecting message data, and downloading additional malware. The hackers have exploited this spyware to publish personal details of victims, increasing their harassment. The FBI advises potential victims on detecting the spyware and recommends enabling antivirus software, running regular scans, and avoiding unofficial downloads.
Winsage
September 15, 2026
Iranian state cyber actors are targeting individuals through popular messaging applications, using surveillance and data-stealing malware known as "Chosen Brick," which has been in use since at least 2025. This malware is designed for Windows systems and enables the theft of personal data, allowing Iranian spies to monitor perceived threats such as dissidents, activists, and journalists. The attacks typically begin with messages sent via WhatsApp or Telegram, impersonating trusted contacts. Attackers conduct extensive research on their targets to craft convincing messages that encourage victims to download malicious files disguised as legitimate applications. Once executed, Chosen Brick operates stealthily, evading detection and establishing a connection for command-and-control communications. It can enumerate processes, capture screen and audio content, extract sensitive information, and even wipe infected systems. Organizations suspecting compromise are advised to engage IT providers for investigations and to inform staff about potential risks. Recent alerts follow cyberattacks on water and energy sectors linked to Iran, with ongoing concerns about the implications for cybersecurity amid escalating military tensions. Additionally, five US agencies have reported that attackers are using AI-generated scripts to exploit vulnerabilities in critical infrastructure systems.
AppWizard
September 15, 2026
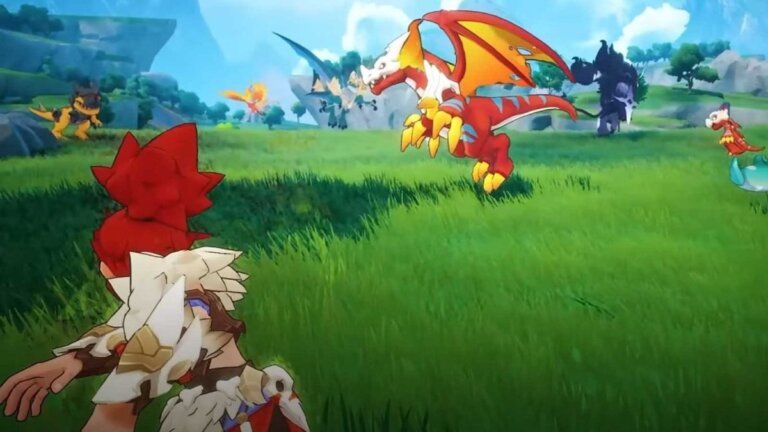
GAMINGbible highlights a new free RPG called Adventurers Guild, developed by AG Studio, which features a whimsical fantasy world and gameplay elements reminiscent of popular franchises. However, the game has been criticized for not matching the vibrant visuals shown in its trailer, with players expressing skepticism about its authenticity. The Steam listing includes a personal email for customer service, raising further concerns. Reviews warn of potential scams, false advertising, and misleading marketing tactics, advising caution when considering the game. There is currently no evidence of malware, but players are urged to be vigilant.
Winsage
September 15, 2026
A spear-phishing campaign linked to the Chinese threat actor UTA0560 targeted various NGOs on September 1, 2026, exploiting recently patched vulnerabilities in Google Chrome and Microsoft Windows. The campaign utilized a malicious JavaScript backdoor called GRIMWEDGE, which was deployed through a multi-stage exploit chain that involved three vulnerabilities: CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880. The attack began with spear-phishing emails that led recipients to a vulnerable U.S.-based university website, allowing attackers to redirect users to their infrastructure. The exploit chain enabled arbitrary code execution and facilitated the deployment of GRIMWEDGE, which is capable of host reconnaissance, file and process management, command execution, and payload delivery. The initial payload was an executable named "msgbox.exe," which extracted a legitimate Windows binary and a malicious DLL called "wsc.dll." This DLL initiated a sideloading chain and contacted a command-and-control server for further instructions. GRIMWEDGE allows for several commands, including system reconnaissance, directory listing, file deletion, and command execution in a hidden window. It lacks built-in persistence or lateral movement mechanisms but provides a foothold for further exploitation. Concurrently, another Chinese threat actor, JungleBamboo (APT31), used the same exploit chain to deploy a loader named SUPERSTOMP, which installs a credential-stealing Chrome extension called LONGTALE. The simultaneous use of the exploit chain by multiple actors suggests potential sharing or sale of the exploit, raising concerns about patch-gap vulnerabilities that pose risks for exploitation campaigns.
AppWizard
September 14, 2026
Malicious Android applications are being promoted through social media advertisements, particularly on platforms like Instagram and Facebook, posing significant risks to users. The Indian Cyber Crime Coordination Centre (I4C) has warned about deceptive apps advertised under names such as Night Play, Reloop, Kyss, Vimo, Rivo, Nezo, and Vixa, which often redirect users to pornographic websites to download APK files. These applications can exploit sensitive device permissions, leading to malware infections, unauthorized financial transactions, and various forms of cyber fraud. Users may be tricked into granting accessibility permissions that allow the malware to operate in the background and potentially install a VPN, rerouting internet traffic through servers controlled by attackers. Cybersecurity experts advise users to verify the legitimacy of applications before installation and to be cautious of permissions requested by unknown apps.
Tech Optimizer
September 12, 2026
If you hold Microsoft 365 E5, you already have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended. CrowdStrike is suitable for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses without IT staff, VIPRE for budget-conscious organizations, and Expel for tool-agnostic managed detection and response. It is essential to assess your organization's current situation honestly when evaluating endpoint protection options. Antivirus and EDR are now essentially the same agent, and organizations should inquire about update staging processes and review independent tests for protection rates. Coverage for servers and Linux environments is often overlooked but crucial, as Linux servers are prime targets for ransomware. Key recommendations include: - Microsoft Defender for Endpoint for organizations already on Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a well-funded security operations function. - SentinelOne for mid-sized organizations needing autonomous operation. - ESET for organizations with older hardware or virtual desktop infrastructure. - Avast Business for micro and small businesses. - VIPRE for budget-conscious organizations. - Expel for those seeking managed detection across various environments. During deployment, avoid running two real-time agents simultaneously, ensure prevention features are activated, and test on line-of-business applications first. Verify update staging and rollback procedures with vendors, and confirm whether Microsoft licensing covers your needs to avoid unnecessary purchases.
Search