The Messaging Trends Report 2026 indicates a 19 percent increase in messaging activity in the Philippines for 2025, with mobile messaging applications experiencing a 139 percent rise in interactions. The report analyzed 628 billion mobile interactions on Infobip’s platform and included a 20-year review of 3.8 trillion messages. Viber interactions grew by 47 percent, WhatsApp by 1,416 percent, SMS by 14 percent, MMS by 15 percent, and email by 5 percent. Other chat applications saw a 1,014 percent increase in user engagement.
Google Photos is set to release version 7.93.0, which will enhance album-sharing by allowing users to copy and download QR codes directly, eliminating the need for screenshots. The update will include buttons labeled "Copy" and "Download" below the QR code for easier sharing. Additionally, an updated Collections tab will allow users to pin items and reorder folders, with a new bottom sheet to improve organization and accessibility. The timeline for the QR code update is uncertain, but the revamped Collections tab is expected to launch soon.
Iranian state cyber actors are targeting individuals through popular messaging applications, using surveillance and data-stealing malware known as "Chosen Brick," which has been in use since at least 2025. This malware is designed for Windows systems and enables the theft of personal data, allowing Iranian spies to monitor perceived threats such as dissidents, activists, and journalists. The attacks typically begin with messages sent via WhatsApp or Telegram, impersonating trusted contacts. Attackers conduct extensive research on their targets to craft convincing messages that encourage victims to download malicious files disguised as legitimate applications.
Once executed, Chosen Brick operates stealthily, evading detection and establishing a connection for command-and-control communications. It can enumerate processes, capture screen and audio content, extract sensitive information, and even wipe infected systems. Organizations suspecting compromise are advised to engage IT providers for investigations and to inform staff about potential risks. Recent alerts follow cyberattacks on water and energy sectors linked to Iran, with ongoing concerns about the implications for cybersecurity amid escalating military tensions. Additionally, five US agencies have reported that attackers are using AI-generated scripts to exploit vulnerabilities in critical infrastructure systems.
A bug in SMS and RCS messaging for Android users causes old messages to be appended when sending new communications, leading to potential data privacy concerns as sensitive information may be shared with unintended recipients. The issue affects a broad range of devices and manufacturers, and Google is working on a gradual fix that may take several weeks to implement. Users are advised to consider alternative messaging platforms to mitigate risks.
Security agencies in India have observed a shift in the tactics of terrorist groups, which are now using pornography websites and niche encrypted applications for communication instead of traditional social media. These groups, often collaborating with Pakistan's ISI, utilize platforms with real-time chat tools disguised as dating services to send instructions to recruits in Jammu and Kashmir. Security agencies are monitoring various digital tools, including Tor-based applications like Coatex and Conion, which obscure user identities. Some privacy-focused platforms do not require phone numbers for registration, complicating tracking efforts. Despite bans on certain pornography applications in India, they are still accessed illegally via VPNs, which mask users' IP addresses. The use of the Tor network presents additional tracking challenges, as it obscures data origins and destinations. Security agencies are adapting their surveillance methods in response to these developments, which include the use of virtual SIM cards in terrorist activities, as highlighted during investigations into the 2019 Pulwama attack.
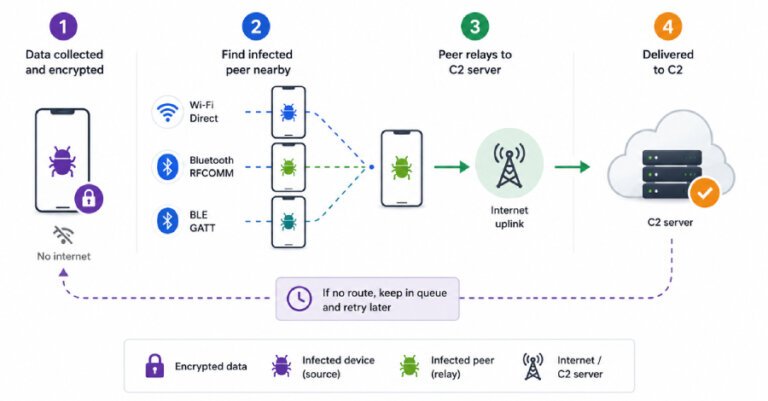
A new Android malware threat, codenamed Manic, poses significant risks to Ukrainian banks, government services, and messaging applications, with a reach extending to Russian and European financial institutions, global fintech platforms, cryptocurrency services, and military communication channels. Manic combines Android banking malware and mobile spyware, targeting sensitive applications and enabling comprehensive device takeover. It features a novel Wi-Fi mesh technique for data relay through compromised devices and utilizes phishing sites and dropper apps. The malware originated in February 2026, with initial development leading to its first deployment by late May. It monitors 169 package IDs related to banks, payment services, and messaging applications, primarily affecting Ukrainian targets but also impacting applications in Russia and Europe. Manic can infiltrate commercial and military messaging apps, track locations, monitor notifications, and collect files. It exploits Android's accessibility services to capture sensitive data and employs a store-and-forward relay mechanism for data exfiltration through nearby compromised devices. Google has stated that no apps containing this malware are found on Google Play, and Android users are protected by Google Play Protect.
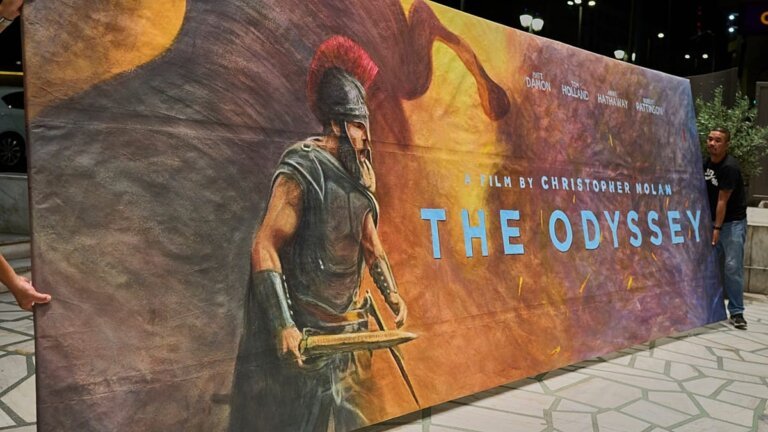
Pirated digital copies of the film "Odyssey" are being used to spread the Lumma Stealer malware, which compromises viewers' computers. Bitdefender's internal data shows that users have attempted to download malicious executable files disguised as the film, which has not yet been released on online platforms. These counterfeit copies are circulating on illegal sites, and the Lumma Stealer malware can steal sensitive information from infected devices. Bitdefender identified several bait file names that are actually executable files designed to infect computers rather than play the film. This tactic follows a trend of using popular films to disseminate malware, with similar campaigns documented in the past. Cybercriminals exploit the gap between a film's theatrical release and its availability on legal streaming platforms. Users are advised to watch films only through verified services and to keep their cybersecurity software updated.
Convos integrates an assistant directly within group chats to provide answers without switching apps. Users can create an identity without a phone number or email, enhancing privacy and simplifying setup. The app features "Little Assistants," specialized agents for tasks, powered by ChatGPT or Claude, allowing them to interact seamlessly in conversations. The messaging interface is similar to popular apps, with a unique "Explode" function for permanent deletion of chats. Convos is designed for privacy-focused users, group planners, and early adopters, though it may not suit those needing a complete contact list or instant responses. The app has a 4.8 rating on the App Store and over 100 downloads on the Play Store.
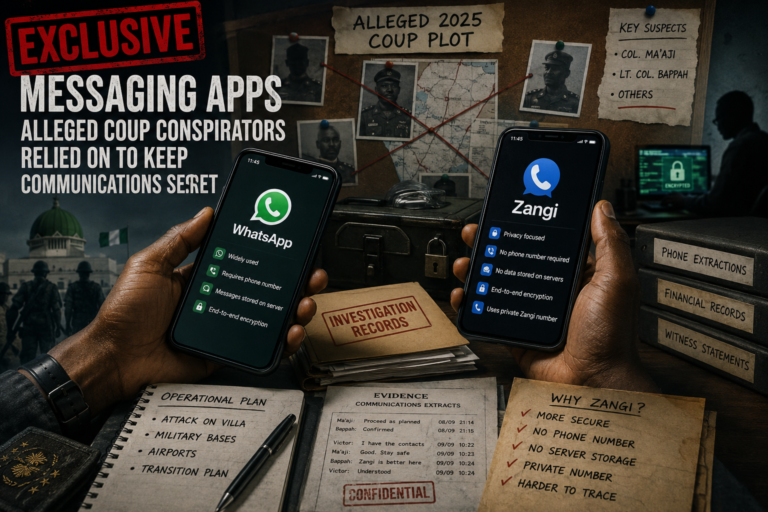
The choice of communication methods, such as WhatsApp and Zangi, influenced the outcome of a clandestine operation related to an alleged coup against President Bola Tinubu's government. Retired navy captain Erasmus Victor, facing treason charges, mentioned being recruited to find financial backers for the coup by Colonel Mohammed Ma’aji, who introduced him to Zangi for its security features. Zangi claims it does not store communication histories and uses end-to-end encryption, but investigators may still access data on users' devices. The investigation includes evidence from devices rather than relying solely on messaging companies. Mr. Victor and his co-defendants have denied wrongdoing and are challenging the admissibility of their statements in court.
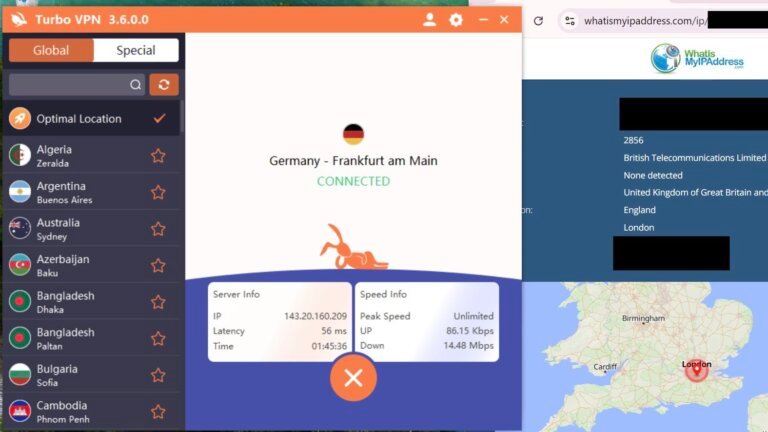
Turbo VPN's Windows client has faced significant privacy issues, including active IP leaks and misconfigured protocols. Owned by Innovative Connecting Pte. Limited in Singapore, it has over 500 million downloads on Android. Initial testing revealed that version 3.6.0.0 did not resolve IPv6 address leaks, despite IPv4 addresses being masked. A subsequent update, version 3.7.0.0, successfully blocked unencrypted IPv6 traffic while maintaining IPv4 masking. Testing showed that the proprietary protocol Lepus functions differently from standard VPNs, routing non-browser data through a local proxy without encryption. Turbo VPN's response indicated that the observed issues were limited to specific network configurations, and they have since implemented improvements in the latest version. However, detailed information about their proprietary protocols remains unavailable.