Microsoft Entra

Winsage
October 8, 2026
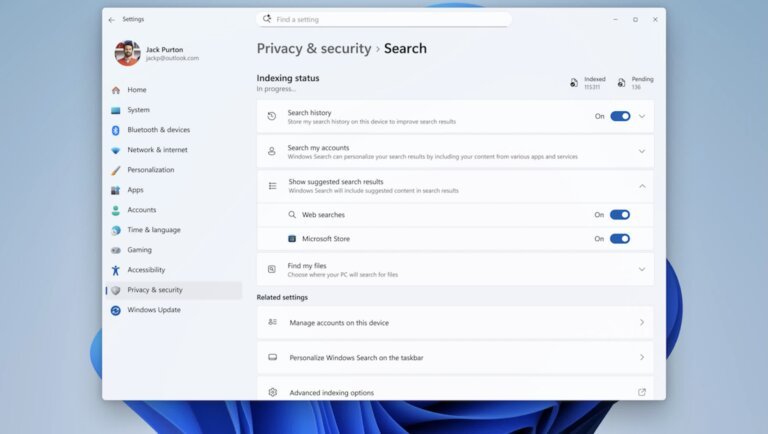
Microsoft is requesting Windows users to grant its Copilot feature access to their files and activities, following a previous retraction of a similar AI integration due to scrutiny. Copilot can analyze content on the device with user consent, performing tasks like organizing files and troubleshooting, using both local AI models and cloud processing. Microsoft has implemented safeguards, but its security team has raised concerns about potential risks associated with powerful features. The opt-in nature of Copilot places accountability on Microsoft, as users must actively grant access. Hybrid features are set to roll out in the coming months, with taskbar search actions already reaching Windows Insiders. Over 40 percent of new business laptops are being designed as Copilot+ PCs, with the Surface Laptop Ultra scheduled for release on October 16.
Winsage
October 8, 2026
Microsoft is inviting Windows users to grant its Copilot feature access to their files and activities, with user consent. The new iteration of Copilot can understand content on the device, perform tasks like organizing files, troubleshooting, and writing code, with some tasks processed in the cloud. Activation is opt-in, folder access is limited, and Copilot operates under separate accounts from users. Microsoft has implemented safeguards, including Microsoft Execution Containers to define agent access. However, internal warnings from Microsoft's security team highlight potential risks associated with agents capable of modifying environments. Features for enhancing auditability of agent activities are under development. Microsoft previously faced criticism for its Recall feature, which raised security concerns. The opt-in design places accountability on Microsoft, as users must grant access. The hybrid features require a Copilot+ PC and are set to roll out in the coming months, with taskbar search actions already reaching Windows Insiders. Over 40 percent of newly manufactured business laptops are Copilot+ PCs, with the Surface Laptop Ultra launching on October 16.
Winsage
October 1, 2026
Microsoft has updated its Windows settings backup and restore functionality, now automatically enabled for all enterprise systems joined to Microsoft Entra or operating in a hybrid environment after upgrading to Windows 11 version 26H2. The backup tool, previously known as Windows Backup for Organizations, is designed to facilitate the backup and restoration of essential Windows settings for enterprise users during device resets, replacements, upgrades, or reimaging. Originally introduced in November 2024, it became generally available by August 2025. The backup policy will be activated by default for eligible devices following the release of Windows 11, version 26H2 on September 29, 2025, unless administrators have previously configured the policy. The automatic backup feature applies to devices running Windows 11 26H2 in regions not governed by the EU Digital Markets Act and does not require explicit admin configuration for restoring Windows devices. IT administrators can control the backup policy through mobile device management solutions like Microsoft Intune or Group Policy.
Winsage
September 24, 2026
Microsoft has informed IT administrators about potential connection challenges with the Always On VPN after the September 2026 Windows 11 security updates. Users may face difficulties connecting to their organization's network, particularly if the VPN is set to automatically attempt an alternative connection method upon failure. Symptoms include connections remaining in a 'Connecting' state or displaying the error message: 'The specified port is already in use.' Affected versions include Windows 11, version 26H1 (KB5124012), version 25H2 (KB5124008), and version 24H2 (KB5124008). A temporary workaround involves adjusting the Always On VPN profile from automatic protocol selection to a single protocol (SSTP or IKEv2). Microsoft is also addressing various other issues related to Hyper-V, Remote Desktop Services, USB audio, and the File History backup feature.
Winsage
September 9, 2026
Microsoft's September 2026 security update revealed 973 vulnerabilities, with 113 classified as critical. Two actively exploited vulnerabilities are CVE-2026-81963 (Windows Update Stack, elevation of privilege, CVSS 7.8) and CVE-2026-85880 (Windows ALPC, elevation of privilege, CVSS 7.8). Among the 113 critical vulnerabilities, 82 are remote code execution (RCE) vulnerabilities. Notable vulnerabilities include: - CVE-2026-69676: RCE in Windows Kerberos, CVSS 8.8, authentication bypass. - CVE-2026-69852: RCE in Windows RRAS, CVSS 7.5, heap-based buffer overflow. - CVE-2026-72957: RCE in Windows Deployment Services, CVSS 7.8. - CVE-2026-69854: Elevation of privilege in Spring Cloud Azure, CVSS 9.0, improper authentication. - CVE-2026-83501: Information disclosure in Windows VBS, CVSS 5.5. - CVE-2026-69730: RCE in Windows DNS Server, CVSS 9.8. Less likely to be exploited vulnerabilities include: - CVE-2026-69845: RCE in Windows DHCP Server, CVSS 9.8, heap-based buffer overflow. - CVE-2026-65772: Vulnerability in Microsoft Dynamics 365 On-Premises, CVSS 8.8, deserialization of untrusted data. - CVE-2026-66302: RCE in Skype for Business, CVSS 9.8. Additional critical vulnerabilities include: - CVE-2026-62916: Elevation of privilege in Microsoft Entra ID, CVSS 9.1. - CVE-2026-83941: Elevation of privilege in Entra ID, CVSS 9.9. - CVE-2026-80098: Vulnerability in Copilot Studio, CVSS 9.3, improper verification of cryptographic signatures. Talos is releasing a new Snort ruleset to detect attempts to exploit these vulnerabilities, with specific SIDs for Snort 2 and Snort 3 rule coverage.
Search