Microsoft

Tech Optimizer
September 23, 2026
A new tool named BigDiskBuster has been released on GitHub, which disrupts Microsoft Defender Antivirus by preventing it from installing updates. It does this by consuming available disk space during the update process, causing Defender to remain on its current version and unable to receive new platform or signature updates. BigDiskBuster operates as a local denial-of-service technique and requires prior access to the target machine to execute. The tool was created by researcher Abdelhamid Naceri, known as Nightmare Eclipse, who has previously worked on similar projects. As of now, there is no CVE identifier, patch, or advisory from Microsoft regarding this issue.
AppWizard
September 23, 2026
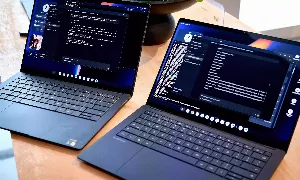
On September 22, 2026, Google introduced the Googlebook, a laptop built on a shared Android foundation, designed to combine the convenience of mobile devices with the power of traditional laptops. Collaborating with manufacturers like HP, Dell, Lenovo, Acer, and Asus, the Googlebook features high-resolution OLED touchscreens, precise trackpads, dedicated keyboards, and boasts a 14-hour battery life. It operates on either Intel’s Core Ultra Series 3 processors or Qualcomm’s Snapdragon X chips, with initial shipping in the U.S. set for October 4, 2026, followed by launches in the UK, France, and Australia on October 5. The Googlebook can run Android applications natively, enhancing multi-tasking capabilities, and developers are encouraged to optimize their apps for the device using Google's Adaptive Development framework. Google plans to provide a decade of software updates for the Googlebook operating system.
Winsage
September 23, 2026
Security researcher Abdelhamid Naceri, known as Nightmare Eclipse, released a zero-day exploit called BigDiskBuster that targets Microsoft Defender, preventing antivirus updates and leaving systems vulnerable. BigDiskBuster operates across all supported Windows versions and must run in the background to block updates. Naceri has previously released a similar exploit called UnDefend and has a history of releasing multiple zero-day exploits since April 2026 amid a dispute with Microsoft. Two weeks before BigDiskBuster, he introduced another exploit named ShieldCrash, which grants SYSTEM access and circumvents a patched flaw. Naceri's recent exploits include tools like LegacyHive, BlueHammer, RedSun, YellowKey, GreenPlasma, and MiniPlasma, all targeting Microsoft Defender and other Windows components. Microsoft has warned of potential legal action against malicious activities but has not commented on BigDiskBuster.
Winsage
September 22, 2026
Users frequently express frustration with Windows updates due to unexpected restarts and frequent breakdowns, leading to a perception of being beta testers for Microsoft. Problems often arise with updates, including significant disruptions from routine maintenance updates. Recent issues included difficulties with the Windows Subsystem for Linux and copy-paste functionality in Microsoft Excel. In July, Microsoft paused an update due to unexpected shutdowns on some Dell PCs. Users are increasingly adopting a wait-and-see approach before installing updates, utilizing Windows 11's ability to pause updates for several weeks. Historically, Windows lacked robust update management, but recent changes have extended the pause period. There is a significant concern regarding the limited control users have over updates and the need for improved quality control from Microsoft.
Tech Optimizer
September 22, 2026
LastPass has identified a sophisticated scheme targeting users of its Authenticator app, involving SEO poisoning and deceptive GitHub pages that distribute malicious ZIP files disguised as legitimate software. Users searching for "LastPass Authenticator download" may encounter these counterfeit pages, which redirect them to a malicious server delivering a ZIP file containing vsdbg.exe and vsdbg.dll. The executable is a legitimate Microsoft debugging tool exploited to execute the malicious DLL through DLL sideloading, allowing the malware to run undetected. Named Rapuncel by security researchers from Delphos, this malware is undetectable by antivirus engines and targets a hardcoded list of 145 antivirus and endpoint security products, disabling them upon detection. Rapuncel harvests sensitive information, including saved passwords from over 25 web browsers, cryptocurrency wallet files from more than 30 applications, and session tokens from platforms like Discord and Steam. It also captures screenshots and compiles a profile of the infected system, uploading the stolen data to an attacker-controlled server. The malware includes a kernel driver that intercepts web traffic, allowing for advertisement injection and search result manipulation. This campaign has been active for several months, with LastPass vaults remaining unaffected. Users are advised to download applications only from trusted sources. Rapuncel establishes persistence on infected machines by installing itself as a Windows service that starts with the system and terminates activated security products. Removing the kernel driver requires booting into Safe Mode or using external recovery tools, as standard Windows utilities cannot eliminate software operating at that level.
Winsage
September 22, 2026
Changing the desktop wallpaper to a solid color in Windows 7 caused a 30-second delay on the Welcome screen after entering a password. This issue arose because the system waited for a signal from the wallpaper component, which only sent its "I'm ready" signal when an image file was used. When a solid color was selected, this signal was not sent, leading to unnecessary waiting. The problem was acknowledged by Microsoft for both Windows 7 and Windows Server 2008 R2, and it was resolved with a Hotfix update in November 2009. Users found workarounds, such as switching to an image or creating a small solid-color image, to eliminate the delay.
Search