mitigation

Winsage
September 26, 2026
Microsoft has acknowledged that some users may experience desktop loading issues, specifically black screens, after installing the August 2026 preview updates and subsequent releases. This problem mainly affects Azure Virtual Desktop (AVD) hosts using FSLogix. Symptoms include a black screen post-sign-in and crashes related to Windows Explorer, which can be temporarily resolved by manually launching Windows Explorer through Task Manager. For enterprise customers, Microsoft has introduced a mitigation strategy via Known Issue Rollback (KIR), allowing IT administrators to reverse problematic updates by applying specific group policies. Additionally, Microsoft has addressed issues related to the loss of mouse and desktop settings on certain Windows 11 systems caused by the KB5120998 update.
Tech Optimizer
September 23, 2026
A new tool named BigDiskBuster has been released on GitHub, which disrupts Microsoft Defender Antivirus by preventing it from installing updates. It does this by consuming available disk space during the update process, causing Defender to remain on its current version and unable to receive new platform or signature updates. BigDiskBuster operates as a local denial-of-service technique and requires prior access to the target machine to execute. The tool was created by researcher Abdelhamid Naceri, known as Nightmare Eclipse, who has previously worked on similar projects. As of now, there is no CVE identifier, patch, or advisory from Microsoft regarding this issue.
Winsage
September 10, 2026
Microsoft's Patch Tuesday on September 8, 2026, addressed two critical Windows privilege escalation vulnerabilities: CVE-2026-85880 and CVE-2026-81963, both with a CVSS score of 7.8. CVE-2026-85880 is a heap-based buffer overflow in the Windows Advanced Local Procedure Call (ALPC), allowing attackers with low-privilege local access to escalate privileges to SYSTEM. CVE-2026-81963 involves improper link resolution in the Windows Update Stack, enabling similar privilege escalation. Both vulnerabilities require no user interaction and have been actively exploited prior to the patch release. CISA added them to its Known Exploited Vulnerabilities catalog on September 8, 2026, with a remediation deadline of September 22 for U.S. federal agencies. CVE-2026-85880 affects various Windows 10 and Server versions but excludes Windows 11 and Windows Server 2025. CVE-2026-81963 impacts newer Windows platforms, including Windows 11 and Windows Server 2025. Microsoft released security updates for both vulnerabilities on September 8, 2026, and organizations are advised to prioritize these updates. Security teams should monitor for signs of privilege escalation and unusual SYSTEM-level activities related to these vulnerabilities.
Winsage
September 4, 2026
Microsoft is addressing an issue (TM1466820) causing delays or preventing some users from accessing the Microsoft Teams desktop client on Windows systems, acknowledged on Thursday at 16:45 EDT. Affected users may experience loading failures or delays of up to two minutes and are advised to use the web or mobile versions of Teams as a temporary workaround. Microsoft is analyzing service logs and telemetry data to identify the root cause and has contacted some affected users for more information. Additionally, there is a separate issue (TM1466659) affecting Mac users, preventing them from joining Teams calls and meetings, confirmed on Sunday at 08:32 EDT. Microsoft is reassessing the cause of this disruption. Earlier this year, Microsoft resolved an issue blocking some Teams Free users from chats and calls. The company also confirmed a bug causing crashes and launch failures for Teams and New Outlook users after recent Windows security updates. Furthermore, there is an ongoing Exchange Online issue affecting multiple mailboxes, resulting in "Server busy" errors and delays in email communications with external domains.
Winsage
September 4, 2026
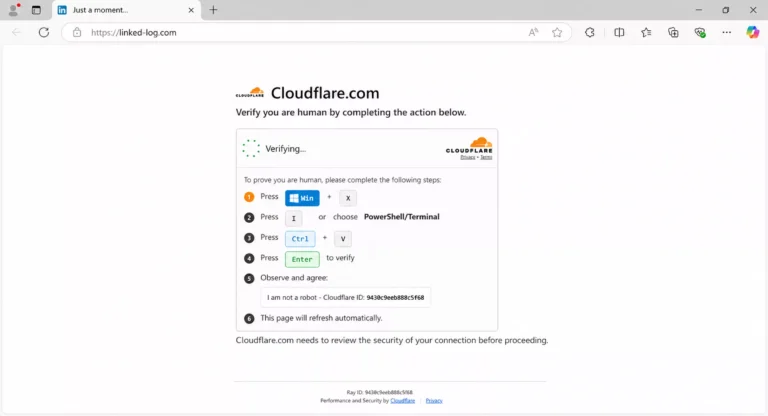
Microsoft has identified a new malware campaign called TerminalFix that uses fake CAPTCHA prompts to trick Windows users into executing malicious commands. This campaign is a variation of ClickFix attacks and employs deceptive pages that impersonate reputable services like Cloudflare. Instead of traditional CAPTCHA challenges, users are instructed to open PowerShell or Command Prompt and paste in commands, allowing attackers to execute complex scripts more easily. TerminalFix initiates a multi-stage intrusion, granting attackers persistent proxy access to the infected machine, which can lead to further exploitation of the company's network. The campaign relies on social engineering tactics, requiring user compliance with counterfeit verification instructions. Microsoft has released mitigation guidance, recommending restrictions on PowerShell access, monitoring for DLL sideloading, blocking outdated Flash plugins, and enabling cloud-delivered protection in Microsoft Defender Antivirus. The campaign poses significant risks to enterprise networks, but individual users should also be cautious about executing commands requested by websites.
Winsage
September 1, 2026
Microsoft Threat Intelligence has identified a new variant of the ClickFix malware campaign called "TerminalFix." This variant uses deceptive CAPTCHAs that mimic trusted services like Cloudflare and directs users to PowerShell or a command prompt, allowing for the execution of complex scripts. TerminalFix aims to orchestrate a multi-stage attack that provides attackers with persistent, network-level proxy access through the compromised host, potentially leading to significant data theft and malware propagation within unsecured enterprise networks. Recommendations for defense against TerminalFix include restricting access to PowerShell and Windows Run dialogs, monitoring for DLL sideloading indicators, blocking Flash plugins, and enabling cloud-delivered protection in Microsoft Defender Antivirus. The attacks primarily target enterprise environments rather than individual consumers.
Winsage
August 24, 2026
Malware researcher Dominik Reichel has discovered a sophisticated Windows backdoor named Sleepwalker, which remains dormant in memory until activated by a specially crafted network packet. Sleepwalker uses a 23-instruction command language to execute tasks, including running code in memory and exfiltrating data. It activates through a proprietary activation packet that does not contain readable commands. The malware targets a VMware VMCI and disguises itself as Microsoft's dpapi.dll, mimicking its functions while redirecting calls to a non-existent file. Once it confirms its host process as ERAAgent.exe, it enters a dormant state to evade detection. Sleepwalker monitors for a specific pattern known as a magic packet to decrypt and interpret commands. Commands sent to it are encrypted with AES-256-CCM and must be read in a specific order. The backdoor includes functionalities for sending and concealing data, receiving tasks, and executing programs. Reichel has developed a toolkit to decode Sleepwalker’s bytecode and a mitigation guide for affected users. However, there are significant gaps in knowledge regarding the initial access method, victim identification, and the malware's operator.
Winsage
August 20, 2026
ShieldBreak, identified as CVE-2026-69414, is a zero-day vulnerability in the Microsoft Malware Protection Engine that allows low-privileged local attackers to escalate privileges to SYSTEM. The public proof of concept was released on August 12, 2026, and Microsoft recognized the CVE on August 14, 2026. No patch is currently available. ShieldBreak exploits an elevation-of-privilege vulnerability by manipulating file processing during the cloud-file hydration process in Microsoft Defender, allowing attackers to control processes with elevated privileges. The exploit is functional on Windows 11 25H2 and Windows Server 2025. Qualys VMDR can detect this vulnerability using a specific query, and organizations can use Qualys TruRisk™ Eliminate for mitigation until a patch is released.
Winsage
August 18, 2026
A new exploit named ShieldBreak, developed by Nightmare-Eclipse, targets Microsoft Defender by allowing privilege escalation and bypassing previous security fixes related to the RoguePlanet vulnerability. ShieldBreak operates on Windows 11 25H2, its Canary channel, and Windows Server 2025, achieving a "100% success rate." Windows 10 may also be vulnerable, but the exploit is specifically designed for Windows 11. There is currently no patch for ShieldBreak, and users are advised to disable Microsoft Defender, implement two-factor authentication, and exercise caution with suspicious online activities. Malwarebytes has recommended its Premium Security antivirus as a temporary solution.
Search