mobile security

AppWizard
September 19, 2026
A new Android malware called RatHat has emerged, analyzed by researchers from Zimperium's zLabs. It spreads through deceptive smishing texts and malicious ads that lead users to counterfeit download pages for popular apps. Once installed, it manipulates Android's Accessibility Service to gain elevated access by enabling Wireless Debugging and retrieving authentication codes without user intervention. RatHat targets finance and banking apps to steal user IDs, passwords, and MFA codes, using techniques to obtain touch coordinates for PIN recovery. It can intercept SMS messages, gain limited control of the device, and reinstall itself. Users are advised against sideloading apps and granting unnecessary accessibility permissions. Google's Advanced Protection Mode and Malwarebytes for Android can help mitigate risks associated with RatHat.

AppWizard
September 19, 2026
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
AppWizard
September 18, 2026
Cybersecurity experts have identified a new Android malware named RatHat, believed to be operated by Chinese threat actors. RatHat is distributed primarily through smishing and malvertising campaigns, leading users to deceptive download portals. It employs an automated multi-stage infection process and exploits Accessibility features along with a local ADB self-pairing mechanism to escape the Android application sandbox. The malware uses various anti-analysis techniques, including container tampering, manifest bombs, DEX bytecode poisoning, and dual string-encryption. RatHat's architecture consists of a malicious Android application, a Go agent, and an FRP reverse-proxy client, which together enable it to gain critical system permissions and perform various malicious activities such as credential capturing, screen recording, and SMS interception. Even if uninstalled, the malware retains shell access to the device, allowing attackers to reinstall it. RatHat can serialize the device's Accessibility tree to XML and communicate with a Generative AI assistant for tasks like screen coordinate determination and text extraction. The Go Agent, masquerading as a native library, exploits shell access to execute commands and establish a persistent connection to a command-and-control server via the FRP client. The C2 server can issue extensive commands to collect sensitive information, including SMS messages, credentials, files, and keystrokes, and RatHat also features a hardware-level keylogger.
BetaBeacon
September 18, 2026
- LDPlayer is a general-purpose performance emulator - MEmu is a multi-instance workhorse for players juggling several accounts - GameLoop is Tencent's first-party tool built almost exclusively around its own mobile titles - LDPlayer, MEmu, and GameLoop are all designed around mobile gaming rather than general Android app testing - LDPlayer is actively patching graphics driver bugs, MEmu is quietly polishing quality-of-life features, and GameLoop's update cadence has slowed - GameLoop is specifically tuned for Tencent-published titles like PUBG Mobile - LDPlayer runs two branches, with LDPlayer 14 being the most actively patched version - MEmu's defining feature is multi-instance management for running multiple Android sessions - MEmu's release cadence has been steady in 2026, with the latest build adding a toggle to disable Android system sounds
AppWizard
September 17, 2026
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures. RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands. The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
Tech Optimizer
September 10, 2026
Bitdefender is recognized for its strong detection capabilities, mid-range pricing, and minimal system impact. Malwarebytes offers a free scanner for cleaning infected Macs, while Intego specializes in macOS with features tailored for Apple users. Norton provides a comprehensive security package with VPN, backup, and identity monitoring features. Gen Digital owns Norton, Avast, AVG, and Avira, indicating that these brands share threat intelligence and engineering resources. The 2026 Mac Antivirus Scorecard ranks Bitdefender highest with a score of 8.8, followed by Intego (8.2), Malwarebytes (8.3), ESET (8.3), and Norton (7.4). Pricing structures often include discounted first-year rates that can double upon renewal. Free options include Avast and Avira with real-time protection, while Malwarebytes offers a free on-demand scanner. Multi-device licensing can provide better value, and business Macs should use business licenses for essential features. macOS has built-in protections like XProtect and Gatekeeper, but third-party antivirus solutions can enhance security against newer threats.
AppWizard
September 7, 2026
The GrapheneOS team is working on a new OS release to fix a volume bar UI regression caused by an upstream Android security preview patch and a UI issue within the Private Space feature. The release of the revamped Messages app has been delayed to follow the upcoming OS release, and there is currently no timeline for the integration of RCS (Rich Communication Services) into the new Messages app. The team is focused on enhancing user privacy and functionality while developing applications and privacy controls to reduce Google's influence.
AppWizard
September 4, 2026
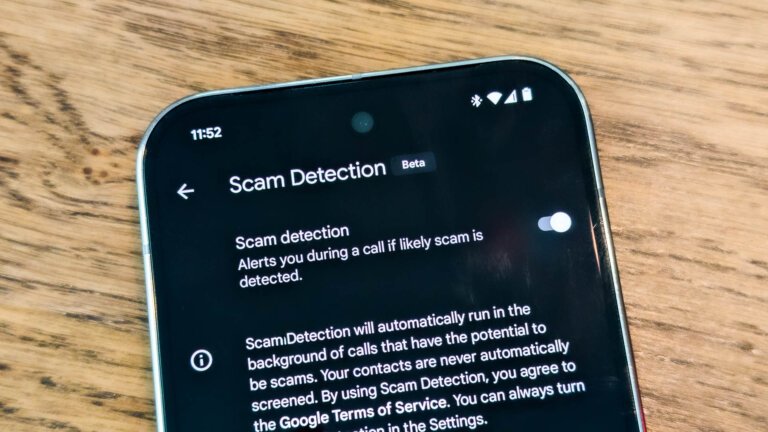
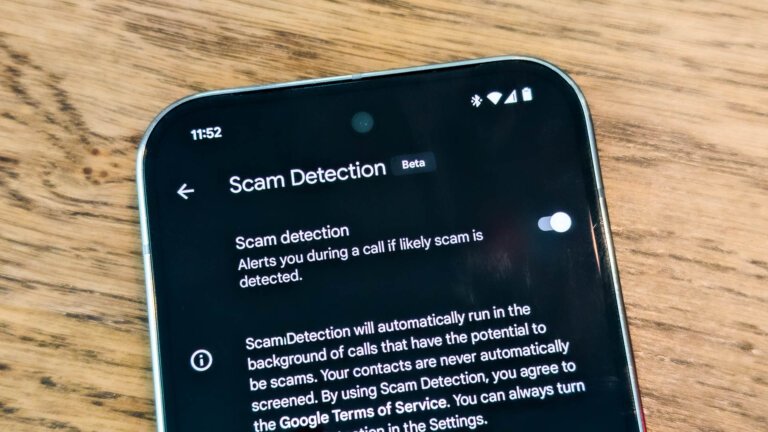
Google's Scam Detection feature, initially available only on Pixel devices, is expanding to more Android smartphones, currently accessible on the Galaxy S26 series and potentially coming to vivo phones. Recent findings from the Google Phone app's public beta indicate that Xiaomi may also support this feature, with the Xiaomi 18 Fold being a possible candidate for the initial rollout, although it is currently confirmed only for release in China. Google's Scam Detection uses on-device AI to analyze incoming calls for potential scams, aiming to enhance user security. The feature is still in beta and may have flaws, but improvements are expected as Google refines the technology.
AppWizard
August 18, 2026
Most Android users consider third-party antivirus apps unnecessary due to the robust built-in security features of modern Android smartphones. However, Android devices are still vulnerable to viruses, malware, and security breaches, with a 2025 Gen threat report indicating a tripling of malicious push notifications and an increase in spyware issues. Google Play Protect blocked 27 million malicious apps in 2025 and conducts scans to manage security. Android employs sandboxing, regular security updates, and an opt-in permissions system to protect users. Upcoming features include phone call spoofing protection and enhanced live threat detection capabilities. Social engineering tactics, such as phishing and fake tech support calls, pose significant risks that antivirus software cannot address. Connecting to open Wi-Fi networks can expose devices to risks, and malicious push notifications can mislead users. Third-party antivirus apps may be beneficial in high-risk scenarios, such as public Wi-Fi networks or when sideloading apps, providing an additional layer of protection.
AppWizard
August 17, 2026
Recent findings indicate that Google’s Scam Detection feature may soon be available on vivo smartphones, making vivo the third Android manufacturer to adopt this technology, following Google and Samsung. The feature, which uses on-device AI to identify potential scams during phone calls, has recently been introduced on the Samsung Galaxy S26 series. A teardown of the Phone by Google app revealed internal references to the codename “Sharpie,” linked to Scam Detection, suggesting its upcoming availability on vivo devices. While it is unclear which vivo models will support this feature, speculation points to the vivo X500 series as the likely first recipient, with the X300 series possibly following. It remains uncertain whether vivo will integrate Scam Detection into its own dialer app or use the Phone by Google app. The technology enhances user awareness by monitoring for suspicious patterns during calls, such as requests for payment via gift cards, and provides alerts for potential scams, excluding calls from saved contacts. The anticipated expansion of Scam Detection to vivo reflects a growing trend among Android manufacturers to enhance user safety against scams.
Search