Netherlands

AppWizard
October 2, 2026
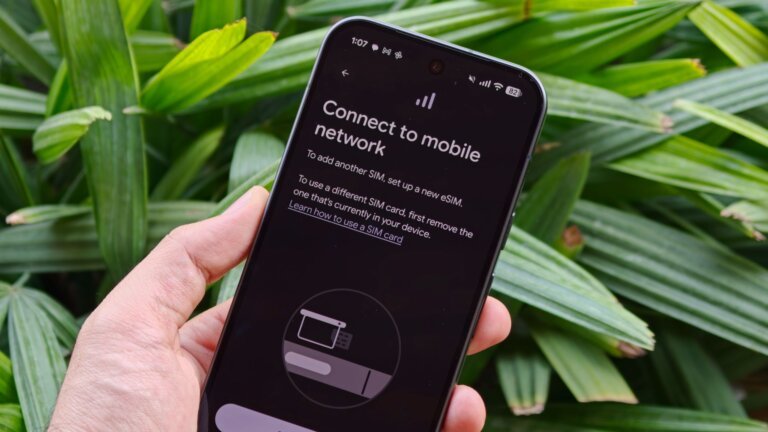
Opera has introduced its own eSIMs, allowing users to install them directly through the Opera browser for a data-only service tailored for travelers. Users can access a complimentary 3GB data package valid for three days post-activation in select countries, including the US, UK, Germany, France, Canada, UAE, Brazil, Netherlands, Norway, Sweden, and Poland, without needing to provide payment information or an email address. The eSIM service is built into the Opera browser for Android, requiring a device that supports eSIM hardware and runs on Android 10 or newer. Users can activate the service by navigating to their profile, selecting the eSIM option, and confirming their choice. Once the free package is used, additional data plans of 3GB, 5GB, or 10GB are available. The eSIM can be used across multiple countries, with activation occurring upon arrival in the selected country, although it is not available in Ukraine.
AppWizard
October 1, 2026
Opera has introduced a built-in eSIM feature in its Android browser, providing travelers with 3GB of complimentary mobile data for three days in select destinations. This feature allows users to connect essential applications without incurring roaming charges and is available in 47 destinations. Users can activate the eSIM before departure and purchase additional data packages after the complimentary allowance is used. Opera's eSIM plans are approximately 33% more affordable than those of six major competitors. The service supports 5G connectivity where available and requires Android 10 or later on unlocked phones. The free data service is currently accessible in the US, UK, Germany, France, Canada, UAE, Brazil, Netherlands, Norway, Sweden, and Poland.
AppWizard
September 29, 2026
Opera has integrated a travel eSIM into its Android browser, offering eligible users 3GB of free data without requiring credit card details. The eSIM can be managed within the Opera browser and is compatible across 47 destinations. Users must install the eSIM from the Opera app before traveling and can activate it upon arrival. To access the free eSIM, users need the latest version of the Opera browser and an Android phone that supports eSIM technology. The offer is available in several countries, including the U.S., U.K., Germany, France, Canada, UAE, Brazil, the Netherlands, Norway, Sweden, and Poland.
Winsage
September 25, 2026
The Dutch government is launching the Digitaal Autonome Werkomgeving Overheid (DAWO) initiative to create a self-sufficient digital environment, featuring a custom Linux-based operating system and IT suite. DAWO will be based on the Dutch Linux distribution NixOS and will include an office suite, collaboration applications, cloud services, and management tools, with a stable version expected by 2027. Other European countries, such as Denmark, Switzerland, and France, are also pursuing digital independence, with France transitioning 250 employees to Linux-based workstations using NixOS and promoting broader Linux adoption within state administration.
Winsage
September 24, 2026
Security researchers from Graz University of Technology in Austria have discovered significant vulnerabilities in the file notification systems of major operating systems: Android, Linux, macOS, and Windows. These flaws have existed for decades and can lead to the leakage of sensitive system information. The affected systems include inotify on Linux (since 2005), FileObserver on Android (since 2008), ReadDirectoryChangesW on Windows (since 2000), and FSEvents on macOS (since 2007). The vulnerabilities allow unprivileged users to monitor file events without explicit read permissions, enabling potential attacks such as inter-keystroke timing attacks and website fingerprinting. For example, on Linux, monitoring a readable directory can leak events on files that cannot be read, allowing attackers to achieve a 93.1% to 100% accuracy rate in monitoring keystrokes. Specific vulnerabilities include CVE-2025-68788 on Linux, which received a partial fix in December 2025, and issues on Android where FileObserver can bypass app storage isolation. On macOS, limited information is available due to a lack of bypasses for private directories, while on Windows, monitoring the root directory can reveal the full path of every accessed file, allowing real-time tracking of web activity with a 97.8% accuracy rate. Microsoft has described the issue as "by-design," which has faced criticism. The researchers propose stronger mitigations, such as disallowing monitoring of entire drives on Windows and introducing a permission system for file monitoring on Windows and macOS. Their findings will be presented at the ACM CCS 2026 conference in November in The Hague, Netherlands.
Tech Optimizer
September 16, 2026
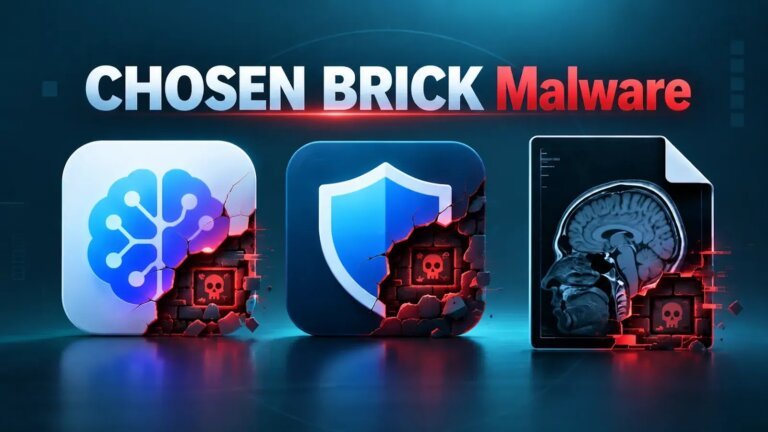
Iranian state-affiliated cyber actors are targeting dissidents, activists, and journalists using fake AI applications, counterfeit antivirus tools, and fabricated MRI scan results, primarily through a spyware family known as CHOSEN BRICK, which is designed for Windows systems. This campaign has been active since at least 2025 and affects individuals globally, including in the UK, US, and Netherlands. The malware establishes persistence via the Windows Registry Run key and communicates through Telegram, utilizing unique Bot IDs for each victim. CHOSEN BRICK is capable of extensive data collection, including capturing screenshots, recording audio, and stealing email content. Personal information from victims has been found on pro-Iranian leak sites, increasing harassment risks. Security measures should include monitoring for suspicious Registry entries and unusual communications, while users are advised to avoid unsolicited software installations and keep their systems updated. The FBI refers to this malware family as HEAVYGRAM.
Winsage
September 15, 2026
Iranian state cyber actors are targeting individuals through popular messaging applications, using surveillance and data-stealing malware known as "Chosen Brick," which has been in use since at least 2025. This malware is designed for Windows systems and enables the theft of personal data, allowing Iranian spies to monitor perceived threats such as dissidents, activists, and journalists. The attacks typically begin with messages sent via WhatsApp or Telegram, impersonating trusted contacts. Attackers conduct extensive research on their targets to craft convincing messages that encourage victims to download malicious files disguised as legitimate applications. Once executed, Chosen Brick operates stealthily, evading detection and establishing a connection for command-and-control communications. It can enumerate processes, capture screen and audio content, extract sensitive information, and even wipe infected systems. Organizations suspecting compromise are advised to engage IT providers for investigations and to inform staff about potential risks. Recent alerts follow cyberattacks on water and energy sectors linked to Iran, with ongoing concerns about the implications for cybersecurity amid escalating military tensions. Additionally, five US agencies have reported that attackers are using AI-generated scripts to exploit vulnerabilities in critical infrastructure systems.
AppWizard
September 15, 2026
On August 27, 2026, a class action lawsuit was filed in San Mateo County Superior Court by three California gamers—Alexander Shimota, Ricardo Camargo, and John Elliott—against Valve Corporation and ten video game publishers, accusing them of colluding to maintain uniform pricing for PC games across digital storefronts. The lawsuit alleges that Valve requires publishers on its Steam platform to agree to a most-favored-nation clause, preventing them from offering lower prices on competing platforms, which stifles competition and limits consumer choice. The ten implicated publishers include Activision Blizzard, Electronic Arts, and Sony Interactive Entertainment. The lawsuit is filed under California's Cartwright Act and claims that the coordinated pricing strategy harms consumers by reducing product diversity and inflating prices. Valve's commission structure, which has largely remained unchanged, is central to the plaintiffs' argument. Valve's co-founder, Gabe Newell, has previously denied dictating prices to third-party developers. The lawsuit is distinct from a prior case, Wolfire Games v. Valve, which focuses on monopoly abuse against developers rather than consumer pricing. Additionally, Valve faces a parallel £2 billion class action in the UK regarding similar pricing allegations. The outcome of these cases could significantly impact the pricing landscape for PC games and the practices of digital storefronts.
Winsage
August 17, 2026
A suspected advanced persistent threat (APT) group linked to China exploited a newly patched vulnerability in VMware vCenter (CVE-2026-59310), which has a critical CVSS score of 9.8, allowing for arbitrary code execution and the deployment of Babuk-derived ransomware. A recently patched vulnerability in Apple macOS (CVE-2026-65400) has been exploited to deploy a cryptocurrency miner, granting unauthorized root access. The Lazarus Group from North Korea exploited a zero-day vulnerability in Microsoft Windows, targeting defense and aerospace sectors. GeoServer patched a critical SQL injection vulnerability that was actively exploited. A new macOS malware, Amnesia Stealer, targets users through ClickFix attacks, stealing data and allowing real-time access to authenticated sessions. A novel attack technique named GhostSplice can manipulate AI coding assistants. Research revealed a method exploiting Chromium's DevTools Protocol for data theft. Noteworthy CVEs this week include CVE-2026-68820, CVE-2026-58231, and multiple others across various platforms. A high-severity command injection flaw in FileRun allows remote code execution. An advanced ClickFix attack has been reported, deploying sophisticated malware. A heap overflow vulnerability in Citrix NetScaler was patched after indications of exploitation. A new malware loader targeting Portuguese-speaking users has been identified. A significant reduction in exposed Automatic Tank Gauge systems has been observed. A phishing campaign targeting Brazil has been detected, and an F.B.I. agent faces charges for unauthorized crypto withdrawals. Authorities in Ukraine dismantled fraudulent call centers, and a North Carolina man was sentenced for cyber extortion. Unauthorized access to sensitive data by the ExfilSquad group has been confirmed. LightSpy activity linked to China has been detected in over 13 countries. A supply chain attack exposed over 2,500 companies, and an Azure exfiltration campaign has exposed millions of enterprise records.
AppWizard
July 3, 2026
The Consumer Competition Claims Foundation (CCC), a Dutch nonprofit organization, has filed a class action claim against Valve, alleging that the company's practices are stifling competition in the PC gaming market and inflating game prices. The CCC claims that Valve enforces price-parity agreements through contracts and peer pressure, preventing game developers from offering lower prices on competing platforms. They argue that Valve's 30% commission on sales restricts studios from setting their own prices, leading to higher costs for consumers. The CCC is also concerned about Valve's requirement for microtransactions to go through the Steam Wallet, which incurs an additional 30% commission, and the practice of region-locking keys. They are seeking €220 million in damages for affected Dutch players. The CCC is currently exploring an amicable resolution with Valve and is encouraging individuals to support their cause by signing up on the GameClaim website. The CCC's claims extend beyond direct Steam purchases, affecting the entire market. The likelihood of a successful lawsuit is uncertain, as the CCC has a mixed track record in previous cases. Valve has faced legal challenges in the past, including a penalty in 2016 for misleading consumer representations, and ongoing lawsuits regarding its market dominance.
Search