operators

Tech Optimizer
September 28, 2026
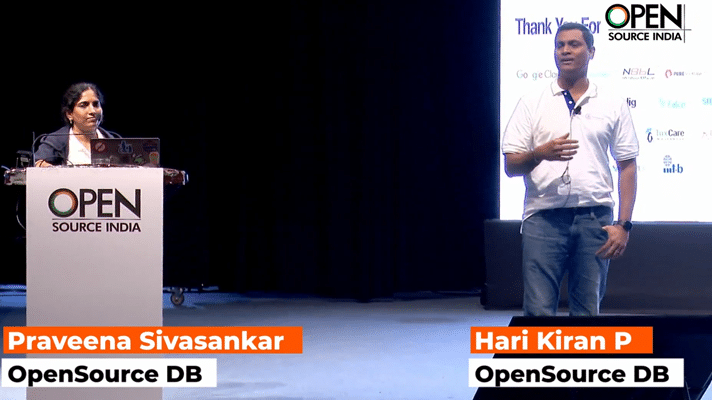
Postgres Women India was launched in 2023 as a corporate social responsibility initiative under OpenSource DB, starting with 10 members and growing to over 2000 women across more than 70 countries. The community addresses the underrepresentation of women in open source and database conferences, aiming to empower, connect, and celebrate women in technology. Its core pillars include community building, nurturing future leaders, and advocating for education. The community organizes virtual and in-person meetups, mentorship programs, and collaborates with universities to enhance skills in database technologies. Key initiatives include a Career Connect Day, intensive upskill programs, and the Women for Data Summit. The community has recognized 18 women as ‘Postgres Women of the Month’ and highlighted emerging contributors. Partnerships with organizations like Google and YugaByteDB support its efforts, and it seeks further community involvement to establish local chapters and host events.
AppWizard
September 25, 2026
Warzone has introduced a "cosmetic toggle" that allows players to disable legacy character skins at a client level, specifically for Warzone, while Modern Warfare 4 will not carry over any cosmetics from previous titles. This feature aims to address concerns about mismatched crossover skins and create a more cohesive gaming experience. The toggle is a response to previous commitments to avoid old skins, although collaborations have complicated this effort. Its effectiveness may diminish with the introduction of new characters in future seasons, and its future depends on Infinity Ward's commitment to aesthetic integrity and potential expansions of the toggle.
AppWizard
September 19, 2026
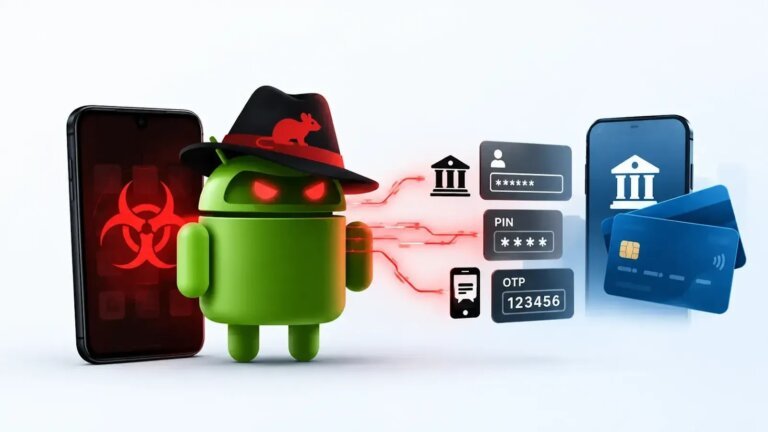
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
AppWizard
September 17, 2026
Security researchers at Zimperium have identified a new strain of Android malware called RatHat, which is linked to threat actors from China and is designed to steal sensitive credentials and banking information. RatHat infiltrates devices through phishing sites, malvertising, and SMS phishing (smishing), tricking users into downloading malicious Android package kits (APKs). The malware uses a dropper to activate its payload, which is hidden in encrypted assets, and employs techniques to bypass Android's security measures. RatHat consists of three main components: a malicious Android application, a Go agent (liblocal-service.so), and an FRP client (libmedia_codec.so). The app collects sensitive information such as banking credentials, notifications, 2FA codes, OTP keys, and screen inputs. It features a generative AI user interface-automation engine that communicates in Mandarin and can perform various tasks like determining screen coordinates and issuing navigation commands. The Go agent acts as a command-and-control executor, executing commands to bypass app-level security and manage system-level tasks. The FRP client maintains a secure reverse tunnel to the attacker's server, allowing ongoing remote access to the device. The architecture of RatHat demonstrates the inadequacy of traditional mobile security measures against such advanced threats.
Search