overflow

TrendTechie
October 10, 2026
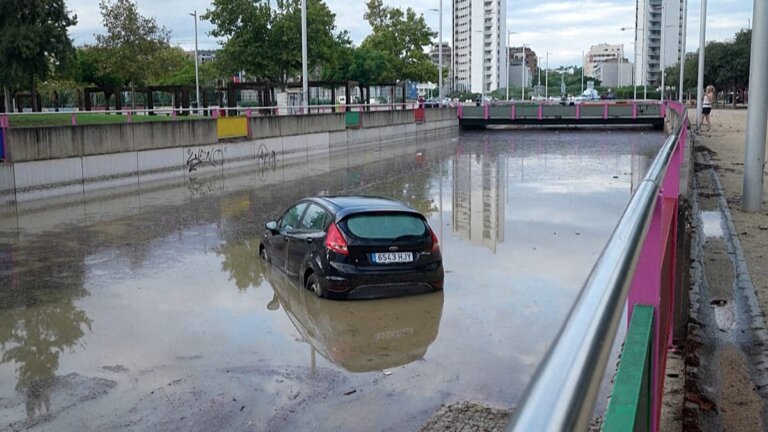
In Torrent, a city with approximately 85,000 residents, severe flooding has caused streets to be covered in mud, damaging several vehicles and trapping 15 individuals in a fast-food restaurant, who were rescued by emergency services. Residents expressed frustration over the lack of engineering measures to prevent such flooding and raised concerns about the delayed warning from the Spanish emergency alert system, ES-Alert, which was issued after significant flooding had already occurred. The flooding followed torrential rains, with nearly 96 liters of rainfall recorded, including 71 liters in just 30 minutes. The Barranco del Poyo ravine and nearby town of Paiporta were also affected, although the stream did not overflow. Emergency crews are working to clear damaged roads and vehicles.
Winsage
October 6, 2026
Microsoft Distinguished Engineer David Fowler addressed a viral post on social media that dismissed Windows as a viable operating system for developers, asserting that Windows is the most widely used operating system among developers. According to Stack Overflow’s 2025 Developer Survey, Windows is preferred by 49.5% of professional developers, while macOS is at 32.9% and Ubuntu at 27.7%. WSL accounted for 16.8%, and Linux outside of WSL garnered 16.7%. In contrast, a poll by The Pragmatic Engineer indicated Windows usage among developers at only 12%, with macOS at 61.6% and Linux at 24.2%. The appeal of Unix tooling is significant for web, cloud, backend, and AI developers, while Windows remains popular among .NET and C# developers, Visual Studio users, and game developers. Microsoft is enhancing its Windows Subsystem for Linux (WSL) to better cater to developers' needs.
Tech Optimizer
September 28, 2026
Spinnaker Support has launched a suite of PostgreSQL support and migration services to help organizations reduce their reliance on Oracle databases. The services include enterprise software support for PostgreSQL and migration services facilitated by HexaCluster, allowing customers to maintain their Oracle environments while transitioning workloads to PostgreSQL. Spinnaker is also developing an enterprise distribution for PostgreSQL, built around standard PostgreSQL and open-source components. The support package includes break-fix support, troubleshooting, security guidance, performance and configuration support, and lifecycle guidance. The migration service analyzes Oracle database dependencies, automates parts of the conversion process, validates production readiness, and facilitates controlled cutovers. The HexaRocket platform from HexaCluster aids in migration, data movement, and replication. The launch aligns with a trend of organizations reassessing database expenditures, with 55.6% of developers using PostgreSQL according to the 2025 Stack Overflow Developer Survey. Spinnaker aims to enhance its role in enterprise infrastructure decisions by supporting both Oracle and PostgreSQL environments. Martin Biggs has been appointed Vice President and General Manager of the PostgreSQL Practice, overseeing PostgreSQL support and migration services. Spinnaker's PostgreSQL offerings are part of its Run, Optimize, Transform framework, designed to help customers manage current systems and plan for long-term changes.
AppWizard
September 27, 2026
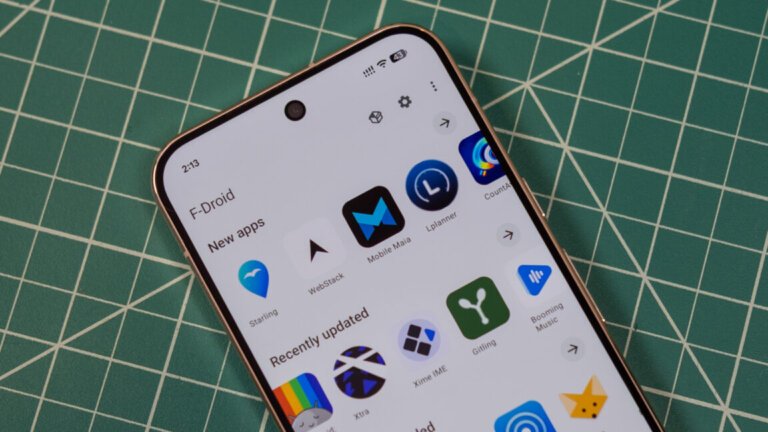
F-Droid has released version 2.0 of its official Android app, marking the most substantial update in a decade after over a year of development and 14 test builds. The app has been reconstructed using Kotlin and Jetpack Compose, aligning it with Android’s Material Design principles and improving maintenance and feature expansion. Navigation is simplified into three sections: Discover, Search, and My Apps. The Discover section showcases new apps, updates, and popular downloads, while categories have been refined for easier access to specific software types. The search functionality has been enhanced to allow users to filter by application names, descriptions, categories, and languages. F-Droid 2.0 now automatically checks for and installs updates, with manual controls still available. Recent changes in the Android platform enable smoother installation experiences for alternative app stores. Privacy features have been updated, but the F-Droid Privileged Extension is not supported in this version, and the app-wiping capability has not returned.
AppWizard
September 25, 2026
F-Droid is a community-driven repository for free and open source Android applications, recently undergoing a transformation with the release of F-Droid 2.0. The new client is redesigned using Kotlin Compose, enhancing responsiveness and introducing optional Material theming for a visually appealing interface. The update simplifies app discovery and installation, now offering a vast library of thousands of open source applications. F-Droid prioritizes user autonomy without tracking behavior for ads. It features extensive categories for specialized needs and improved search functionality that returns results based on app names and descriptions. Installation has been streamlined using Google’s pre-approval API, allowing users to confirm installations through a simplified pop-up, improving the user experience despite requiring one additional click compared to the Play Store.
Winsage
September 10, 2026
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has expanded its Known Exploited Vulnerabilities (KEV) catalog, adding critical vulnerabilities that need immediate attention. 1. CVE-2026-75650: A vulnerability in Adobe Commerce and Magento with a CVSS score of 10.0, allowing unauthenticated remote code execution. Affected versions include Magento Open Source releases 2.4.7, 2.4.8, and 2.4.9. It has been actively exploited since September 4. 2. CVE-2026-81963: A Microsoft Windows vulnerability with a CVSS score of 7.8, related to a link-following issue within the Update Stack, allowing local attackers to escalate privileges. It is currently being exploited. 3. CVE-2026-85880: Another Microsoft Windows vulnerability rated at 7.8, involving a heap-based buffer overflow in the ALPC component, permitting local privilege escalation. This flaw is also actively exploited. 4. CVE-2026-86218: A N-able N-central vulnerability with a CVSS score of 10.0, allowing pre-authenticated remote code execution. N-able has released an emergency hotfix for this issue. Federal agencies must address these vulnerabilities by specified deadlines: Windows flaws by September 22 and other vulnerabilities by September 11, 2026, in accordance with Binding Operational Directive (BOD) 22-01. Private organizations are advised to review the KEV catalog and take necessary actions to strengthen their infrastructure against these vulnerabilities.
Winsage
September 10, 2026
On September 8, 2026, Microsoft released 966 security updates, the largest Patch Tuesday to date, addressing various vulnerabilities. Among these, 105 were classified as critical, including two zero-day vulnerabilities: CVE-2026-81963 and CVE-2026-85880. Both allow authorized local attackers to escalate privileges to SYSTEM level. CVE-2026-81963 is related to the Windows Update Stack, while CVE-2026-85880 involves a heap-based buffer overflow in the Windows Advanced Local Procedure Call (ALPC). The updates included 438 vulnerabilities related to privilege escalation, 258 concerning remote code execution, and 173 involving information disclosures. Users are advised to prioritize the installation of these updates due to the potential exploitation of the two critical vulnerabilities.
Winsage
September 10, 2026
Microsoft's Patch Tuesday on September 8, 2026, addressed two critical Windows privilege escalation vulnerabilities: CVE-2026-85880 and CVE-2026-81963, both with a CVSS score of 7.8. CVE-2026-85880 is a heap-based buffer overflow in the Windows Advanced Local Procedure Call (ALPC), allowing attackers with low-privilege local access to escalate privileges to SYSTEM. CVE-2026-81963 involves improper link resolution in the Windows Update Stack, enabling similar privilege escalation. Both vulnerabilities require no user interaction and have been actively exploited prior to the patch release. CISA added them to its Known Exploited Vulnerabilities catalog on September 8, 2026, with a remediation deadline of September 22 for U.S. federal agencies. CVE-2026-85880 affects various Windows 10 and Server versions but excludes Windows 11 and Windows Server 2025. CVE-2026-81963 impacts newer Windows platforms, including Windows 11 and Windows Server 2025. Microsoft released security updates for both vulnerabilities on September 8, 2026, and organizations are advised to prioritize these updates. Security teams should monitor for signs of privilege escalation and unusual SYSTEM-level activities related to these vulnerabilities.
Winsage
September 9, 2026
Recent investigations have identified the BlueMoon exploit kit, used by espionage-driven threat activity clusters, particularly linked to APT31, a China-aligned state-sponsored group, since August 28, 2026. BlueMoon exploits three vulnerabilities: CVE-2026-85046 (a type confusion vulnerability in Google Chrome's V8 engine), an unassigned V8 sandbox escape, and CVE-2026-85880 (a heap-based buffer overflow in Windows ALPC). Google and Microsoft have released patches for these vulnerabilities, which were exploited as "patch-gap" zero-days. The attack vectors typically begin with phishing emails that lead victims to malicious URLs, triggering the vulnerabilities for code execution and privilege escalation. Variants of BlueMoon have been detected, featuring modifications for specific campaigns. Notable attack chains include: - APT31 targeting NGOs and mining firms in the U.S. with a malicious browser add-on called GemStone. - UNK_LateNight targeting U.S. aerospace companies, deploying BlueMoon alongside the ShadowPad backdoor. - UNK_DoubleCheck targeting a Vietnamese manufacturer, using DLL sideloading to execute a Rust binary. - UNK_QuietRacket targeting government and financial organizations in Indonesia and Singapore, modifying BlueMoon to execute a .NET assembly. CISA added the Chrome flaw to its Known Exploited Vulnerabilities catalog on September 4, 2026, requiring federal agencies to apply patches by September 18, 2026. Indicators of compromise include specific process trees, files, folders, scheduled tasks, mutexes, and registry keys. Proofpoint has released detection rules to help organizations identify and mitigate these threats.
Winsage
September 9, 2026
Microsoft addressed 974 vulnerabilities in its software suite during its recent Patch Tuesday, marking a record high. The breakdown includes 723 flaws in Windows, 111 in Office, 62 in SQL, and 22 in Developer Tools, with over 110 rated as critical. Two actively exploited vulnerabilities are CVE-2026-85880 and CVE-2026-81963, both allowing local privilege elevation. Other notable vulnerabilities include CVE-2026-55007 (8.1), CVE-2026-80097 (8.6), CVE-2026-69465 (8.8), and several with CVSS scores of 9.6 and above. Microsoft has patched a total of 2,760 security flaws this year, reflecting a trend of increasing vulnerability discoveries. Despite the extensive patching, no significant spike in active exploits has been observed.
Search