overlays

AppWizard
September 22, 2026
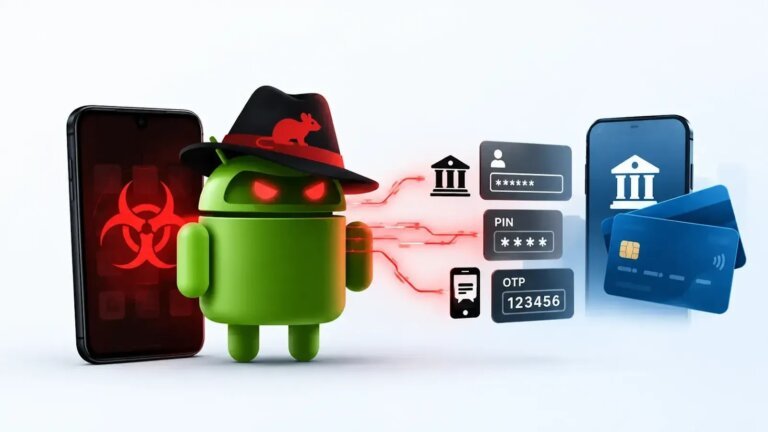
Cybersecurity researchers at Zimperium have identified a new strain of malware called RatHat, targeting Android devices and linked to threat actors from China. RatHat uses generative AI to maintain persistence and control over infected devices. The malware is typically spread through social engineering, tricking users into downloading counterfeit applications that appear legitimate. Once installed, RatHat requests accessibility permissions, activates Wireless Debugging, and can capture text messages, create overlays, and steal passwords and multi-factor authentication codes. Its AI capabilities allow it to navigate the device interface in real-time, making detection by security software more difficult. To protect against RatHat, users should avoid downloading apps from untrustworthy sources, and removal requires a factory reset of the device.
AppWizard
September 19, 2026
Security researchers have identified an Android banking Trojan named RatHat, which utilizes artificial intelligence, accessibility features, and Android Debug Bridge (ADB) to steal financial credentials, PINs, and one-time passcodes. Unlike traditional malware, RatHat employs a live AI assistant that interacts with the Android accessibility tree, allowing it to make real-time decisions based on the victim's screen content. The infection typically starts with social-engineering tactics, leading victims to counterfeit download pages where they are tricked into sideloading a malicious APK. Once installed, RatHat prompts users to enable Android Accessibility Service permissions, which it exploits to navigate Developer Options and enable Wireless Debugging. This grants it shell-level ADB access, allowing it to bypass application sandbox restrictions. RatHat deploys two native binaries for executing commands and maintaining a connection to the attacker's infrastructure. It targets banking applications through credential-stealing overlays and can intercept SMS messages for transaction verification codes. Additionally, it can record touch coordinates to reconstruct PINs and unlock patterns. RatHat includes persistence mechanisms to restore itself after removal, and users are advised to perform a factory reset if they suspect compromise. To reduce infection risk, users should avoid sideloading apps from unknown links, deny unnecessary Accessibility Service requests, and refrain from enabling Developer Options or Wireless Debugging for unfamiliar applications.
Winsage
September 17, 2026
Mark Russinovich, the Chief Technology Officer of Microsoft Azure, transitioned ZoomIt, a Windows tool for screen zooming, recording, and annotation, to macOS using artificial intelligence. Originally developed to aid in teaching Windows Internals, ZoomIt has been enhanced over the years with features like screen recording and webcam overlays. Despite initial reluctance due to time constraints, Russinovich utilized AI to create a functional macOS version in just two days, significantly faster than anticipated. The AI model leveraged the original Windows code, allowing for a high-fidelity clone of ZoomIt that includes essential features. ZoomIt for macOS is now available as a free and open-source tool, requiring macOS 14 Sonoma or newer, and can be installed via Homebrew or from Microsoft’s GitHub repository. Users can access its functionalities through keyboard shortcuts and a menu bar icon.
AppWizard
August 23, 2026
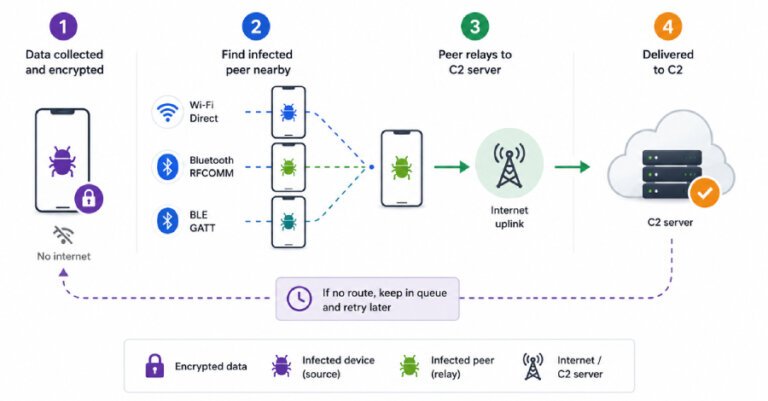
A new Android malware threat, codenamed Manic, poses significant risks to Ukrainian banks, government services, and messaging applications, with a reach extending to Russian and European financial institutions, global fintech platforms, cryptocurrency services, and military communication channels. Manic combines Android banking malware and mobile spyware, targeting sensitive applications and enabling comprehensive device takeover. It features a novel Wi-Fi mesh technique for data relay through compromised devices and utilizes phishing sites and dropper apps. The malware originated in February 2026, with initial development leading to its first deployment by late May. It monitors 169 package IDs related to banks, payment services, and messaging applications, primarily affecting Ukrainian targets but also impacting applications in Russia and Europe. Manic can infiltrate commercial and military messaging apps, track locations, monitor notifications, and collect files. It exploits Android's accessibility services to capture sensitive data and employs a store-and-forward relay mechanism for data exfiltration through nearby compromised devices. Google has stated that no apps containing this malware are found on Google Play, and Android users are protected by Google Play Protect.
Winsage
August 10, 2026
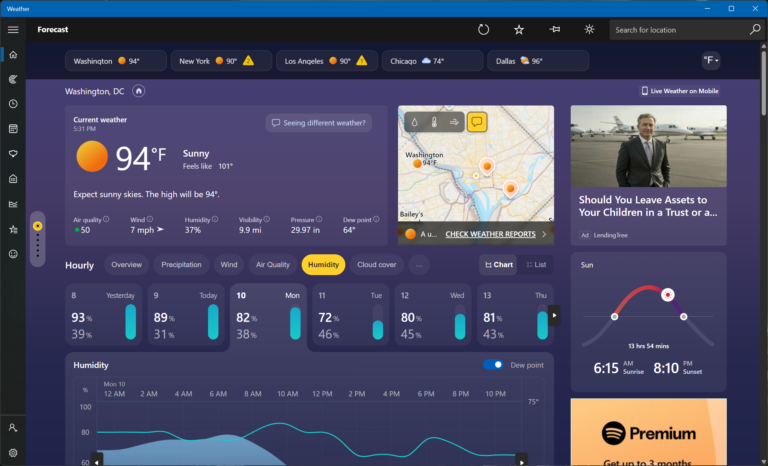
Microsoft is addressing issues related to user dissatisfaction with its Windows operating system, which has faced criticism for lack of optimization, excessive bloat, and intrusive advertisements. The built-in weather application, MSN Weather, exemplifies these problems, consuming up to 1.2GB of RAM while idling and displaying ads despite being part of a paid OS. In contrast, Apple's macOS weather app uses about 250MB of memory and operates ad-free. MSN Weather functions as a web wrapper, utilizing eight Chromium-based subprocesses, which raises concerns about its efficiency. Microsoft plans to update all native Windows applications to the Win32 standard for better optimization, but it is unclear if this will also apply to MSN-branded services like MSN Weather. Users have shown a preference for mobile devices over the weather widget introduced in Windows 11.
Search