Patch

Winsage
September 15, 2026
Microsoft has released an emergency patch for Windows 11, identified as KB5129195, which is being automatically downloaded to address critical issues, including privilege elevation vulnerabilities. The patch fixes CVE-2026-62721 and resolves remote desktop connection problems, as well as attempts to address USB audio issues that arose after the September update. Improvements have been noted for 8-channel and 3D audio modes, but users may still face problems such as missing volume controls and lack of audio output for some USB audio devices. Additionally, unresolved issues from the September update, KB5124008, persist, particularly for AMD Radeon GPU users experiencing system freezes, crashes, and driver timeouts. Complaints about File Explorer crashing or failing to launch have also been reported, affecting certain enterprise environments. Microsoft is using internal AI tools to enhance security, but this has led to a cycle of instability in the operating system. Nearly 1,000 CVE patches were applied just before this update.
Winsage
September 15, 2026
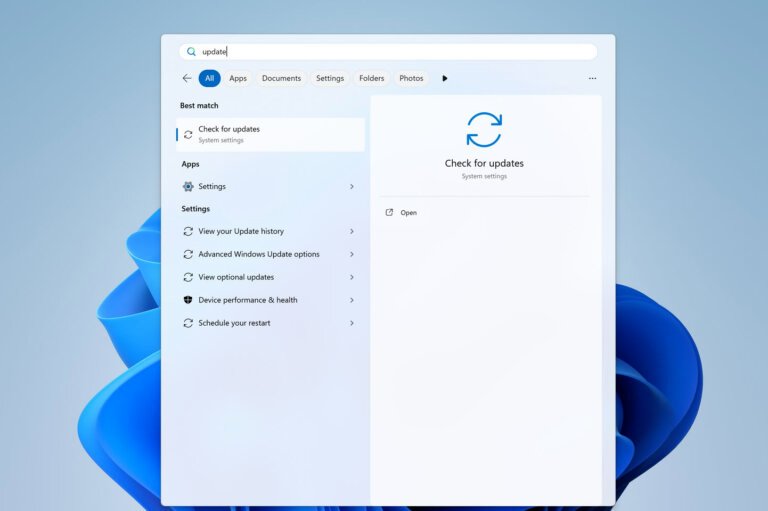
Microsoft has released out-of-band updates for Windows 11 versions 26H1, 25H2, and 24H2 to address security vulnerabilities and improve system performance. The KB5129194 patch for version 26H1 fixes a critical elevation-of-privilege vulnerability (CVE-2026-62721) related to the Windows User-Mode Power Service (UMPS). The KB5129195 update for versions 25H2 and 24H2 also addresses a similar UMPS vulnerability and resolves a connection issue with Remote Desktop Services. Additionally, the updates fix problems with multichannel audio features on certain USB Audio Class 1.0 devices. These updates include enhancements from the September 2026 Patch Tuesday release, such as Taskbar customization, a faster Windows Search experience, and new Start Menu options. Users with unmanaged PCs will receive these updates automatically but can also check for updates manually.
Winsage
September 15, 2026
A spear-phishing campaign linked to the Chinese threat actor UTA0560 targeted various NGOs on September 1, 2026, exploiting recently patched vulnerabilities in Google Chrome and Microsoft Windows. The campaign utilized a malicious JavaScript backdoor called GRIMWEDGE, which was deployed through a multi-stage exploit chain that involved three vulnerabilities: CVE-2026-85046, CVE-2026-87491, and CVE-2026-85880. The attack began with spear-phishing emails that led recipients to a vulnerable U.S.-based university website, allowing attackers to redirect users to their infrastructure. The exploit chain enabled arbitrary code execution and facilitated the deployment of GRIMWEDGE, which is capable of host reconnaissance, file and process management, command execution, and payload delivery. The initial payload was an executable named "msgbox.exe," which extracted a legitimate Windows binary and a malicious DLL called "wsc.dll." This DLL initiated a sideloading chain and contacted a command-and-control server for further instructions. GRIMWEDGE allows for several commands, including system reconnaissance, directory listing, file deletion, and command execution in a hidden window. It lacks built-in persistence or lateral movement mechanisms but provides a foothold for further exploitation. Concurrently, another Chinese threat actor, JungleBamboo (APT31), used the same exploit chain to deploy a loader named SUPERSTOMP, which installs a credential-stealing Chrome extension called LONGTALE. The simultaneous use of the exploit chain by multiple actors suggests potential sharing or sale of the exploit, raising concerns about patch-gap vulnerabilities that pose risks for exploitation campaigns.
Winsage
September 14, 2026
Windows 11 update KB5124008, released on September 8, has caused significant audio issues for users, including failure of audio devices to initialize or produce sound, and problems with microphones and multichannel audio. The update is linked to Explorer.exe crashes, disruptions in File History backups, Remote Desktop difficulties, and GPU issues on certain AMD systems. Microsoft has acknowledged these problems and indicated that the audio issues primarily affect USB Audio Class 1.0 devices. Users may see error logs in Device Manager indicating "This device cannot start (Code 10)." A temporary workaround is to switch to a 2-channel mode, and wireless audio devices appear to be unaffected. Microsoft is working on a permanent solution.
AppWizard
September 14, 2026
The 3.0 patch for Warcraft 3: Reforged has introduced the Forsaken Kingdom expansion, which includes bug fixes and new features. A significant change is the requirement for an internet connection to play, even in single-player mode, which removes local area network (LAN) functionality. Blizzard has provided access to the legacy Warcraft 3 client with the purchase of Reforged, allowing offline play and LAN support. The patch also adds a new graphics mode for improved visual fidelity and doubles the unit selection cap from 12 to 24. Full patch notes are available on the Blizzard forums.
Winsage
September 12, 2026
Windows 11 KB5124008, released on September 8, has caused various issues, including disruptions to WSL-based applications and Remote Desktop sessions. Users have reported problems with File History backups and instability in Explorer.exe, leading to system and GPU crashes. Microsoft confirmed a bug affecting applications using HCS-managed Linux virtual machines, particularly Claude Cowork, which is experiencing connectivity issues. Remote Desktop Services (RDS) are malfunctioning, leading to connection failures and sign-in problems. Additionally, some users face black screens upon sign-in due to Explorer.exe crashes. Reports indicate that File History is not recognizing external backup drives, and serious GPU issues have been reported on AMD Radeon systems, including driver timeouts and system freezes.
Tech Optimizer
September 12, 2026
If you hold Microsoft 365 E5, you already have access to Microsoft Defender for Endpoint, which provides enterprise-grade endpoint protection at no additional cost. For organizations without a dedicated security specialist, Sophos is recommended. CrowdStrike is suitable for those with a mature Security Operations Center (SOC) and sufficient budget. Other options include SentinelOne for mid-sized organizations needing automation, ESET for older hardware and virtual desktops, Avast Business for very small businesses without IT staff, VIPRE for budget-conscious organizations, and Expel for tool-agnostic managed detection and response. It is essential to assess your organization's current situation honestly when evaluating endpoint protection options. Antivirus and EDR are now essentially the same agent, and organizations should inquire about update staging processes and review independent tests for protection rates. Coverage for servers and Linux environments is often overlooked but crucial, as Linux servers are prime targets for ransomware. Key recommendations include: - Microsoft Defender for Endpoint for organizations already on Microsoft 365 E5. - Sophos for organizations with 25-500 staff relying on IT generalists. - CrowdStrike for enterprises with a well-funded security operations function. - SentinelOne for mid-sized organizations needing autonomous operation. - ESET for organizations with older hardware or virtual desktop infrastructure. - Avast Business for micro and small businesses. - VIPRE for budget-conscious organizations. - Expel for those seeking managed detection across various environments. During deployment, avoid running two real-time agents simultaneously, ensure prevention features are activated, and test on line-of-business applications first. Verify update staging and rollback procedures with vendors, and confirm whether Microsoft licensing covers your needs to avoid unnecessary purchases.
Search