permission requests

AppWizard
September 14, 2026
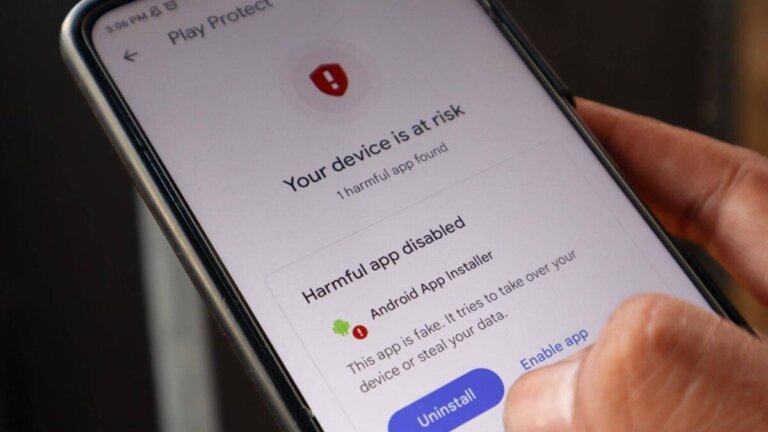
Malicious Android applications are being promoted through social media advertisements, particularly on platforms like Instagram and Facebook, posing significant risks to users. The Indian Cyber Crime Coordination Centre (I4C) has warned about deceptive apps advertised under names such as Night Play, Reloop, Kyss, Vimo, Rivo, Nezo, and Vixa, which often redirect users to pornographic websites to download APK files. These applications can exploit sensitive device permissions, leading to malware infections, unauthorized financial transactions, and various forms of cyber fraud. Users may be tricked into granting accessibility permissions that allow the malware to operate in the background and potentially install a VPN, rerouting internet traffic through servers controlled by attackers. Cybersecurity experts advise users to verify the legitimacy of applications before installation and to be cautious of permissions requested by unknown apps.
AppWizard
September 14, 2026
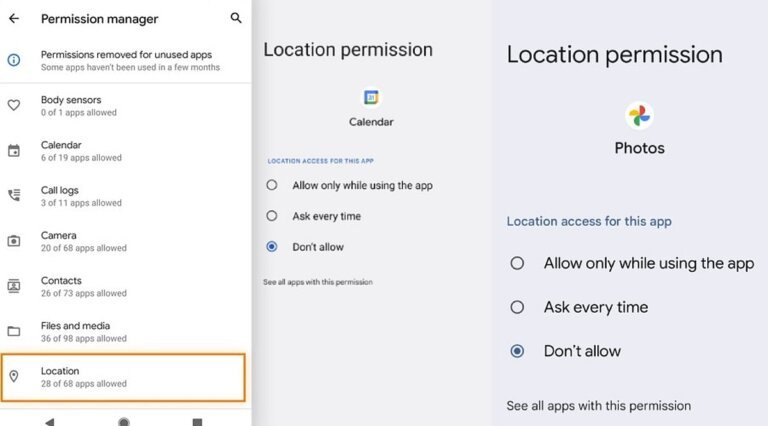
Permissions in Android apps should be granted based on their relevance to the app's primary function. Users should be cautious with permissions such as location, contacts, SMS, microphone, camera, and accessibility access, as they can expose sensitive information or control device capabilities. To review app permissions, users can navigate to Settings, select Apps, choose the application, and tap on Permissions. The Permission Manager under Security & Privacy allows users to see which apps have access to specific permissions. Android can automatically pause activity for seldom-used apps, removing previously granted permissions. If an app repeatedly requests denied permissions, users should evaluate the necessity of the request and consider maintaining their denial if it seems unwarranted.
Tech Optimizer
August 17, 2026
The landscape of mobile security has shifted away from traditional third-party antivirus software, as modern Android devices are equipped with built-in security features. Key components of this security framework include Google Play Protect, which blocked 27 million malicious apps in 2025; application sandboxing that isolates apps; proactive permissions that enhance user privacy; AI-powered threat detection for sophisticated attacks; and strict sideloading policies to limit risks from off-market malware. Despite these defenses, threats such as social engineering, phishing, malicious push notifications, and unsecured public Wi-Fi remain prevalent, often evading traditional antivirus solutions. However, certain scenarios, such as frequent sideloading, using older devices, connecting to public Wi-Fi, or suspected infections, may warrant the use of third-party antivirus apps for additional protection. Overall, the built-in security features of Android provide a strong defense for most users, with user education being crucial for effective smartphone protection.
AppWizard
August 4, 2026
A recent analysis by DoubleVerify engineers has identified a trend in mobile advertising known as AfterCall ads, where applications display advertisements immediately after a phone call ends. This practice generates hundreds of millions of impressions monthly and raises concerns about user experience and brand integrity. AfterCall applications operate using three components: a misleading permission, a Broadcast Receiver to capture end-of-call events, and an Activity to display ads. The SYSTEMALERTWINDOW permission allows these apps to show content over others, often granted under false pretenses. They utilize Android's telephony system to trigger ads post-call and employ tactics to obscure their presence, such as removing themselves from the recent apps list and using innocuous icons. Detection is challenging due to the lack of shared codebases and the obfuscation techniques used. The scale of the issue is significant, with numerous AfterCall applications identified monthly, negatively impacting user experience and raising concerns for advertisers.
Search